

Microsoft SC-100テストエンジン練習テスト問題、試験問題集
100%無料SC-100日常練習試験には298問があります
マイクロソフトSC-100試験を受けることの利点の1つは、世界中の雇用主や組織に認められていることです。この試験は、サイバーセキュリティの専門家のためのグローバルに認知された認定である「Microsoft Certified: Security, Compliance, and Identity Fundamentals」の一部であり、マイクロソフトSC-100試験に合格することで、個人はサイバーセキュリティアーキテクチャの専門知識を示し、この分野での雇用の可能性を高めることができます。
質問 # 13
You need to recommend a solution to meet the requirements for connections to ClaimsDB.
What should you recommend using for each requirement? To answer, select the appropriate options in the answer area.
NOTE: Each correct selection is worth one point.
正解:
解説:
Topic 1, Fabrikam, Inc Case Study 1
OverView
Fabrikam, Inc. is an insurance company that has a main office in New York and a branch office in Paris.
On-premises Environment
The on-premises network contains a single Active Directory Domain Services (AD DS) domain named corp.
fabrikam.com.
Azure Environment
Fabrikam has the following Azure resources:
* An Azure Active Directory (Azure AD) tenant named fabrikam.onmicrosoft.com that syncs with corp.
fabnkam.com
* A single Azure subscription named Sub1
* A virtual network named Vnet1 in the East US Azure region
* A virtual network named Vnet2 in the West Europe Azure region
* An instance of Azure Front Door named FD1 that has Azure Web Application Firewall (WAR enabled
* A Microsoft Sentinel workspace
* An Azure SQL database named ClaimsDB that contains a table named ClaimDetails
* 20 virtual machines that are configured as application servers and are NOT onboarded to Microsoft Defender for Cloud
* A resource group named TestRG that is used for testing purposes only
* An Azure Virtual Desktop host pool that contains personal assigned session hosts All the resources in Sub1 are in either the East US or the West Europe region.
Partners
Fabrikam has contracted a company named Contoso, Ltd. to develop applications. Contoso has the following infrastructure-.
* An Azure AD tenant named contoso.onmicrosoft.com
* An Amazon Web Services (AWS) implementation named ContosoAWS1 that contains AWS EC2 instances used to host test workloads for the applications of Fabrikam Developers at Contoso will connect to the resources of Fabrikam to test or update applications. The developers will be added to a security Group named Contoso Developers in fabrikam.onmicrosoft.com that will be assigned to roles in Sub1.
The ContosoDevelopers group is assigned the db.owner role for the ClaimsDB database.
Compliance Event
Fabrikam deploys the following compliance environment:
* Defender for Cloud is configured to assess all the resources in Sub1 for compliance to the HIPAA HITRUST standard.
* Currently, resources that are noncompliant with the HIPAA HITRUST standard are remediated manually.
* Qualys is used as the standard vulnerability assessment tool for servers.
Problem Statements
The secure score in Defender for Cloud shows that all the virtual machines generate the following recommendation-. Machines should have a vulnerability assessment solution.
All the virtual machines must be compliant in Defender for Cloud.
ClaimApp Deployment
Fabrikam plans to implement an internet-accessible application named ClaimsApp that will have the following specification
* ClaimsApp will be deployed to Azure App Service instances that connect to Vnetl and Vnet2.
* Users will connect to ClaimsApp by using a URL of https://claims.fabrikam.com.
* ClaimsApp will access data in ClaimsDB.
* ClaimsDB must be accessible only from Azure virtual networks.
* The app services permission for ClaimsApp must be assigned to ClaimsDB.
Application Development Requirements
Fabrikam identifies the following requirements for application development:
* Azure DevTest labs will be used by developers for testing.
* All the application code must be stored in GitHub Enterprise.
* Azure Pipelines will be used to manage application deployments.
* All application code changes must be scanned for security vulnerabilities, including application code or configuration files that contain secrets in clear text. Scanning must be done at the time the code is pushed to a repository.
Security Requirement
Fabrikam identifies the following security requirements:
* Internet-accessible applications must prevent connections that originate in North Korea.
* Only members of a group named InfraSec must be allowed to configure network security groups (NSGs} and instances of Azure Firewall, VJM. And Front Door in Sub1.
* Administrators must connect to a secure host to perform any remote administration of the virtual machines.
The secure host must be provisioned from a custom operating system image.
AWS Requirements
Fabrikam identifies the following security requirements for the data hosted in ContosoAWSV.
* Notify security administrators at Fabrikam if any AWS EC2 instances are noncompliant with secure score recommendations.
* Ensure that the security administrators can query AWS service logs directly from the Azure environment.
Contoso Developer Requirements
Fabrikam identifies the following requirements for the Contoso developers;
* Every month, the membership of the ContosoDevelopers group must be verified.
* The Contoso developers must use their existing contoso.onmicrosoft.com credentials to access the resources in Sub1.
* The Comoro developers must be prevented from viewing the data in a column named MedicalHistory in the ClaimDetails table.
Compliance Requirement
Fabrikam wants to automatically remediate the virtual machines in Sub1 to be compliant with the HIPPA HITRUST standard. The virtual machines in TestRG must be excluded from the compliance assessment.
質問 # 14
You are planning the security requirements for Azure Cosmos DB Core (SQL) API accounts. You need to recommend a solution to audit all users that access the data in the Azure Cosmos DB accounts. Which two configurations should you include in the recommendation? Each correct answer presents part of the solution. NOTE: Each correct selection is worth one point.
- A. Enable Microsoft Defender for Cosmos DB.
- B. Send the Azure Cosmos DB logs to a Log Analytics workspace.
- C. Enable Microsoft Defender for Identity.
- D. Send the Azure Active Directory (Azure AD) sign-in logs to a Log Analytics workspace.
- E. Disable local authentication for Azure Cosmos DB.
正解:D、E
解説:
https://docs.microsoft.com/en-us/azure/cosmos-db/audit-control-plane-logs
質問 # 15
You need to recommend a solution to meet the requirements for connections to ClaimsDB.
What should you recommend using for each requirement? To answer, select the appropriate options in the answer area.
NOTE: Each correct selection is worth one point.
正解:
解説:
質問 # 16
Your company plans to follow DevSecOps best practices of the Microsoft Cloud Adoption Framework for Azure.
You need to perform threat modeling by using a top-down approach based on the Microsoft Cloud Adoption Framework for Azure.
What should you use to start the threat modeling process?
- A. the DREAD model
- B. OWASP threat modeling
- C. the STRIDE model
正解:C
解説:
https://learn.microsoft.com/en-us/azure/security/develop/threat-modeling-tool-threats
質問 # 17
Hotspot Question
You have an Azure subscription that contains an Azure Kubernetes Service (AKS) cluster named AKS1. AKS1 hosts a Windows node pool named Pool1 and a Linux node pool named Pool2.
You are designing a pool update strategy for AKS1.
You need to recommend how often to replace the operating system images deployed to the nodes. The solution must meet the following requirements:
- Minimize how long it takes to apply operating system updates once the updates are released.
- Minimize administrative effort.
What should you recommend for each pool? To answer, select the appropriate options in the answer area.
NOTE: Each correct selection is worth one point.
正解:
解説:
Explanation:
Box 1: Monthly
Windows supports monthly node image version upgrades.
Box 2: Weekly
Linux supports weekly node image version upgrades.
Note: Azure Kubernetes Service patch and upgrade guidance
This section of the Azure Kubernetes Service (AKS) day-2 operations guide describes patching and upgrading strategies for AKS worker nodes and Kubernetes versions. As a cluster operator, you need to have a plan for keeping your clusters up to date and monitoring Kubernetes API changes and deprecations over time.
Reference:
https://learn.microsoft.com/en-us/azure/architecture/operator-guides/aks/aks-upgrade-practices
質問 # 18
You need to recommend a strategy for routing internet-bound traffic from the landing zones. The solution must meet the landing zone requirements.
What should you recommend as part of the landing zone deployment?
- A. a VNet-to-VNet connection
- B. forced tunneling
- C. service chaining
- D. local network gateways
正解:C
解説:
https://docs.microsoft.com/en-us/learn/modules/configure-vnet-peering/5-determine-service-chaining-uses
質問 # 19
You have a Microsoft Entra tenant named contoso.com and use Microsoft Intune. Each user in contoso.com has a Microsoft Entra ID P1 license and a Windows 11 device that has the Global Secure Access client deployed.
You plan to deploy the following configuration of Microsoft Entra Internet Access:
* Enable a baseline profile.
* Create a security profile named Profile` that has a priority of 300 and contains a single web content filtering policy named WCFPolicy configure WCFPolicy1 as follows:
o Set Action to allow.
o Include a single rule that has a fully qualified domain name (FQDN) destination of '. adatum.com.
* Link Profile1 to a Conditional Access policy named CAPolicy1, apply CAPolicy1 to all users, and grant access unless a user's device is noncompliant You need to evaluate the impact of the planned deployment on traffic to the following resources:
* https://www.adatum.com:8433
* https://www.fabrikam.com
Which two traffic scenarios will occur? Each correct answer presents a complete solution.
NOTE: Each correct selection is worth one point
- A. Traffic to https://www.adatum.com:8433 will be allowed from compliant devices only.
- B. Traffic to https://www.fabrikam.com will be blocked from noncompliant devices only.
- C. Traffic to https://www.fabrikam.com will be allowed from all the devices.
- D. Traffic to https://www.adatumxom:8433 will be allowed from all the devices.
- E. Traffic to https://www.fabrikam.com will be allowed from compliant devices only.
- F. Traffic to https://www.adatum.com:8433 will be blocked from all the devices.
正解:A、C
質問 # 20
Hotspot Question
You have a Microsoft 365 subscription that contains 1,000 users and two groups named Group1 and Group2. All the users have devices that are onboarded to Microsoft Intune and Microsoft Defender for Endpoint. Group1 manages Microsoft Entra and Microsoft 365 services. Group2 manages Intune and Defender for Endpoint.
You need to recommend a solution to prevent users from connecting to Microsoft 365 services from devices that have encryption disabled.
What should you recommend implementing for each group? To answer, select the options in the answer area.
NOTE: Each correct answer is worth one point.
正解:
解説:
Explanation:
Box 1: A Conditional Access policy
Group1 manages Microsoft Entra and Microsoft 365 services.
Microsoft Entra ID, Conditional Access, Common Conditional Access policy: Require a compliant device, Microsoft Entra hybrid joined device, or multifactor authentication for all users Organizations who deploy Microsoft Intune can use the information returned from their devices to identify devices that meet compliance requirements such as:
Requiring a PIN to unlock
*-> Requiring device encryption
Requiring a minimum or maximum operating system version
Requiring a device isn't jailbroken or rooted
Box 2: A compliance policy in Intune
Group2 manages Intune and Defender for Endpoint.
Device Compliance settings for Windows 10/11 in Intune includes:
* Encryption
Encryption of data storage on a device:
This setting applies to all drives on a device.
Not configured (default)
Require - Use Require to encrypt data storage on your devices.
DeviceStatus CSP - DeviceStatus/Compliance/EncryptionCompliance
Reference:
https://learn.microsoft.com/en-us/entra/identity/conditional-access/howto-conditional-access- policy-compliant-device
https://learn.microsoft.com/en-us/mem/intune/protect/compliance-policy-create-windows
質問 # 21
You need to recommend an identity security solution for the Azure AD tenant of Litware. The solution must meet the identity requirements and the regulatory compliance requirements.
What should you recommend? To answer, select the appropriate options in the answer area.
NOTE: Each correct selection is worth one point.
正解:
解説:
質問 # 22
You have a Microsoft 365 E5 subscription.
You are designing a solution to protect confidential data in Microsoft SharePoint Online sites that contain more than one million documents.
You need to recommend a solution to prevent Personally Identifiable Information (Pll) from being shared.
Which two components should you include in the recommendation? Each correct answer presents part of the solution.
NOTE: Each correct selection is worth one point.
- A. sensitivity label policies
- B. eDiscovery cases
- C. retention label policies
- D. data loss prevention (DLP) policies
正解:A、B
質問 # 23
Your company has a multi-cloud environment that contains a Microsoft 365 subscription, an Azure subscription, and Amazon Web Services (AWS) implementation. You need to recommend a security posture management solution for the following components:
* Azure loT Edge devices
* AWS EC2 instances
Which services should you include in the recommendation? To answer, select the appropriate options in the answer area. NOTE: Each correct selection is worth one point.
正解:
解説:
質問 # 24
You are designing an auditing solution for Azure landing zones that will contain the following components:
* SQL audit logs for Azure SQL databases
* Windows Security logs from Azure virtual machines
* Azure App Service audit logs from App Service web apps
You need to recommend a centralized logging solution for the landing zones. The solution must meet the following requirements:
* Log all privileged access.
* Retain logs for at least 365 days.
* Minimize costs.
What should you include in the recommendation? To answer, select the appropriate options in the answer are a. NOTE: Each correct selection is worth one point.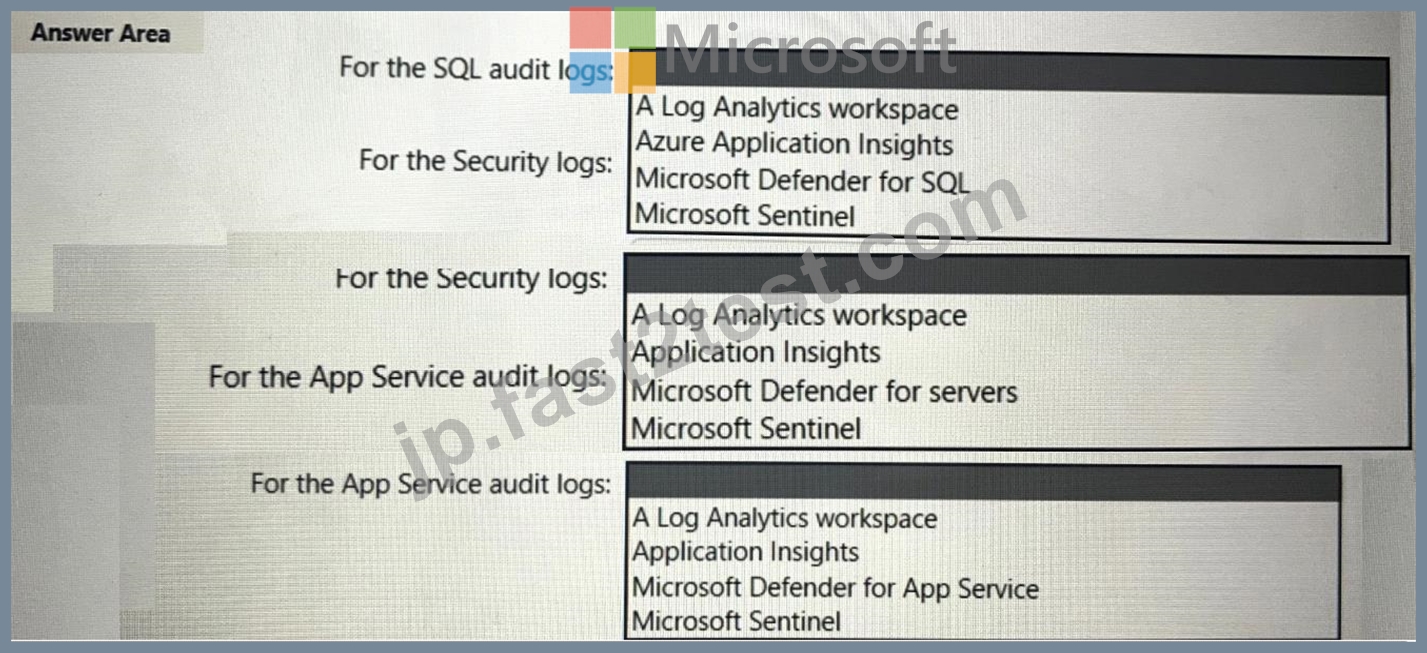
正解:
解説:
質問 # 25
You have a Microsoft 365 subscription that contains 1,000 Microsoft Exchange Online mailboxes.
Incoming email from the internet is scanned for security threats by using a third-party cloud service.
You are evaluating whether to replace the third-party service with Microsoft Defender for Office
365.
What should you modify to ensure that all the incoming email is scanned by Defender for Office
365 only?
- A. the Exchange Online transport rule
- B. the DNS records
- C. the Exchange Online connectors
- D. the accepted domains in Exchange Online
正解:C
解説:
Configure mail flow using connectors in Exchange Online
Connectors are a collection of instructions that customize the way your email flows to and from your Microsoft 365 or Office 365 organization.
What do connectors do?
Connectors are used in the following scenarios:
Enable mail flow between Microsoft 365 or Office 365 and email servers that you have in your on- premises environment (also known as on-premises email servers).
*-> Apply security restrictions or controls to email that's sent between your Microsoft 365 or Office
365 organization and a business partner or service provider.
Relay mail from devices, applications, or other non-mailbox entities in your on-premises environment through Microsoft 365 or Office 365.
Avoid graylisting that would otherwise occur due to the large volume of mail that's regularly sent between your Microsoft 365 or Office 365 organization and your on-premises environment or partners.
Reference:
https://learn.microsoft.com/en-us/exchange/mail-flow-best-practices/use-connectors-to-configure- mail-flow/use-connectors-to-configure-mail-flow
質問 # 26
You have an Azure subscription that contains the resources shown in the following table.
You need to recommend a network security solution for App1. The solution must meet the following requirements:
* Only the virtual machines that are connected to Subnet1 must be able to connect to D81.
* DB1 must be inaccessible from the internet
* Costs must be minimized.
What should you include in the recommendation? To answer, select the options in the answer area. NOTE:
Each correct answer is worth one point.
正解:
解説:
Explanation:
質問 # 27
You are designing a ransomware response plan that follows Microsoft Security Best Practices- You need to recommend a solution to limit the scope of damage of ransomware attacks without being locked out.
What should you include in the recommendations?
- A. Customer Lockbox for Microsoft Azure
- B. Privileged Access Workstations (PAWs)
- C. device compliance policies
- D. emergency access accounts
正解:D
質問 # 28
......
有効な問題最新版を試そうSC-100テスト解釈SC-100有効な試験ガイド:https://jp.fast2test.com/SC-100-premium-file.html
SC-100試験資料Microsoft学習ガイド:https://drive.google.com/open?id=1LIso0OLVqFWYBkLZLKGeMvxfQ9G_jgMX