

FCP_FSM_AN-7.2 PDF問題集リアル2026最近更新された問題
リリースFortinet FCP_FSM_AN-7.2更新された問題PDF
Fortinet FCP_FSM_AN-7.2 認定試験の出題範囲:
| トピック | 出題範囲 |
|---|---|
| トピック 1 |
|
| トピック 2 |
|
| トピック 3 |
|
| トピック 4 |
|
質問 # 12
Which analytics search can be used to apply a user and entity behavior analytics (UEBA) tag to an event for a failed login by the user JSmith?
- A. User = smith
- B. Username CONTAIN smit
- C. User IS jsmith
- D. Username NOT END WITH jsmith
正解:C
解説:
The correct syntax to match an exact username in FortiSIEM analytics search is User IS jsmith.
This ensures that the UEBA tag is applied only when the event is specifically tied to the user
"jsmith", which is required for accurate behavioral analytics.
質問 # 13
Refer to the exhibit.
Which section contains the subpattern configuration that determines how many matching events are needed to trigger the rule?
- A. Actions
- B. Filters
- C. Aggregate
- D. Group By
正解:C
解説:
The Aggregate section contains the condition COUNT(Matched Events) >= 1, which defines how many events must match the filter criteria for the rule to trigger. This is the subpattern configuration that determines the event threshold.
質問 # 14
Which statement about thresholds is true?
- A. FortiSIEM uses only device thresholds for security metrics.
- B. FortiSIEM uses fixed, hardcoded global and device thresholds for all performance metrics.
- C. FortiSIEM uses global and per device thresholds for performance metrics.
- D. FortiSIEM uses only global thresholds for performance metrics.
正解:C
解説:
FortiSIEM evaluates performance metrics against both global thresholds, which apply system-wide, and per-device thresholds, which can be customized for individual devices. This dual approach allows flexibility in monitoring while ensuring consistent baseline alerting.
質問 # 15
Refer to the exhibit.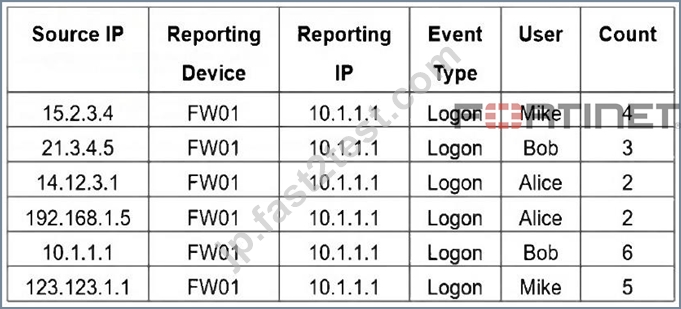
If you group the events by User and Count attributes, how many results will FortiSIEM display?
- A. One
- B. Two
- C. Six
- D. Five
- E. Three
正解:D
解説:
Grouping by User and Count yields five unique pairs: (Mike,4), (Bob,3), (Alice,2), (Bob,6), (Mike,5).
質問 # 16
In an automation policy, which two methods can you use to notify analysts when an incident is triggered? (Choose two.)
- A. Email
- B. FortiSIEM Case
- C. Pop-up window
- D. Syslog
正解:A、B
解説:
In FortiSIEM automation policies, analysts can be notified of triggered incidents through FortiSIEM Case (which creates and assigns a case for follow-up) and Email notifications (which send alerts directly to recipients). These methods ensure prompt awareness and response to security events.
質問 # 17
Which two settings must you configure to allow FortiSIEM to apply tags to devices in FortiClient EMS? (Choose two.)
- A. FortiEMS API credentials defined on FortiSIEM
- B. ZTNA tags defined on FortiSIEM
- C. Remediation script configured
- D. FortiSIEM API credentials defined on FortiEMS\
正解:A、D
解説:
To allow FortiSIEM to apply tags to devices in FortiClient EMS, FortiEMS API credentials must be defined on FortiSIEM to enable communication with EMS, and FortiSIEM API credentials must be defined on FortiEMS to allow EMS to accept tagging instructions from FortiSIEM. This bidirectional API trust is essential for tag application.
質問 # 18
Which analytics search can be used to apply a user and entity behavior analytics (UEBA) tag to an event for a failed login by the user JSmith?
- A. User = smith
- B. Username CONTAIN smit
- C. User IS jsmith
- D. Username NOT END WITH jsmith
正解:C
解説:
The correct syntax to match an exact username in FortiSIEM analytics search is User IS jsmith. This ensures that the UEBA tag is applied only when the event is specifically tied to the user "jsmith", which is required for accurate behavioral analytics.
質問 # 19
Refer to the exhibit.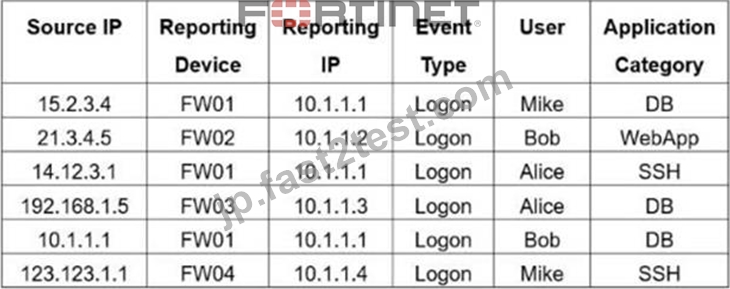
If you group the events by Reporting Device, Reporting IP, and Application Category, how many results will FortiSIEM display?
- A. One
- B. Four
- C. Two
- D. Six
- E. Five
正解:E
解説:
Grouping by Reporting Device, Reporting IP, and Application Category yields five unique tuples: (FW01, 10.1.1.1, DB), (FW02, 10.1.1.2, WebApp), (FW01, 10.1.1.1, SSH), (FW03, 10.1.1.3, DB), and (FW04, 10.1.1.4, SSH).
質問 # 20
Refer to the exhibit.
If a rule containing the automation policy shown in the exhibit triggers, what will happen?
- A. Associated source IP addresses will be blocked on two FortiGate firewalls.
- B. Associated source IP addresses will be blocked on devices in the Network CMDB group.
- C. Associated source IP addresses will be blocked on devices in the Aviation organization.
- D. Associated source IP addresses will be blocked on all FortiGate firewalls.
正解:A
解説:
The automation policy is configured to run a remediation script named "Fortinet FortiOS - Block Source IP FortiOS via API". It specifies enforcement on two FortiGate devices: FortiGate508 and FortiGate90D. Therefore, associated source IP addresses will be blocked on those two FortiGate firewalls only.
質問 # 21
Refer to the exhibit. What will FortiSIEM display if you apply the Group By and Display Fields configuration to a list of allowed firewall connections?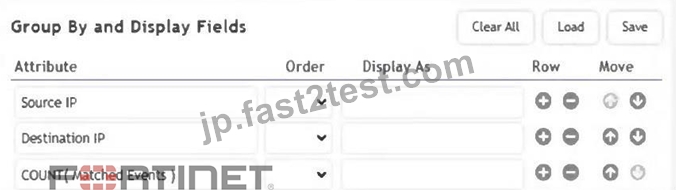
- A. A list of connections ordered by destination IP address hit count
- B. A list of connections between unique source and destination IP addresses
- C. A running count of connections, regardless of source or destination
- D. A list of connections ordered by the number of unique connections started by each source IP address
正解:B
解説:
With Source IP and Destination IP as grouping attributes, and COUNT(Matched Events) included, FortiSIEM will display a list of unique source-destination IP pairs along with the number of allowed connections between each pair. This configuration summarizes connection activity by unique communication paths.
質問 # 22
Refer to the exhibit.
An analyst wants the rule shown in the exhibit to trigger when three failed login attempts occur within three minutes.
What should the values be for the condition time window and aggregate count?
- A. Time window 180 seconds, aggregate count 2
- B. Time window 90 seconds, aggregate count 2
- C. Time window 90 seconds, aggregate count 3
- D. Time window 180 seconds, aggregate count 3
正解:D
解説:
To detect three failed login attempts within three minutes, you must set the aggregate count to 3 in the subpattern and the time window to 180 seconds in the rule condition. This ensures the rule triggers only if three or more failed logins occur in that timeframe.
質問 # 23
Refer to the exhibits.
Three events are collected over 10 minutes from two servers: Server A and Server B.
Based on the settings for the rule subpattern and a 10-minute condition window, how many incidents will the servers generate?
- A. Server A will generate one incident and Server B will not generate any incidents.
- B. Server A will generate one incident and Server B will generate one incident.
- C. Server A will not generate any incidents and server B will generate one incident.
- D. Server A will not generate any incidents and Server B will not generate any incidents.
正解:A
解説:
The rule triggers when the average CPU utilization (AVG(CPU Util)) exceeds the device's CMDB critical threshold and there are at least two matching events within the 10-minute window.
Server A: Average CPU = (90 + 95) / 2 = 92.5, which is greater than its critical threshold of 90, and it has two events, so one incident is generated.
Server B: Average CPU = (70 + 60) / 2 = 65, which is below its critical threshold of 70, so no incident is generated.
So, Server A generates one incident, and Server B generates none.
質問 # 24
From which two sources can you import data to train FortiSIEM machine learning? (Choose two.)
- A. FortiSIEM reports
- B. SQL database
- C. CSV files
- D. Syslog archives
正解:A、C
質問 # 25
Refer to the exhibit.
A FortiSIEM device is receiving syslog events from a FortiGate firewall. The FortiSIEM analyst is trying to search the raw event logs for the last two hours that contain the keyword "udp".
However, they are getting no results from the search, which they know should be available.
Based on the filter shown in the exhibit, why are there no search results?
- A. The analyst selected AND in the Next column. This is the wrong Boolean operator.
- B. The Time Range value should be set to Real-Time.
- C. The analyst selected = in the Operator column. That is the wrong operator.
- D. The keyword is case sensitive. Instead of typing udp in the Value field, the analyst should type UDP.
正解:C
解説:
The operator is set to "=", which performs an exact match on the entire raw event log, not a substring search. To find logs that contain the keyword "udp", the analyst should use the CONTAIN operator instead. This will return all logs where "udp" appears anywhere in the raw log message.
質問 # 26
Which information can FortiSIEM retrieve from FortiClient EMS through an API connection?
- A. FortiSIEM license
- B. Host login credentials
- C. ZTNA tags
- D. Host software versions
正解:C
解説:
FortiSIEM can retrieve ZTNA tags from FortiClient EMS through an API connection, enabling dynamic user and device classification for policy enforcement and incident response.
質問 # 27
Refer to the exhibit.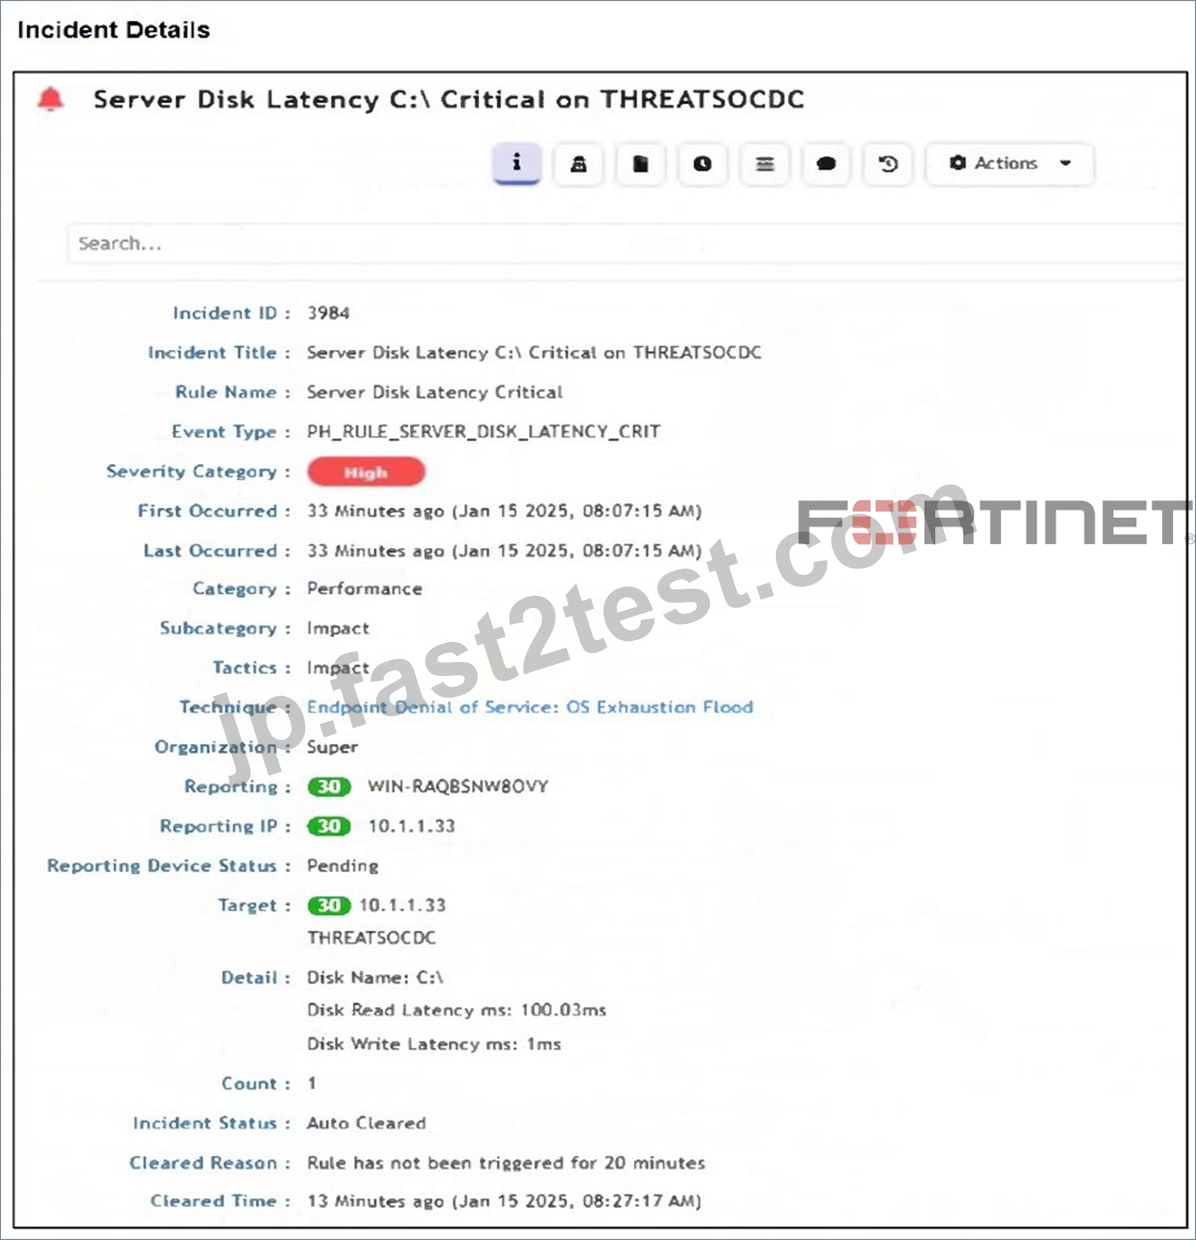
How was this incident cleared?
- A. FortiSIEM cleared the incident automatically after 24 hours.
- B. The endpoint was rebooted and sent an all-clear signal to FortiSIEM.
- C. The incident was cleared automatically by the rule.
- D. The analyst manually cleared the incident from the incident table.
正解:C
解説:
The Incident Status shows "Auto Cleared", and the Cleared Reason states: "Rule has not been triggered for 20 minutes." This indicates that the incident was automatically cleared by the rule logic after a defined period of inactivity.
質問 # 28
Refer to the exhibit. What is the Group: VPN Gateway value referring to?
- A. A CMDB device group
- B. A FortiGate address group
- C. A watchlist
- D. An authentication user group
正解:A
解説:
The value Group: VPN Gateway refers to a CMDB device group in FortiSIEM. This group represents a collection of devices categorized as VPN Gateways in the Configuration Management Database. By filtering with this group, the query retrieves events where the Source IP matches any device included in the CMDB group "VPN Gateway."
質問 # 29
Refer to the exhibit.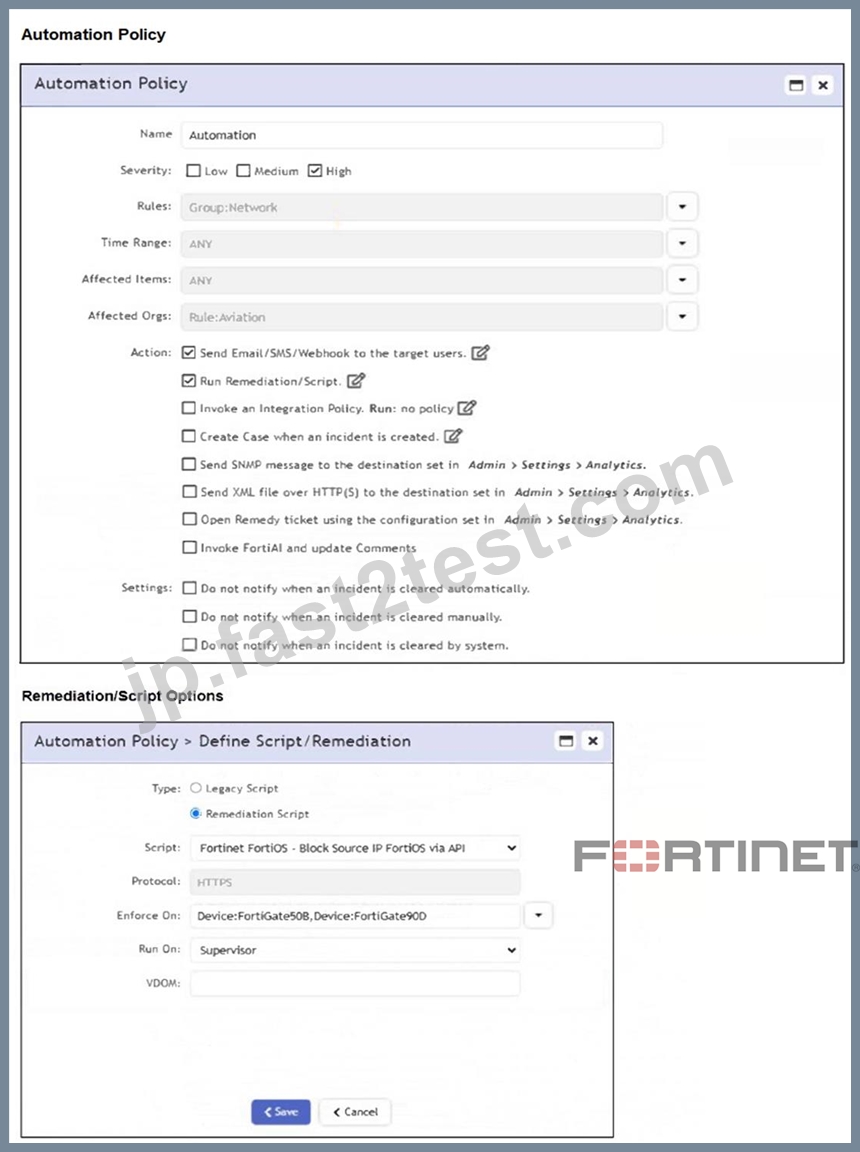
If a rule containing the automation policy shown in the exhibit triggers, what will happen?
- A. Associated source IP addresses will be blocked on two FortiGate firewalls.
- B. Associated source IP addresses will be blocked on devices in the Network CMDB group.
- C. Associated source IP addresses will be blocked on devices in the Aviation organization.
- D. Associated source IP addresses will be blocked on all FortiGate firewalls.
正解:A
解説:
The automation policy is configured to run a remediation script named "Fortinet FortiOS - Block Source IP FortiOS via API". It specifies enforcement on two FortiGate devices: FortiGate508 and FortiGate90D. Therefore, associated source IP addresses will be blocked on those two FortiGate firewalls only.
質問 # 30
......
FCP_FSM_AN-7.2問題集と練習テスト(63試験問題):https://jp.fast2test.com/FCP_FSM_AN-7.2-premium-file.html
ガイド(2026年最新)実際のFortinet FCP_FSM_AN-7.2試験問題:https://drive.google.com/open?id=19lB2kMog7lGMTFHxZ3GDiO4cBeGtkHgN