

最新のAssociate-Cloud-Engineer実際の無料試験問題更新された269問あります
無料で使えるAssociate-Cloud-Engineer試験ブレーン問題集認定ガイドの問題と解答
質問 # 87
Your company publishes large files on an Apache web server that runs on a Compute Engine instance. The Apache web server is not the only application running in the project. You want to receive an email when the egress network costs for the server exceed 100 dollars for the current month as measured by Google Cloud Platform (GCP). What should you do?
- A. Export the billing data to BigQuery. Create a Cloud Function that uses BigQuery to sum the egress network costs of the exported billing data for the Apache web server for the current month and sends an email if it is over 100 dollars. Schedule the Cloud Function using Cloud Scheduler to run hourly.
- B. Set up a budget alert on the project with an amount of 100 dollars, a threshold of 100%, and notification type of "email."
- C. Set up a budget alert on the billing account with an amount of 100 dollars, a threshold of 100%, and notification type of "email."
- D. Use the Stackdriver Logging Agent to export the Apache web server logs to Stackdriver Logging.Create a Cloud Function that uses BigQuery to parse the HTTP response log data in Stackdriver for the current month and sends an email if the size of all HTTP responses, multiplied by current GCP egress prices, totals over 100 dollars. Schedule the Cloud Function using Cloud Scheduler to run hourly.
正解:A
解説:
Explanation
https://blog.doit-intl.com/the-truth-behind-google-cloud-egress-traffic-6e8f57b5c2f8
質問 # 88
An application generates daily reports in a Compute Engine virtual machine (VM). The VM is in the project corp-iot-insights. Your team operates only in the project corp-aggregate-reports and needs a copy of the daily exports in the bucket corp-aggregate-reports-storage. You want to configure access so that the daily reports from the VM are available in the bucket corp-aggregate-reports-storage and use as few steps as possible while following Google-recommended practices. What should you do?
- A. Make corp-aggregate-reports-storage public and create a folder with a pseudo-randomized suffix name.
Share the folder with the IoT team. - B. Create a Shared VPC network between both projects. Grant the VM Service Account the role Storage Object Creator on corp-iot-insights.
- C. Move both projects under the same folder.
- D. Grant the VM Service Account the role Storage Object Creator on corp-aggregate-reports-storage.
正解:C
質問 # 89
You recently discovered that your developers are using many service account keys during their development process. While you work on a long term improvement, you need to quickly implement a process to enforce short-lived service account credentials in your company. You have the following requirements:
* All service accounts that require a key should be created in a centralized project called pj-sa.
* Service account keys should only be valid for one day.
You need a Google-recommended solution that minimizes cost. What should you do?
- A. Enforce an org policy constraint allowing the lifetime of service account keys to be 24 hours. Enforce an org policy constraint denying service account key creation with an exception on pj-sa.
- B. Implement a Kubernetes Cronjob to rotate all service account keys periodically. Disable attachment of service accounts to resources in all projects with an exception to pj-sa.
- C. Implement a Cloud Run job to rotate all service account keys periodically in pj-sa. Enforce an org policy to deny service account key creation with an exception to pj-sa.
- D. Enforce a DENY org policy constraint over the lifetime of service account keys for 24 hours. Disable attachment of service accounts to resources in all projects with an exception to pj-sa.
正解:A
解説:
According to the Google Cloud documentation, you can use organization policy constraints to control the creation and expiration of service account keys. The constraints are:
constraints/iam.allowServiceAccountKeyCreation: This constraint allows you to specify which projects or folders can create service account keys. You can set the value to true or false, or use a condition to apply the constraint to specific service accounts. By setting this constraint to false for the organization and adding an exception for the pj-sa project, you can prevent developers from creating service account keys in other projects.
constraints/iam.serviceAccountKeyMaxLifetime: This constraint allows you to specify the maximum lifetime of service account keys. You can set the value to a duration in seconds, such as 86400 for one day. By setting this constraint to 86400 for the organization, you can ensure that all service account keys expire after one day.
These constraints are recommended by Google Cloud as best practices to minimize the risk of service account key misuse or compromise. They also help you reduce the cost of managing service account keys, as you do not need to implement a custom solution to rotate or delete them.
Reference:
1: Associate Cloud Engineer Certification Exam Guide | Learn - Google Cloud
5: Create and delete service account keys - Google Cloud
Organization policy constraints for service accounts
質問 # 90
You deployed an LDAP server on Compute Engine that is reachable via TLS through port 636 using UDP.
You want to make sure it is reachable by clients over that port. What should you do?
- A. Add a network tag of your choice to the instance. Create a firewall rule to allow ingress on UDP port
636 for that network tag. - B. Create a route called allow-udp-636 and set the next hop to be the VM instance running the LDAP server.
- C. Add a network tag of your choice to the instance running the LDAP server. Create a firewall rule to allow egress on UDP port 636 for that network tag.
- D. Add the network tag allow-udp-636 to the VM instance running the LDAP server.
正解:A
解説:
Explanation
A tag is simply a character string added to a tags field in a resource, such as Compute Engine virtual machine (VM) instances or instance templates. A tag is not a separate resource, so you cannot create it separately. All resources with that string are considered to have that tag. Tags enable you to make firewall rules and routes applicable to specific VM instances.
質問 # 91
Your company uses Cloud Storage to store application backup files for disaster recovery purposes. You want to follow Google's recommended practices. Which storage option should you use?
- A. Regional Storage
- B. Multi-Regional Storage
- C. Coldline Storage
- D. Nearline Storage
正解:C
解説:
Reference:
https://cloud.google.com/storage/docs/storage-classes#nearline
質問 # 92
You are using Container Registry to centrally store your company's container images in a separate project. In another project, you want to create a Google Kubernetes Engine (GKE) cluster. You want to ensure that Kubernetes can download images from Container Registry. What should you do?
- A. Configure the ACLs on each image in Cloud Storage to give read-only access to the default Compute Engine service account.
- B. When you create the GKE cluster, choose the Allow full access to all Cloud APIs option under
`Access scopes'. - C. In the project where the images are stored, grant the Storage Object Viewer IAM role to the service account used by the Kubernetes nodes.
- D. Create a service account, and give it access to Cloud Storage. Create a P12 key for this service account and use it as an imagePullSecrets in Kubernetes.
正解:C
解説:
If the cluster is in a different project or if the VMs in the cluster use a different service account, you must grant the service account the appropriate permissions to access the storage bucket used by Container Registry.
For the service account used by Compute Engine VMs, including VMs in Google Kubernetes Engine clusters, access is based on both Cloud IAM permissions and storage access scopes.
https://cloud.google.com/container-registry/docs/access-control
https://cloud.google.com/container-registry/docs/using-with-google-cloud-platform
質問 # 93
You create a Deployment with 2 replicas in a Google Kubernetes Engine cluster that has a single preemptible node pool. After a few minutes, you use kubectl to examine the status of your Pod and observe that one of them is still in Pending status: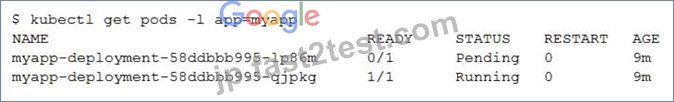
What is the most likely cause?
- A. The pending Pod was originally scheduled on a node that has been preempted between the creation of the Deployment and your verification of the Pods' status. It is currently being rescheduled on a new node.
- B. Too many Pods are already running in the cluster, and there are not enough resources left to schedule the pending Pod.
- C. The pending Pod's resource requests are too large to fit on a single node of the cluster.
- D. The node pool is configured with a service account that does not have permission to pull the container image used by the pending Pod.
正解:B
質問 # 94
Your organization needs to grant users access to query datasets in BigQuery but prevent them from accidentally deleting the datasets. You want a solution that follows Google-recommended practices. What should you do?
- A. Add users to roles/bigquery user role only, instead of roles/bigquery dataOwner.
- B. Add users to roles/bigquery dataEditor role only, instead of roles/bigquery dataOwner.
- C. Create a custom role by removing delete permissions, and add users to that role only.
- D. Create a custom role by removing delete permissions. Add users to the group, and then add the group to the custom role.
正解:D
解説:
https://cloud.google.com/bigquery/docs/access-control#custom_roles
Custom roles enable you to enforce the principle of least privilege, ensuring that the user and service accounts in your organization have only the permissions essential to performing their intended functions.
質問 # 95
You have a Compute Engine instance hosting an application used between 9 AM and 6 PM on weekdays. You want to back up this instance daily for disaster recovery purposes. You want to keep the backups for 30 days. You want the Google-recommended solution with the least management overhead and the least number of services. What should you do?
- A. 1. In the Cloud Console, go to the Compute Engine Disks page and select your instance's disk.
2. In the Snapshot Schedule section, select Create Schedule and configure the following parameters:
- Schedule frequency: Daily
- Start time: 1:00 AM ?2:00 AM
- Autodelete snapshots after 30 days - B. 1. Create a bash script in the instance that copies the content of the disk to Cloud Storage.
2. Create a bash script in the instance that deletes data older than 30 days in the backup Cloud Storage bucket.
3. Configure the instance's crontab to execute these scripts daily at 1:00 AM. - C. 1. Update your instances' metadata to add the following value: snapshot-schedule: 0 1 * * *
2. Update your instances' metadata to add the following value: snapshot-retention: 30 - D. 1. Create a Cloud Function that creates a snapshot of your instance's disk.
2. Create a Cloud Function that deletes snapshots that are older than 30 days.
3. Use Cloud Scheduler to trigger both Cloud Functions daily at 1:00 AM.
正解:A
質問 # 96
You are building a multi-player gaming application that will store game information in a database. As the popularity of the application increases, you are concerned about delivering consistent performance. You need to ensure an optimal gaming performance for global users, without increasing the management complexity.
What should you do?
- A. Store game statistics in a Bigtable database partitioned by username.
- B. Use Cloud Spanner to store user data mapped to the game statistics.
- C. Use BigQuery to store game statistics with a Redis on Memorystore instance in the front to provide global consistency.
- D. Use Cloud SQL database with cross-region replication to store game statistics in the EU, US, and APAC regions.
正解:B
質問 # 97
Your team has been working on building a web application. The plan is to deploy to Kubernetes. You currently have a Dockerfile that works locally. How can you get the application deployed to Kubernetes?
- A. Use kubectl to push the convert the Dockerfile into a deployment.
- B. Use docker to create a container image, save the image to Cloud Storage, deploy the uploaded image to Kubernetes with kubectl.
- C. Use docker to create a container image, push it to the Google Container Registry, deploy the uploaded image to Kubernetes with kubectl.
- D. Use kubectl apply to push the Dockerfile to Kubernetes.
正解:C
質問 # 98
You are using Data Studio to visualize a table from your data warehouse that is built on top of BigQuery. Data is appended to the data warehouse during the day. At night, the daily summary is recalculated by overwriting the table. You just noticed that the charts in Data Studio are broken, and you want to analyze the problem.
What should you do?
- A. In Cloud Logging create a filter for your Data Studio report
- B. Use Cloud Debugger to find out why the data was not refreshed correctly
- C. Use the BigQuery interface to review the nightly Job and look for any errors
- D. Review the Error Reporting page in the Cloud Console to find any errors.
正解:C
解説:
Explanation
Cloud Debugger helps inspect the state of an application, at any code location, without stopping or slowing down the running app // https://cloud.google.com/debugger/docs
質問 # 99
You need to create a custom IAM role for use with a GCP service. All permissions in the role must be suitable for production use. You also want to clearly share with your organization the status of the custom role. This will be the first version of the custom role. What should you do?
- A. Use permissions in your role that use the 'supported' support level for role permissions. Set the role stage to ALPHA while testing the role permissions.
- B. Use permissions in your role that use the 'testing' support level for role permissions. Set the role stage to BETA while testing the role permissions.
- C. Use permissions in your role that use the 'testing' support level for role permissions. Set the role stage to ALPHA while testing the role permissions.
- D. Use permissions in your role that use the 'supported' support level for role permissions. Set the role stage to BETA while testing the role permissions.
正解:C
解説:
Explanation
質問 # 100
Your company uses Cloud Storage to store application backup files for disaster recovery purposes. You want to follow Google's recommended practices.
Which storage option should you use?
- A. Regional Storage
- B. Multi-Regional Storage
- C. Coldline Storage
- D. Nearline Storage
正解:C
解説:
Coldline is a new Cloud Storage class designed for long-term archival and disaster recovery.
https://cloud.google.com/blog/products/gcp/introducing-coldline-and-a-unified-platform-for-data- storage
質問 # 101
You have deployed multiple Linux instances on Compute Engine. You plan on adding more instances in the coming weeks. You want to be able to access all of these instances through your SSH client over me Internet without having to configure specific access on the existing and new instances. You do not want the Compute Engine instances to have a public IP. What should you do?
- A. Configure Cloud Identity-Aware Proxy for SSH and TCP resources.
- B. Configure Cloud Identity-Aware Proxy (or HTTPS resources
- C. Create an SSH keypair and store the public key as a project-wide SSH Key
- D. Create an SSH keypair and store the private key as a project-wide SSH Key
正解:A
解説:
https://cloud.google.com/iap/docs/using-tcp-forwarding
質問 # 102
You significantly changed a complex Deployment Manager template and want to confirm that the dependencies of all defined resources are properly met before committing it to the project. You want the most rapid feedback on your changes. What should you do?
- A. Execute the Deployment Manager template against a separate project with the same configuration, and monitor for failures.
- B. Use granular logging statements within a Deployment Manager template authored in Python.
- C. Monitor activity of the Deployment Manager execution on the Stackdriver Logging page of the GCP Console.
- D. Execute the Deployment Manager template using the --previewoption in the same project, and observe the state of interdependent resources.
正解:D
解説:
Explanation/Reference: https://cloud.google.com/deployment-manager/docs/deployments/updating-deployments
質問 # 103
......
Associate-Cloud-Engineer認定概要最新のAssociate-Cloud-EngineerのPDF問題集:https://jp.fast2test.com/Associate-Cloud-Engineer-premium-file.html
トップクラスGoogle Associate-Cloud-Engineer試験材料で学習ガイド!練習問題バージョン:https://drive.google.com/open?id=1RTB0i5g9G2rBvqb5tW8qGoO3aGfGGA46