

合格させるCKA試験問題で実際テストエンジンPDFには85問題あります
最新をゲットせよ!CKA認定練習テスト問題の試験問題集
Linux Foundation Certified Kubernetes Administrator(CKA)プログラムは、Kubernetes管理における専門知識を証明したいITプロフェッショナル向けの業界をリードする認定資格です。Kubernetesは、コンテナ化されたアプリケーションのデプロイメント、スケーリング、管理を自動化するオープンソースのコンテナオーケストレーションプラットフォームです。CKAプログラムは、Kubernetes管理における個人のスキルを評価し、業界に認められた認定資格を提供するために設計されています。
質問 # 40
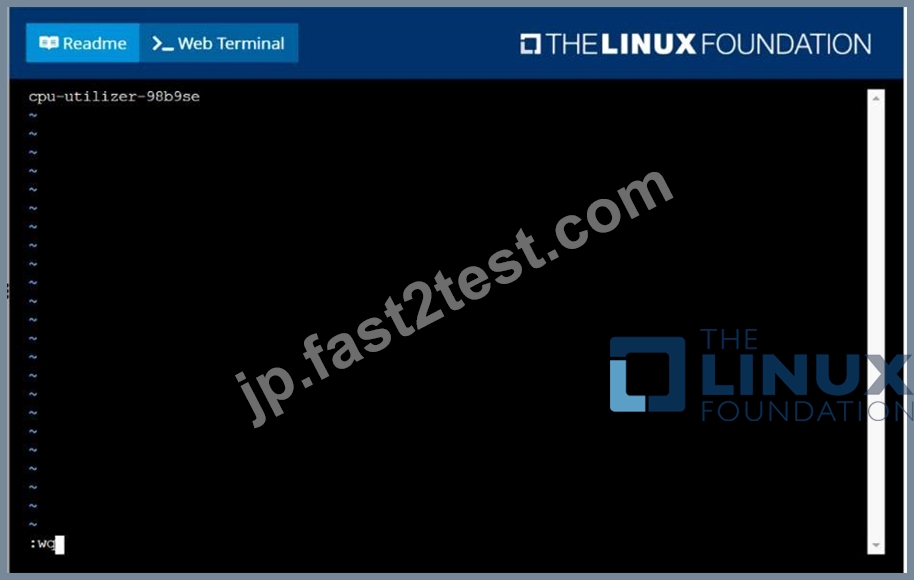
From the pod label name=cpu-utilizer, find pods running high CPU workloads and write the name of the pod consuming most CPU to the file /opt/KUTR00102/KUTR00102.txt (which already exists).
正解:
解説:
solution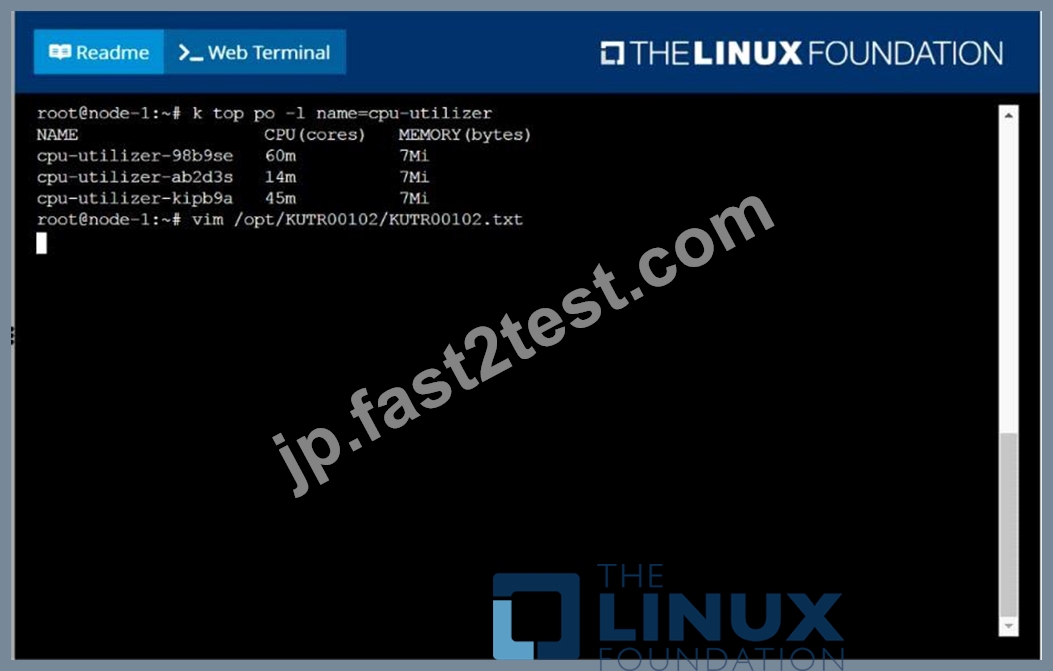
質問 # 41
Set the node named ek8s-node-1 as unavailable and reschedule all the pods running on it.
正解:
解説: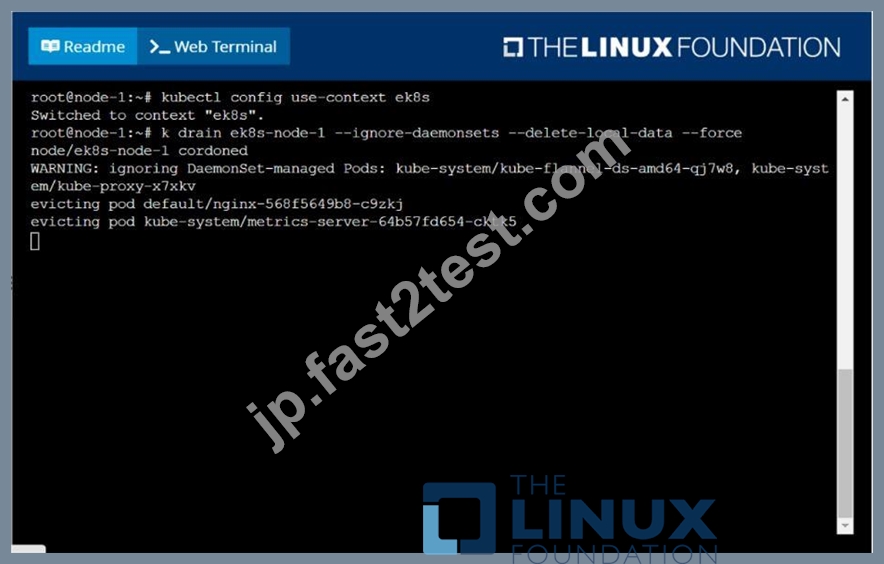
質問 # 42
Schedule a Pod as follows:
. Name: kucc1
. App Containers : 2
. Container Name/Images :
* redis
* Memcached
正解:
解説:
A screen shot of a computer AI-generated content may be incorrect.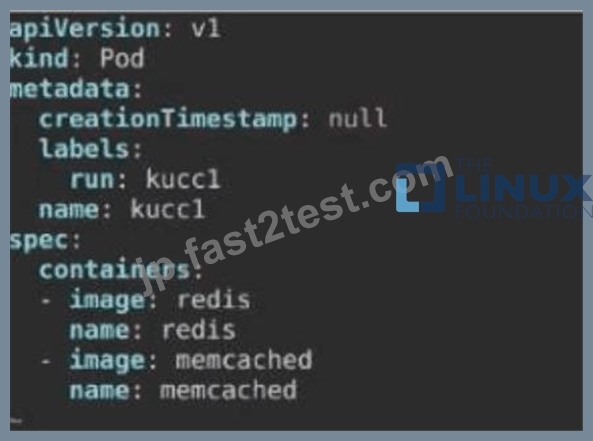
質問 # 43
Create a job named "hello-job" with the image busybox which echos "Hello I'm running job"
- A. kubectl create job hello-job --image=busybox --dry-run -o yaml
-- echo "Hello I'm running job" > hello-job.yaml
kubectl create -f hello-job.yaml
//Verify Job
kubectl get po
kubectl logs hello-job-* - B. kubectl create job hello-job --image=busybox --dry-run -o yaml
-- echo "Hello I'm running job" > hello-job.yaml
kubectl create -f hello-job.yaml
//Verify Job
kubectl get job
kubectl get po
kubectl logs hello-job-*
正解:B
質問 # 44
Set the node namedek8s-node-1asunavailable and reschedule all thepods running on it.
正解:
解説:
See the solution below.
Explanation
solution
質問 # 45
Check the Image version of nginx-dev pod using jsonpath
正解:
解説:
See the solution below.
Explanation
kubect1 get po nginx-dev -o
jsonpath='{.spec.containers[].image}{"\n"}'
質問 # 46 
Task
Create a new Ingress resource as follows:
. Name: echo
. Namespace : sound-repeater
. Exposing Service echoserver-service on
http://example.org/echo
using Service port 8080
The availability of Service
echoserver-service can be checked
i
using the following command, which should return 200 :
[candidate@cka000024] $ curl -o /de v/null -s -w "%{http_code}\n"
http://example.org/echo
正解:
解説:
Task Summary
Create an Ingress named echo in the sound-repeater namespace that:
* Routes requests to /echo on host example.org
* Forwards traffic to service echoserver-service
* Uses service port 8080
* Verification should return HTTP 200 using curl
# Step-by-Step Answer
1## SSH into the correct node
As shown in the image:
bash
CopyEdit
ssh cka000024
## Skipping this will result in a ZERO score!
2## Verify the namespace and service
Ensure the sound-repeater namespace and echoserver-service exist:
kubectl get svc -n sound-repeater
Look for:
echoserver-service ClusterIP ... 8080/TCP
3## Create the Ingress manifest
Create a YAML file: echo-ingress.yaml
apiVersion: networking.k8s.io/v1
kind: Ingress
metadata:
name: echo
namespace: sound-repeater
annotations:
nginx.ingress.kubernetes.io/rewrite-target: /$1
spec:
rules:
- host: example.org
http:
paths:
- path: /echo
pathType: Prefix
backend:
service:
name: echoserver-service
port:
number: 8080
4## Apply the Ingress resource
kubectl apply -f echo-ingress.yaml
5## Test with curl as instructed
Use the exact verification command:
curl -o /dev/null -s -w "%{http_code}\n"
http://example.org/echo
# You should see:
200
# Final Answer Summary
ssh cka000024
kubectl get svc -n sound-repeater
# Create the Ingress YAML
cat <<EOF > echo-ingress.yaml
apiVersion: networking.k8s.io/v1
kind: Ingress
metadata:
name: echo
namespace: sound-repeater
annotations:
nginx.ingress.kubernetes.io/rewrite-target: /$1
spec:
rules:
- host: example.org
http:
paths:
- path: /echo
pathType: Prefix
backend:
service:
name: echoserver-service
port:
number: 8080
EOF
kubectl apply -f echo-ingress.yaml
curl -o /dev/null -s -w "%{http_code}\n"
http://example.org/echo
質問 # 47
Create an nginx pod and load environment values from the above configmap "keyvalcfgmap" and exec into the pod and verify the environment variables and delete the pod
- A. // first run this command to save the pod yaml
kubectl run nginx --image=nginx --restart=Always --dry-run -o
yaml > nginx-pod.yml
// edit the yml to below file and create
vim nginx-pod.yml
apiVersion: v1
name: nginx
envFrom:
- configMapRef:
name: keyvalcfgmap
restartPolicy: Always
kubectl apply -f nginx-pod.yml
// verify
kubectl exec -it nginx -- env
kubectl delete po nginx - B. // first run this command to save the pod yaml
kubectl run nginx --image=nginx --restart=Always --dry-run -o
yaml > nginx-pod.yml
// edit the yml to below file and create
vim nginx-pod.yml
apiVersion: v1
kind: Pod
metadata:
labels:
run: nginx
name: nginx
spec:
containers:
- image: nginx
name: nginx
envFrom:
- configMapRef:
name: keyvalcfgmap
restartPolicy: Always
kubectl apply -f nginx-pod.yml
// verify
kubectl exec -it nginx -- env
kubectl delete po nginx
正解:B
質問 # 48
You have a Kubernetes cluster with multiple namespaces. You want to create a ClusterRole that grants users in the "admins" group the ability to create, delete, and list Pods in any namespace, but restricts them from managing namespaces themselves.
正解:
解説:
See the solution below with Step by Step Explanation.
Explanation:
Solution (Step by Step) :
1. Create the ClusterRole: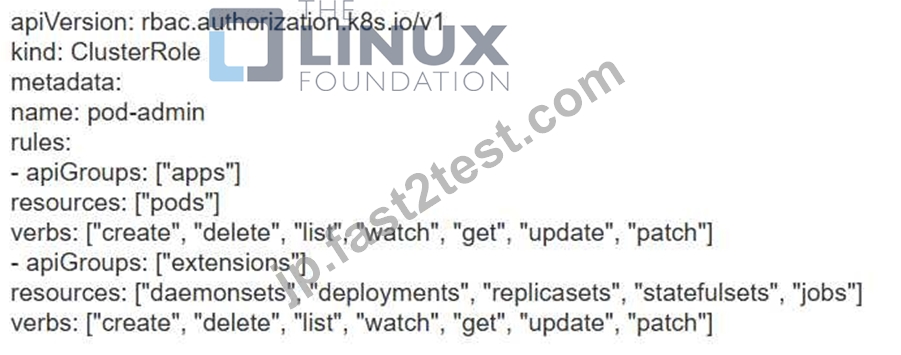
2. Create the ClusterRoleBinding: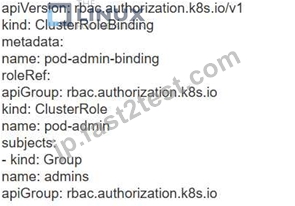
3. Apply the ClusterRole and ClusterRoleBinding: bash kubectl apply -f clusterrole.yaml kubectl apply -f clusterrolebinding.yaml
質問 # 49
You have a Kubernetes cluster with two worker nodes and a single Nginx service deployed. You want to expose this service externally using a LoadBalancer service type but only want traffic to be directed to pods on a specific worker node. How would you achieve this?
正解:
解説:
See the solution below with Step by Step Explanation.
Explanation:
Solution (Step by Step) :
1. Create a Node Selector:
- Create a Node Selector label on the worker node where you want to host the Nginx pods.
- Example: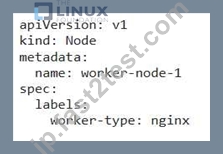
- Apply this configuration using 'kubectl apply -f node-config.yaml'. 2. Configure the Deployment: - Update the Nginx deployment to include the Node Selector label in its pod template. - Example: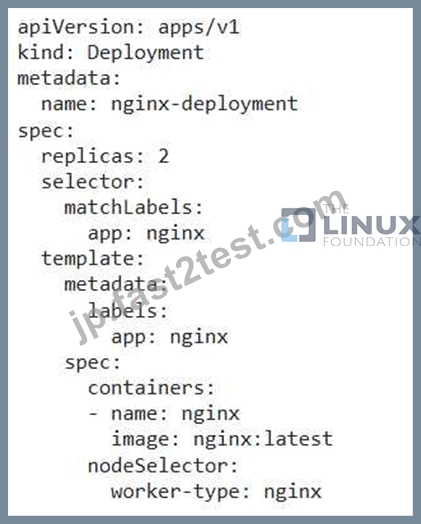
- Apply the updated deployment configuration using 'kubectl apply -f nginx-deployment.yamr. 3. Create a LoadBalancer Service: - Create a LoadBalancer type service that selects the Nginx pods with the 'app=nginx' label. - Example:
- Apply the service configuration using 'kubectl apply -f nginx-service.yamP. 4. Verify the Deployment: - Confirm the deployment of the Nginx pods on the specified worker node using 'kubectl get pods -l app=nginx -o wide'. - Check the LoadBalancer service's external IP address using 'kubectl get services nginx-service'. - Access the Nginx service using the external IP address. All traffic should be routed to the pods on the worker node with the 'worker-type: nginx' label. ---
質問 # 50
You need to configure CoreDNS to resolve DNS queries for services in different namespaces within your Kubernetes cluster. You want to ensure that pods in one namespace cannot resolve the names of services in other namespaces unless explicitly allowed.
正解:
解説:
See the solution below with Step by Step Explanation.
Explanation:
Solution (Step by Step) :
1 . Configure CoreDNS with Namespace-Specific DNS:
- In the CoreDNS ConfigMap, configure the 'kubernetes' plugin to restrict DNS resolution based on namespaces.
2. Use Network Policies for Cross-Namespace Communication: - If you need pods in one namespace to communicate with services in another namespace, use network policies to explicitly allow the communication.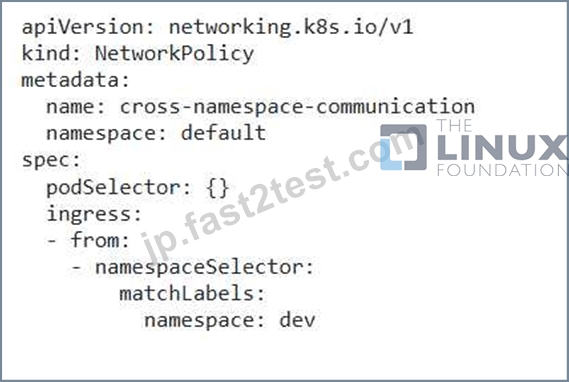
3. Test Namespace-Specific DNS: - Deploy pods in different namespaces and try to resolve service names from those pods. You should only be able to resolve names of services in the same namespace or namespaces that have been explicitly allowed using network policies.
質問 # 51
View certificate details in /etc/kubernetes/pki
正解:
解説:
// Verify Public Key / Certificate file Openssl x509 -in certificate.crt -noout -text // Verify Private Key Openssl rsa -in "private-key" -check // Verify CSR Openssl req -text -noout -verify
質問 # 52
Get IP address of the pod - "nginx-dev"
- A. Kubect1 get po -o wide
Using JsonPath
kubect1 get pods -o=jsonpath='{range
.items[*]}{.metadata.name}{"\t"}{.status.podIP}{"\n"}{end}' - B. Kubect1 get po -o wide
Using JsonPath
kubect1 get pods
.items[*]}{.metadata.name}{"\t"}{.status.podIP}{"\n"}{end}'
正解:A
質問 # 53
Get the list of pods of webapp deployment
- A. // Get the label of the deployment
kubectl get deploy --show-labels
// Get the pods with that label
kubectl get pods -l app=webapp - B. // Get the label of the deployment
kubectl get deploy --show-labels
kubectl get pods -l app=webapp
正解:A
質問 # 54
An Administrator is configuring Authentication Enforcement and they would like to create an exemption rule to exempt a specific group from authentication. Which authentication enforcement object should they select?
- A. default-browser-challenge
- B. default-no-captive-port
- C. default-web-form
- D. default-authentication-bypass
正解:B
質問 # 55
Create a pod as follows:
Name: mongo
Using Image: mongo
In a new Kubernetes namespace named: my-website
正解:
解説:
solution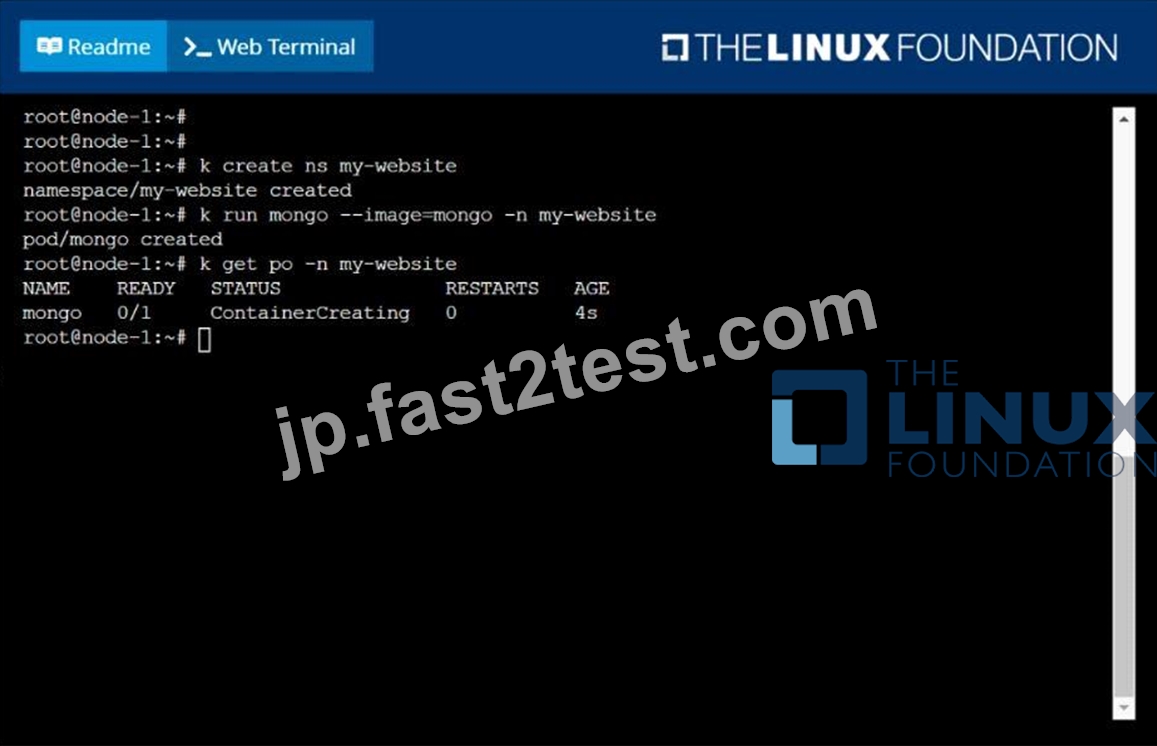
質問 # 56
Score: 7%
Task
Reconfigure the existing deployment front-end and add a port specification named http exposing port 80/tcp of the existing container nginx.
Create a new service named front-end-svc exposing the container port http.
Configure the new service to also expose the individual Pods via a NodePort on the nodes on which they are scheduled.
正解:
解説:
Solution:
kubectl get deploy front-end
kubectl edit deploy front-end -o yaml
#port specification named http
#service.yaml
apiVersion: v1
kind: Service
metadata:
name: front-end-svc
labels:
app: nginx
spec:
ports:
- port: 80
protocol: tcp
name: http
selector:
app: nginx
type: NodePort
# kubectl create -f service.yaml
# kubectl get svc
# port specification named http
kubectl expose deployment front-end --name=front-end-svc --port=80 --tarport=80 --type=NodePort
質問 # 57
Create a pod as follows:
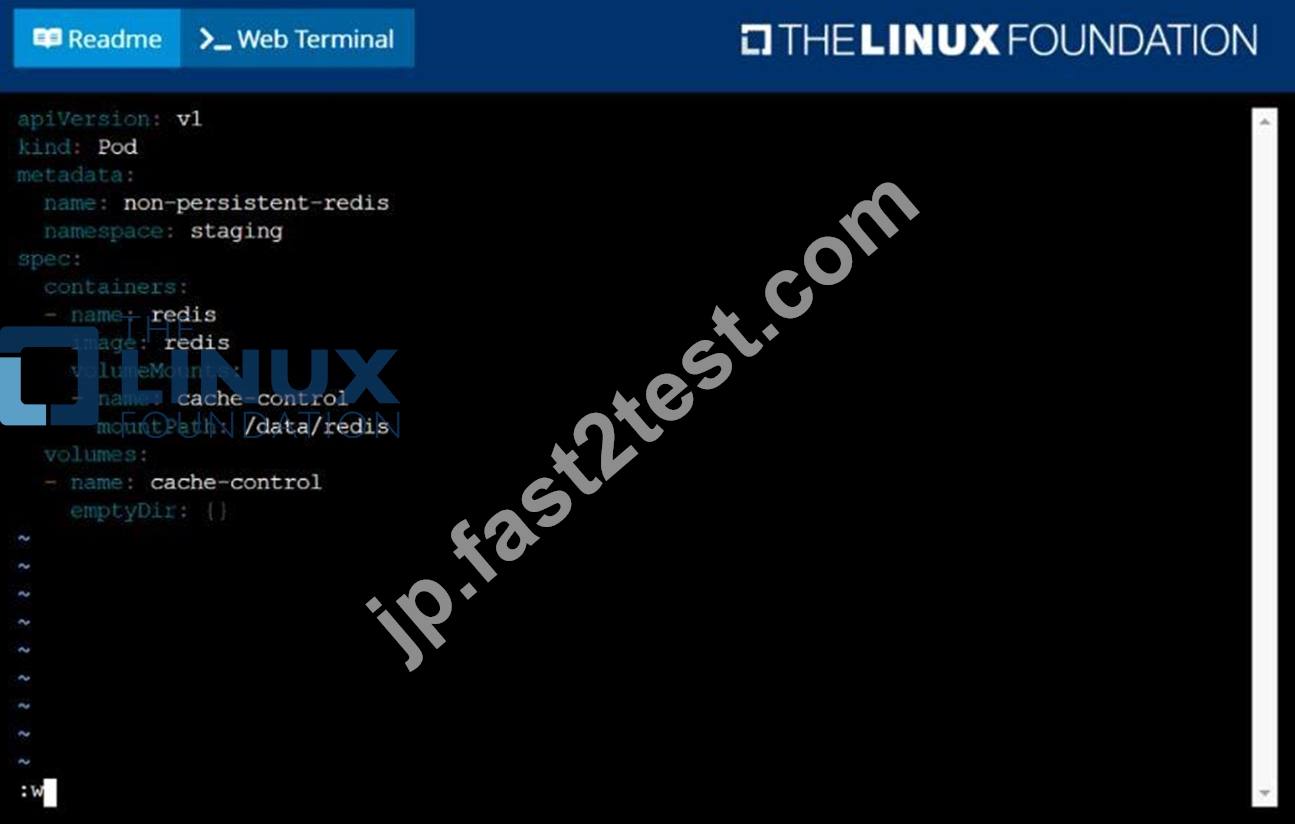
Name: non-persistent-redis
container Image: redis
Volume with name: cache-control
Mount path: /data/redis
The pod should launch in the staging namespace and the volume must not be persistent.
正解:
解説:
solution
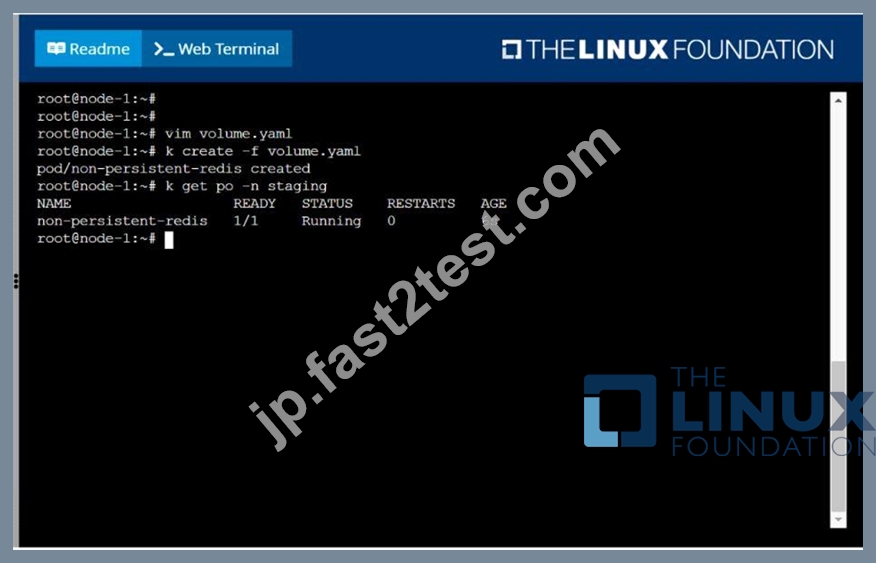
質問 # 58
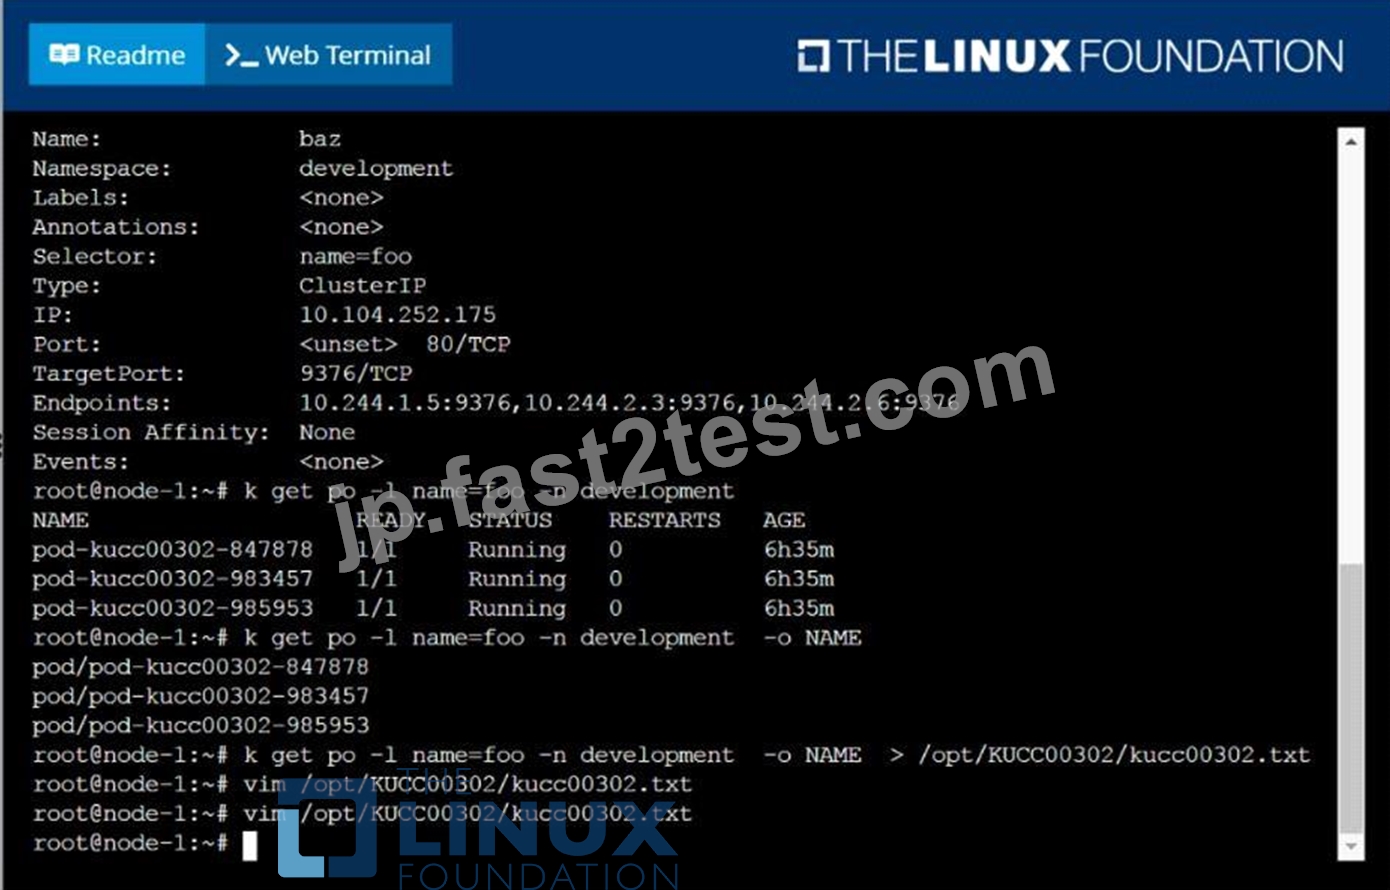
Create a file:
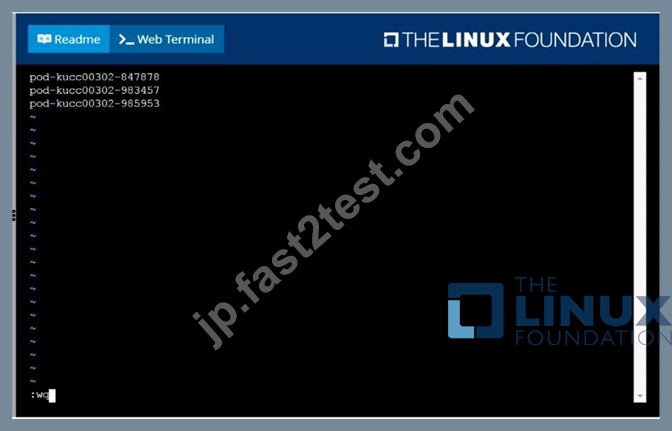
/opt/KUCC00302/kucc00302.txt that lists all pods that implement service baz in namespace development.
The format of the file should be one pod name per line.
正解:
解説:
solution
質問 # 59
Scale the deployment webserver to 6 pods.
正解:
解説:
solution
質問 # 60
You are running a critical application on Kubernetes that requires high availability. To ensure the application stays operational even if one or more nodes experience failures, you decide to implement a pod anti-affinity rule. Explain how you can configure an anti-affinity rule to prevent pods from being scheduled on the same node.
正解:
解説:
See the solution below with Step by Step Explanation.
Explanation:
Solution (Step by Step) :
1 . Define the Anti-Affinity Rule: Add an 'affinity' section to the 'spec.template.spec' of your Deployment or StatefulSet. Within , define a podAntiAffinity' section, specifying that pods with the same label should not be placed on the same node.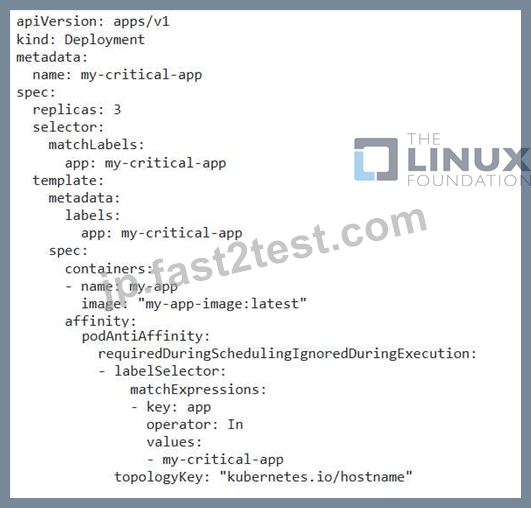
2. Use 'requiredDuringSchedulinglgnoredDuringExecution': The 'requiredDuringSchedulinglgnoredDuringExecutioru section ensures that the rule is enforced during pod scheduling. Once a pod is scheduled, the rule is ignored. This ensures that even if a node fails, the remaining pods are not affected. 3. Set 'topologyKey': The 'topologyKey' is set to 'kubernetes.io/hostname'. This tells Kubernetes to consider the node's hostname for pod placement. It will prevent pods with the label 'app: my-critical-app' from being scheduled on the same node. 4. Verify the Deployment: Apply the YAML file to your cluster using 'kubectl apply -f my-critical-app.yaml'. You can then check the status of your Deployment using 'kubectl get pods -l app=my-critical-app' to verify that the pods are distributed across different nodes.
質問 # 61
......
CKA試験問題集でPDF問題とテストエンジン:https://jp.fast2test.com/CKA-premium-file.html
リアルCKA試験問題集解答で有効なCKA問題集PDF:https://drive.google.com/open?id=1RvDZG4jdQlvfTKLS3XkRqfreTJhliFv1