

[2023年12月]更新のMicrosoft MD-102テストエンジンとPDFで完全版無料問題集を無料提供
最新版を今すぐ試そうMD-102認定有効な試験問題集
Microsoft MD-102 認定試験の出題範囲:
| トピック | 出題範囲 |
|---|---|
| トピック 1 |
|
| トピック 2 |
|
| トピック 3 |
|
| トピック 4 |
|
| トピック 5 |
|
| トピック 6 |
|
| トピック 7 |
|
| トピック 8 |
|
| トピック 9 |
|
| トピック 10 |
|
| トピック 11 |
|
| トピック 12 |
|
質問 # 63
You have a Microsoft 365 E5 subscription that contains 500 macOS devices enrolled in Microsoft Intune.
You need to ensure that you can apply Microsoft Defender for Endpoint antivirus policies to the macOS devices. The solution must minimize administrative effort.
What should you do?
- A. From the Microsoft Endpoint Manager admin center, create a configuration profile.
- B. From the Microsoft Endpoint Manager admin center, create a security baseline.
- C. Onboard the macOS devices to the Microsoft 365 compliance center.
- D. Install Defender for Endpoint on the macOS devices.
正解:D
解説:
Just install, and use Defender for Endpoint on Mac.
質問 # 64
You have a Microsoft 365 subscription that uses Microsoft Intune Suite.
You use Microsoft Intune to manage devices.
You need to configure an update ring that meets the following requirements:
* Fixes and improvements to existing Windows functionality can be deferred for 14 days but will install automatically seven days after that date.
* The installation of new Windows features can be deferred for 90 days but will install automatically 10 days after that date.
* Devices must restart automatically three days after an update is installed.
How should you configure the update ring? To answer, select the appropriate options in the answer area.
NOTE: Each correct selection is worth one point.
正解:
解説:
Explanation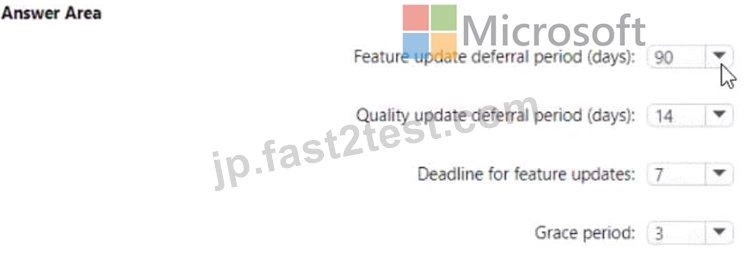
質問 # 65
You have a Microsoft Intune subscription.
You have devices enrolled in intune as shown in the following table.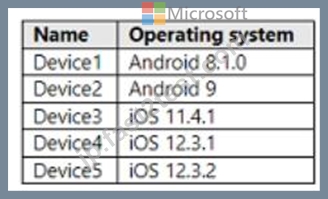
An app named App1 is installed on each device.
What is the minimum number of app configuration policies required to manage Appl ?
- A. 0
- B. 1
- C. 2
- D. 3
- E. 4
正解:D
解説:
The correct answer is B because you need to create two app configuration policies for managed devices, one for iOS/iPadOS devices and one for Android devices1. App configuration policies let you customize the settings of apps for iOS/iPadOS or Android devices1. The settings are assigned to user groups and applied when the app runs1. The app developer or supplier provides the configuration settings (keys and values) that are exposed to Intune1. You can't use a single app configuration policy for both iOS/iPadOS and Android devices because they have different configuration settings2. Reference: 1: App configuration policies for Microsoft Intune | Microsoft Learn https://learn.microsoft.com/en-us/mem/intune/apps/app-configuration-policies-overview 2: Add app configuration policies for managed iOS/iPadOS devices | Microsoft Learn https://learn.microsoft.com/en-us/mem/intune/apps/app-configuration-policies-use-ios
質問 # 66
You have a Microsoft Deployment Toolkit (MDT) deployment share.
From the Deployment Workbench, you open the New Task Sequence Wizard and select the Standard Client Upgrade Task Sequence task sequence template.
You discover that there are no operating system images listed on the Select OS page as shown in the following exhibit.
You need to be able to select an operating system image to perform a Windows 11 in-place upgrade.
What should you do?
- A. Import a full set of source files.
- B. Enable monitoring for the deployment share.
- C. Run the Update Deployment Share Wizard
- D. Import a custom image file.
正解:C
質問 # 67
You have a Microsoft 365 E5 subscription that contains 100 iOS devices enrolled in Microsoft Intune.
You need to ensure that notifications of iOS updates are deferred for 30 days after the updates are released.
What should you create?
- A. a device configuration profile based on the Device features template
- B. an iOS app provisioning profile
- C. a device configuration profile based on the Device restrictions template
- D. an update policy for iOS/iPadOS
正解:D
解説:
Manage iOS/iPadOS software update policies in Intune, delay visibility of software updates.
When you use update policies for iOS, you might have need to delay visibility of an iOS software update. Reasons to delay visibility include:
Prevent users from updating the OS manually
To deploy an older update while preventing users from installing a more recent one To delay visibility, deploy a device restriction template that configures the following settings:
Defer software updates = Yes
This doesn't affect any scheduled updates. It represents days before software updates are visible to end users after release.
Delay default visibility of software updates = 1 to 90
90 days is the maximum delay that Apple supports.
質問 # 68
You have the on-premises servers shown in the following table.
You have a Microsoft 365 E5 subscription that contains Android and iOS devices. All the devices are managed by using Microsoft Intune.
You need to implement Microsoft Tunnel for Intune. The solution must minimize the number of open firewall ports.
To which server can you deploy a Tunnel Gateway server, and which inbound ports should be allowed on the server to support Microsoft Tunnel connections? To answer, select the appropriate options in the answer area.
NOTE: Each correct selection is worth one point.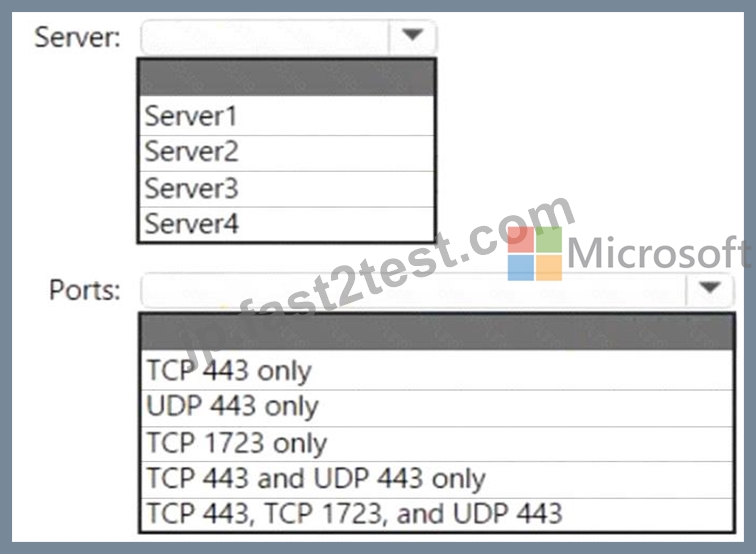
正解:
解説:
Explanation
Box 1: Server4
Microsoft Tunnel is a VPN gateway solution for Microsoft Intune that runs in a container on Linux and allows access to on-premises resources from iOS/iPadOS and Android Enterprise devices using modern authentication and Conditional Access.
Box 2: TCP 443 and UDP 443 only
Some traffic goes to your public facing IP address for the Tunnel. The VPN channel will use TCP, TLS, UDP, and DTLS over port 443.
By default, port 443 is used for both TCP and UDP, but this can be customized via the Intune Saerver Configuration - Server port setting. If changing the default port (443) ensure your inbound firewall rules are adjusted to the custom port.
Incorrect:
TCP 1723 is not used.
Reference: https://docs.microsoft.com/en-us/mem/intune/protect/microsoft-tunnel-overview
質問 # 69
You need to meet the technical requirements for Windows AutoPilot.
Which two settings should you configure from the Azure Active Directory blade? To answer, select the appropriate settings in the answer area.
NOTE: Each correct selection is worth one point.
正解:
解説:
Explanation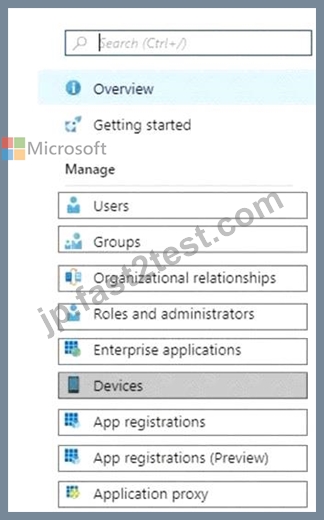
References:
https://docs.microsoft.com/en-us/windows/deployment/windows-autopilot/windows-autopilot-reset
質問 # 70
You need to recommend a solution to meet the device management requirements.
What should you include in the recommendation? To answer, select the appropriate options in the answer area.
NOTE: Each correct selection is worth one point.
正解:
解説: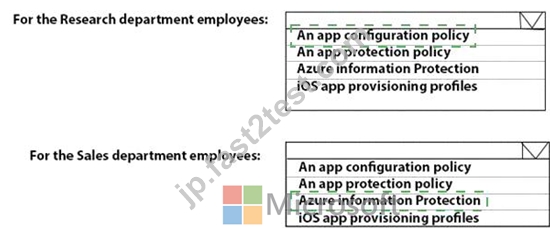
Explanation
Reference:
https://github.com/MicrosoftDocs/IntuneDocs/blob/master/intune/app-protection-policy.md
https://docs.microsoft.com/en-us/azure/information-protection/configure-usage-rights#do-not-forward-option-for
質問 # 71
You use Windows Admin Center to remotely administer computers that run Windows 10.
When connecting to Windows Admin Center, you receive the message shown in the following exhibit.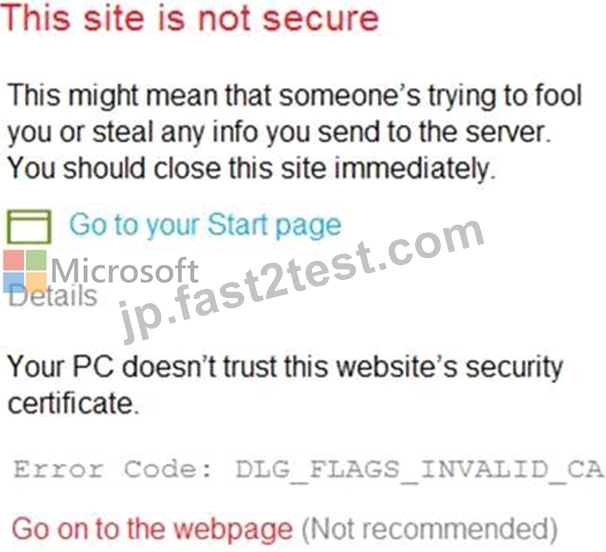
You need to prevent the message from appearing when you connect to Windows Admin Center.
To which certificate store should you import the certificate?
- A. Trusted Root Certification Authorities
- B. Personal
- C. Client Authentication Issuers
正解:A
質問 # 72
You have 100 Windows 10 devices enrolled in Microsoft Intune.
You need to configure the devices to retrieve Windows updates from the internet and from other computers on a local network.
Which Delivery Optimization setting should you configure, and which type of Intune object should you create? To answer, select the appropriate options in the answer area.
NOTE: Each correct selection is worth one point.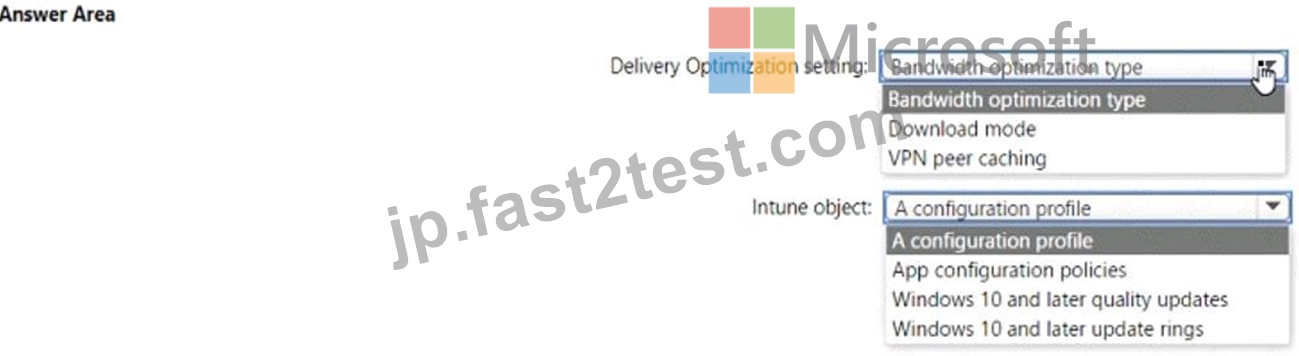
正解:
解説:
Explanation
Delivery Optimization setting: B. Download mode Intune object: A configuration profile To configure the devices to retrieve Windows updates from the internet and from other computers on a local network, you need to configure the Download mode setting in a Delivery Optimization device configuration profile. This setting specifies how the devices use Delivery Optimization to download updates. You can choose from several options, such as HTTP only, LAN only, or Group. For example, you can set the Download mode to Group and specify a group ID for the devices to share updates among themselves and with other devices that have the same group ID. You can also set the Download mode to Internet to allow the devices to download updates from Microsoft or other devices on the internet that use Delivery Optimization.
References: https://docs.microsoft.com/en-us/mem/intune/configuration/delivery-optimization-windows
質問 # 73
You have 200 computers that run Windows 10 and are joined to an Active Directory domain.
You need to enable Windows Remote Management (WinRM) on all the computers by using Group Policy.
Which three actions should you perform? Each correct answer presents part of the solution.
NOTE: Each correct selection is worth one point.
- A. Set the Startup Type of the Remote Registry service to Automatic
- B. Enable the Windows Defender Firewall: Allow inbound remote administration exception setting.
- C. Set the Startup Type of the Windows Remote Management (WS-Management) service to Automatic.
- D. Enable the Allow remote server management through WinRM setting.
- E. Enable the Windows Defender Firewall: Allow inbound Remote Desktop exceptions setting.
- F. Enable the Allow Remote Shell access setting.
正解:B、C、D
解説:
Explanation
To enable WinRM on domain computers using Group Policy, you need to perform the following actions:
Enable the Allow remote server management through WinRM setting under Computer Configuration > Policies > Administrative Templates > Windows Components > Windows Remote Management (WinRM) > WinRM Service. This setting allows you to specify the IP address ranges that can connect to the WinRM service.
Set the Startup Type of the Windows Remote Management (WS-Management) service to Automatic under Computer Configuration > Preferences > Control Panel Settings > Services. This setting ensures that the WinRM service starts automatically on the computers.
Enable the Windows Defender Firewall: Allow inbound remote administration exception setting under Computer Configuration > Policies > Security Settings > Windows Firewall and Advanced Security > Windows Firewall and Advanced Security > Inbound Rules. This setting creates a firewall rule that allows incoming TCP connections on port 5985 for WinRM. References: How to Enable WinRM via Group Policy, Installation and configuration for Windows Remote Management
質問 # 74
You have a Microsoft 365 subscription that contains 1,000 Android devices enrolled in Microsoft Intune. You create an app configuration policy that contains the following settings:
* Device enrollment type: Managed devices
* Profile Type: All Profile Types
* Platform: Android Enterprise
Which two types of apps can be associated with the policy? Each correct answer presents a complete solution.
NOTE: Each correct selection is worth one point.
- A. Web link
- B. Android Enterprise system app
- C. Built-in Android app
- D. Managed Google Play store app
- E. Android store app
正解:B、D
質問 # 75
What should you upgrade before you can configure the environment to support co-management?
- A. Windows Server Update Services (WSUS)
- B. the domain controllers
- C. Configuration Manager
- D. the domain functional level
正解:C
解説:
Explanation
References:
https://docs.microsoft.com/en-us/sccm/comanage/tutorial-co-manage-clients
Topic 2, Case Study Contoso, Ltd.Overview
Contoso, Ltd. is a consulting company that has a main office in Montreal and branch offices in Seattle and New York.
Contoso has a Microsoft 365 E5 subscription.
Network Environment
The network contains an on-premises Active domain named Contoso.com. The domain contains the servers shown in the following table.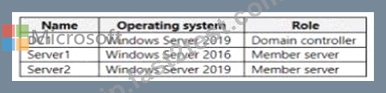
Contoso has a hybrid Azure Active Directory (Azure AD) tenant named Contoso.com.
Contoso has a Microsoft Store for Business instance.
Users and Groups
The Contoso.com tenant contains the users shown in the following table.
All users are assigned a Microsoft Office 365 license and an Enterprise Mobility + Security E3 license.
Enterprise State Roaming is enabled for Group1 and GroupA.
Group and Group have a Membership type of Assign
Devices
Contoso has the Windows 10 devices shown in the following table.
The Windows 10 devices are joined to Azure AD and enrolled in Microsoft intune.
The Windows 10 devices are configured as shown in the following table.
All the Azure AD joined devices have an executable file named C:\AppA.exe and a folder named D:\Folder 1.
Microsoft Endpoint Manager Configuration
Microsoft Endpoint Manager has the compliance policies shown in the following table.
The Compliance policy settings are shown in the following exhibit.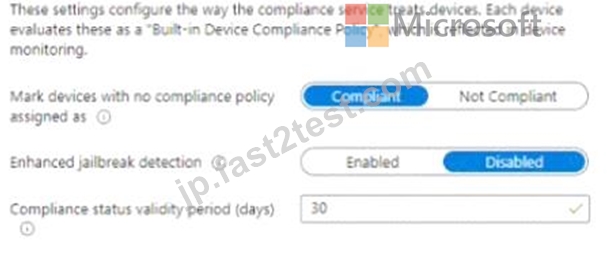
The Automatic Enrolment settings have the following configurations:
* MDM user scope GroupA
* MAM user scope: GroupB
You have an Endpoint protection configuration profile that has the following Controlled folder access settings:
* Name: Protection1
* Folder protection: Enable
* List of apps that have access to protected folders: CV\AppA.exe
* List of additional folders that need to be protected: D:\Folderi1
* Assignments
Windows Autopilot Configuration
Currently, there are no devices deployed by using Window Autopilot
The Intune connector tor Active Directory is installed on Server 1.
Planned Changes
Contoso plans to implement the following changes:
* Purchase a new Windows 10 device named Device6 and enroll the device in Intune.
* New computers will be deployed by using Windows Autopilot and will be hybrid Azure AO joined.
* Deploy a network boundary configuration profile that will have the following settings:
* Name Boundary 1
* Network boundary 192.168.1.0/24
* Scope tags: Tag 1
* Assignments;
* included groups: Group 1. Group2
* Deploy two VPN configuration profiles named Connection! and Connection that will have the following settings:
* Name: Connection 1
* Connection name: VPNI
* Connection type: L2TP
* Assignments:
* Included groups: Group1. Group2, GroupA
* Excluded groups: -
* Name: Connection
* Connection name: VPN2
* Connection type: IKEv2 i Assignments:
* included groups: GroupA
* Excluded groups: GroupB
* Purchase an app named App1 that is available in Microsoft Store for Business and to assign the app to all the users.
Technical Requirements
Contoso must meet the following technical requirements:
* Users in GroupA must be able to deploy new computers.
* Administrative effort must be minimized.
質問 # 76
You have two computers named Computer1 and Computed that run Windows 10. Computed has Remote Desktop enabled.
From Computer1, you connect to Computer2 by using Remote Desktop Connection.
You need to ensure that you can access the local drives on Computer1 from within the Remote Desktop session.
What should you do?
- A. From Computer 2, configure the Remote Desktop settings.
- B. From Windows Defender Firewall on Computer 2, allow File and Printer Sharing.
- C. From Windows Defender Firewall on Computer 1, allow Remote Desktop.
- D. From Computer1, configure the Remote Desktop Connection settings.
正解:D
質問 # 77
You have an Azure AD tenant named contoso.com that contains the devices shown in the following table.
AH devices contain an app named App1 and are enrolled in Microsoft Intune.
You need to prevent users from copying data from App1 and pasting the data into other apps.
Which type of policy and how many policies should you create in Intune? To answer, select the appropriate options in the answer area.
NOTE: Each correct selection is worth one point.
正解:
解説:
Explanation
Policy type: App protection policy Minimum number of policies: 1 Comprehensive Explanation of Correct Answer Only: The correct answer is app protection policy because it allows you to customize the settings of apps for iOS/iPadOS or Android devices1. One of the settings you can configure is Restrict cut, copy, and paste between other apps, which lets you prevent users from copying data from App1 and pasting the data into other apps2. You only need one policy to apply this setting to all devices that have App1 installed1.
References: 1: App configuration policies for Microsoft Intune | Microsoft Learn
https://learn.microsoft.com/en-us/mem/intune/apps/app-configuration-policies-overview 2: Troubleshoot restricting cut, copy, and paste between applications - Intune | Microsoft Learn
https://learn.microsoft.com/en-us/troubleshoot/mem/intune/app-protection-policies/troubleshoot-cut-copy-paste
質問 # 78
You have a Microsoft Intune subscription.
You are creating a Windows Autopilot deployment profile named Profile1 as shown in the following exhibit.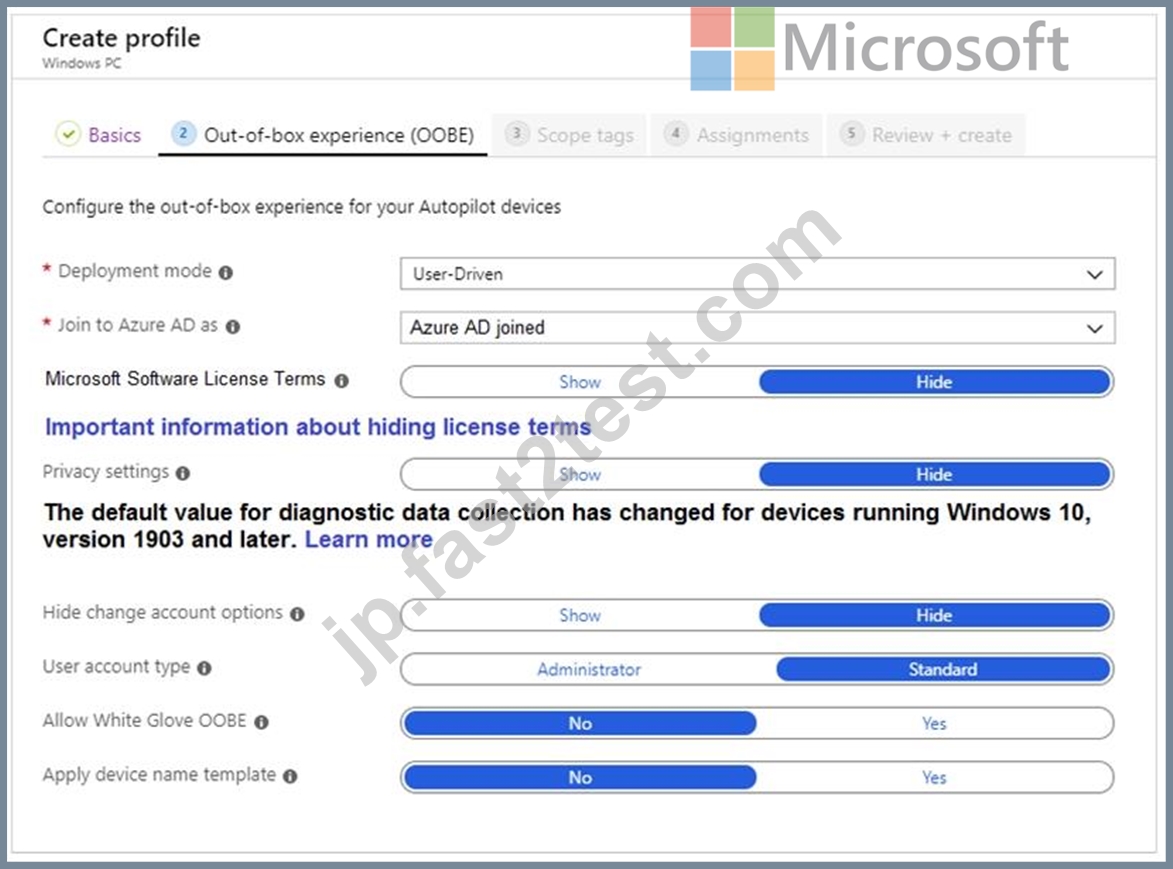
Use the drop-down menus to select the answer choice that completes each statement based on the information presented in the graphic.
NOTE: Each correct selection is worth one point.
正解:
解説: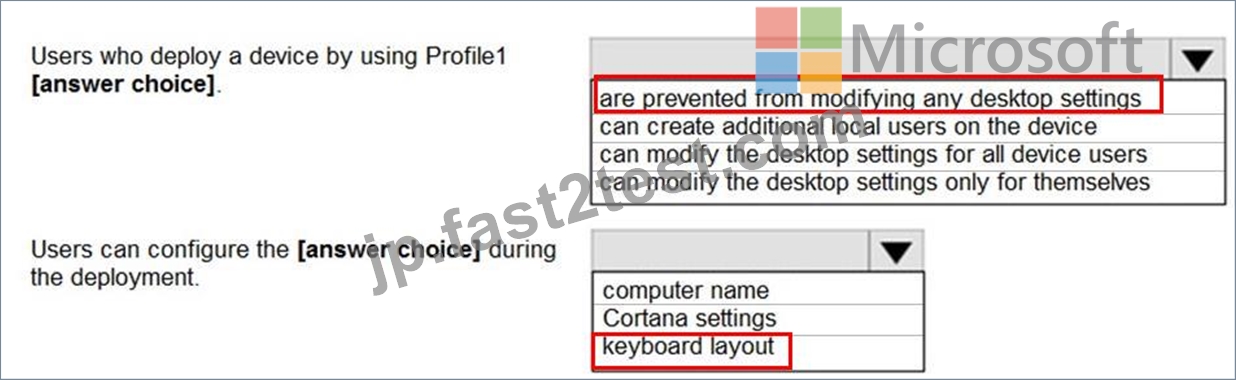
質問 # 79
......
100%合格保証付きの素晴らしいMD-102試験問題PDF:https://jp.fast2test.com/MD-102-premium-file.html
MD-102問題集で2023年最新のMicrosoft試験問題:https://drive.google.com/open?id=1Ncc2bX64hp1AB3bu2C9fLAMIb1DTFLk_