

ベストな準備プラン350-701試験2024年最新のCCNP Security無制限630問題
注目すべき時短になる350-701オールインワン試験ガイド
Cisco 350-701(Implementing and Operating Cisco Security Core Technologies)認定試験は、Cisco Security Core Technologiesの実装と運用に関する知識とスキルを持つ個人を認定する世界的に認知された認定試験です。この認定試験は、ネットワークセキュリティの分野でキャリアアップを望むセキュリティプロフェッショナルを対象としています。
Cisco 350-701試験は、ITプロフェッショナルのCiscoセキュリティコアテクノロジーの実装と運用のスキルと知識を認定する認定試験です。この試験は、Ciscoネットワーク、デバイス、アプリケーションのセキュリティに責任を持つ個人のために設計されています。認定は、Cisco Certified Network Professional(CCNP)セキュリティトラックの一部であり、Cisco Certified Internetwork Expert(CCIE)セキュリティ認定の前提条件です。
質問 # 105
What is an attribute of the DevSecOps process?
- A. mandated security controls and check lists
- B. security scanning and theoretical vulnerabilities
- C. isolated security team
- D. development security
正解:D
解説:
DevSecOps (development, security, and operations) is a concept used in recent years to describe how to move security activities to the start of the development life cycle and have built-in security practices in the continuous integration/continuous deployment (CI/CD) pipeline. Thus minimizing vulnerabilities and bringing security closer to IT and business objectives.
Three key things make a real DevSecOps environment:
+ Security testing is done by the development team.
+ Issues found during that testing is managed by the development team.
+ Fixing those issues stays within the development team.
質問 # 106
Drag and drop the suspicious patterns for the Cisco Tetration platform from the left onto the correct definitions on the right.
正解:
解説:
質問 # 107
After a recent breach, an organization determined that phishing was used to gain initial access to the network before regaining persistence. The information gained from the phishing attack was a result of users visiting known malicious websites. What must be done in order to prevent this from happening in the future?
- A. Modify an access policy.
- B. Modify identification profiles.
- C. Modify web proxy settings
- D. Modify outbound malware scanning policies
正解:C
解説:
Reference: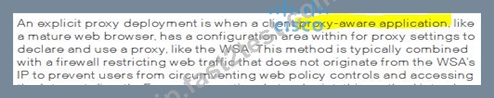
質問 # 108
What must be configured in Cisco ISE to enforce reauthentication of an endpoint session when an endpoint is deleted from an identity group?
- A. CoA
- B. posture assessment
- C. SNMP probe
- D. external identity source
正解:A
解説:
Cisco ISE allows a global configuration to issue a Change of Authorization (CoA) in the Profiler Configuration page that enables the profiling service with more control over endpoints that are already authenticated.
One of the settings to configure the CoA type is "Reauth". This option is used to enforce reauthentication of an already authenticated endpoint when it is profiled.
Reference:
b_ise_admin_guide_sample_chapter_010101.html
b_ise_admin_guide_sample_chapter_010101.html
質問 # 109
Refer to the exhibit.
How does Cisco Umbrella manage traffic that is directed toward risky domains?
- A. Traffic is managed by the security settings and blocked.
- B. Traffic is proximed through the intelligent proxy.
- C. Traffic is managed by the application settings, unhandled and allowed.
- D. Traffic is allowed but logged.
正解:A
質問 # 110
Drag and drop the suspicious patterns for the Cisco Tetration platform from the left onto the correct definitions on the right.
正解:
解説:
質問 # 111
A network engineer is configuring DMVPN and entered the crypto isakmp key cisc0380739941 address 0.0.0.0 command on host A.
The tunnel is not being established to hostB. What action is needed to authenticate the VPN?
- A. Enter the command with a different password on hostB.
- B. Change the password on hostA to the default password.
- C. Enter the same command on hostB.
- D. Change isakmp to ikev2 in the command on hostA.
正解:C
質問 # 112
DRAG DROP
Drag and drop the Firepower Next Generation Intrusion Prevention System detectors from the left onto the correct definitions on the right.
Select and Place:
正解:
解説:
Explanation/Reference: https://www.cisco.com/c/en/us/td/docs/security/firepower/640/configuration/guide/fpmc-config- guide-v64/detecting_specific_threats.html
質問 # 113
An engineer recently completed the system setup on a Cisco WSA Which URL information does the system send to SensorBase Network servers?
- A. none because SensorBase Network Participation is disabled by default
- B. Summarized server-name information and MD5-hashed path information
- C. URL information collected from clients that connect to the Cisco WSA using Cisco AnyConnect
- D. complete URL,without obfuscating the path segments
正解:D
質問 # 114
How does Cisco Advanced Phishing Protection protect users?
- A. It determines which identities are perceived by the sender
- B. It utilizes sensors that send messages securely.
- C. It uses machine learning and real-time behavior analytics.
- D. It validates the sender by using DKIM.
正解:C
解説:
Reference:
https://www.cisco.com/c/dam/en/us/products/collateral/security/cloud-email-security/at-a-glance-c45-740894.pdf
質問 # 115
Which two features of Cisco DNA Center are used in a Software Defined Network solution? (Choose two)
- A. assurance
- B. automation
- C. authentication
- D. accounting
- E. encryption
正解:A、B
解説:
What Cisco DNA Center enables you to do
Automate: Save time by using a single dashboard to manage and automate your network. Quickly scale your business with intuitive workflows and reusable templates. Configure and provision thousands of network devices across your enterprise in minutes, not hours.
Secure policy: Deploy group-based secure access and network segmentation based on business needs. With Cisco DNA Center, you apply policy to users and applications instead of to your network devices. Automation reduces manual operations and the costs associated with human errors, resulting in more uptime and improved security. Assurance then assesses the network and uses context to turn data into intelligence, making sure that changes in the network device policies achieve your intent.
Assurance: Monitor, identify, and react in real time to changing network and wireless conditions. Cisco DNA Center uses your network's wired and wireless devices to create sensors everywhere, providing real-time feedback based on actual network conditions. The Cisco DNA Assurance engine correlates network sensor insights with streaming telemetry and compares this with the current context of these data sources. With a quick check of the health scores on the Cisco DNA Center dashboard, you can see where there is a performance issue and identify the most likely cause in minutes.
Extend ecosystem: With the new Cisco DNA Center platform, IT can now integrate Cisco® solutions and thirdparty technologies into a single network operation for streamlining IT workflows and increasing business value and innovation. Cisco DNA Center allows you to run the network with open interfaces with IT and business applications, integrates across IT operations and technology domains, and can manage heterogeneous network devices.
Reference:
What Cisco DNA Center enables you to do
Automate: Save time by using a single dashboard to manage and automate your network. Quickly scale your business with intuitive workflows and reusable templates. Configure and provision thousands of network devices across your enterprise in minutes, not hours.
Secure policy: Deploy group-based secure access and network segmentation based on business needs. With Cisco DNA Center, you apply policy to users and applications instead of to your network devices. Automation reduces manual operations and the costs associated with human errors, resulting in more uptime and improved security. Assurance then assesses the network and uses context to turn data into intelligence, making sure that changes in the network device policies achieve your intent.
Assurance: Monitor, identify, and react in real time to changing network and wireless conditions. Cisco DNA Center uses your network's wired and wireless devices to create sensors everywhere, providing real-time feedback based on actual network conditions. The Cisco DNA Assurance engine correlates network sensor insights with streaming telemetry and compares this with the current context of these data sources. With a quick check of the health scores on the Cisco DNA Center dashboard, you can see where there is a performance issue and identify the most likely cause in minutes.
Extend ecosystem: With the new Cisco DNA Center platform, IT can now integrate Cisco® solutions and thirdparty technologies into a single network operation for streamlining IT workflows and increasing business value and innovation. Cisco DNA Center allows you to run the network with open interfaces with IT and business applications, integrates across IT operations and technology domains, and can manage heterogeneous network devices.
質問 # 116
What is the most commonly used protocol for network telemetry?
- A. SMTP
- B. SNMP
- C. TFTP
- D. NctFlow
正解:D
質問 # 117
Which feature requires a network discovery policy on the Cisco Firepower Next Generation Intrusion Prevention System?
- A. Health Monitoring
- B. URL Filtering
- C. Impact Flags
- D. Security Intelligence
正解:A
解説:
A network discovery policy is required for the health monitoring feature on the Cisco Firepower Next Generation Intrusion Prevention System (NGIPS). Health monitoring allows the system to collect and display information about the health and performance of the managed devices, such as CPU, memory, disk, and interface utilization, as well as the status of various processes and services. Health monitoring also enables the system to generate alerts and notifications when certain thresholds or conditions are met or violated.
To enable health monitoring, the system must have access to the network data from the managed devices, which is provided by the network discovery policy. The network discovery policy controls how the system collects data on the network assets and which network segments and ports are monitored. The network discovery policy also specifies the zones to which the policy is deployed, which determines the scope of the health monitoring data. Without a network discovery policy, the system cannot perform health monitoring on the NGIPS devices.
References :=
1: Network Discovery Policies, Cisco Firepower Management Center Configuration Guide, Version 7.0, page
1. 2: Health Monitoring, Cisco Firepower Management Center Configuration Guide, Version 7.0, page 1.
質問 # 118
Which Cisco Firewall solution requires zone definition?
- A. ZBFW
- B. CBAC
- C. Cisco AMP
- D. Cisco ASA
正解:A
質問 # 119
Which term describes when the Cisco Firepower downloads threat intelligence updates from Cisco Talos?
- A. sharing
- B. analysis
- C. authoring
- D. consumption
正解:D
解説:
... we will showcase Cisco Threat Intelligence Director (CTID) an exciting feature on Cisco's Firepower Management Center (FMC) product offering that automates the operationalization of threat intelligence. TID has the ability to consume threat intelligence via STIX over TAXII and allows uploads/downloads of STIX and simple blacklists. Reference: https://blogs.cisco.com/developer/automate-threat-intelligence-using-cisco-threat-intelligencedirector
質問 # 120
What does Cisco AMP for Endpoints use to help an organization detect different families of malware?
- A. Ethos Engine to perform fuzzy fingerprinting
- B. Spero Engine with machine learning to perform dynamic analysis
- C. Tetra Engine to detect malware when me endpoint is connected to the cloud
- D. Clam AV Engine to perform email scanning
正解:A
解説:
Reference: https://docs.amp.cisco.com/AMP%20for%20Endpoints%20User%20Guide.pdfETHOS = Fuzzy Fingerprinting using static/passive heuristics Reference: https://www.ciscolive.com/c/dam/r/ciscolive/emea/docs/2016/pdf/BRKSEC-2139.pdf
質問 # 121
Which technology must be used to implement secure VPN connectivity among company branches over a private IP cloud with any-to-any scalable connectivity?
- A. IPsec DVTI
- B. DMVPN
- C. GET VPN
- D. FlexVPN
正解:C
解説:
Explanation Cisco's Group Encrypted Transport VPN (GETVPN) introduces the concept of a trusted group to eliminate point-to-point tunnels and their associated overlay routing. All group members (GMs) share a common security association (SA), also known as a group SA. This enables GMs to decrypt traffic that was encrypted by any other GM. GETVPN provides instantaneous large-scale any-to-any IP connectivity using a group IPsec security paradigm. Reference: https://www.cisco.com/c/dam/en/us/products/collateral/security/group-encrypted-transport-vpn/ GETVPN_DIG_version_2_0_External.pdf
質問 # 122
Drag and drop the Firepower Next Generation Intrustion Prevention System detectors from the left onto the correct definitions on the right.
正解:
解説:
Explanation
Reference:
https://www.cisco.com/c/en/us/td/docs/security/firepower/640/configuration/guide/fpmc-configguide-v64/detecti
質問 # 123
An engineer has been tasked with configuring a Cisco FTD to analyze protocol fields and detect anomalies in the traffic from industrial systems. What must be done to meet these requirements?
- A. Configure intrusion rules for the DNP3 preprocessor
- B. Implement pre-filter policies for the CIP preprocessor
- C. Enable traffic analysis in the Cisco FTD
- D. Modify the access control policy to trust the industrial traffic
正解:B
解説:
The Modbus, DNP3, and CIP SCADA preprocessors detect traffic anomalies and provide data to intrusion rules. Therefore in this question only answer A or answer C is correct. The DNP3 preprocessor detects anomalies in DNP3 traffic and decodes the DNP3 protocol for processing by the rules engine, which uses DNP3 keywords to access certain protocol fields. The Common Industrial Protocol (CIP) is a widely used application protocol that supports industrial automation applications. EtherNet/IP is an implementation of CIP that is used on Ethernet-based networks.The CIP preprocessor detects CIP and ENIP traffic running on TCP or UDP and sends it to the intrusion rules engine. You can use CIP and ENIP keywords in custom intrusion rules to detect attacks in CIP and ENIP traffic. Reference: https://www.cisco.com/c/en/us/td/docs/security/firepower/630/configuration/guide/fpmc-configguide-v63/scada_preprocessors.html Both DNP3 and CIP preprocessors can be used to detect traffic anomalies but we choose CIP as it is widely used in industrial applications. Note: + An intrusion rule is a specified set of keywords and arguments that the system uses to detect attempts to exploit vulnerabilities in your network. As the system analyzes network traffic, it compares packets against the conditions specified in each rule, and triggers the rule if the data packet meets all the conditions specified in the rule. + Preprocessor rules, which are rules associated with preprocessors and packet decoder detection options in the network analysis policy. Most preprocessor rules are disabled by default.
rules. Therefore in this question only answer A or answer C is correct.
The DNP3 preprocessor detects anomalies in DNP3 traffic and decodes the DNP3 protocol for processing by the rules engine, which uses DNP3 keywords to access certain protocol fields.
The Common Industrial Protocol (CIP) is a widely used application protocol that supports industrial automation applications. EtherNet/IP is an implementation of CIP that is used on Ethernet-based networks.The CIP preprocessor detects CIP and ENIP traffic running on TCP or UDP and sends it to the intrusion rules engine.
You can use CIP and ENIP keywords in custom intrusion rules to detect attacks in CIP and ENIP traffic.
Reference:
Both DNP3 and CIP preprocessors can be used to detect traffic anomalies but we choose CIP as it is widely used in industrial applications.
Note:
The Modbus, DNP3, and CIP SCADA preprocessors detect traffic anomalies and provide data to intrusion rules. Therefore in this question only answer A or answer C is correct. The DNP3 preprocessor detects anomalies in DNP3 traffic and decodes the DNP3 protocol for processing by the rules engine, which uses DNP3 keywords to access certain protocol fields. The Common Industrial Protocol (CIP) is a widely used application protocol that supports industrial automation applications. EtherNet/IP is an implementation of CIP that is used on Ethernet-based networks.The CIP preprocessor detects CIP and ENIP traffic running on TCP or UDP and sends it to the intrusion rules engine. You can use CIP and ENIP keywords in custom intrusion rules to detect attacks in CIP and ENIP traffic. Reference: https://www.cisco.com/c/en/us/td/docs/security/firepower/630/configuration/guide/fpmc-configguide-v63/scada_preprocessors.html Both DNP3 and CIP preprocessors can be used to detect traffic anomalies but we choose CIP as it is widely used in industrial applications. Note: + An intrusion rule is a specified set of keywords and arguments that the system uses to detect attempts to exploit vulnerabilities in your network. As the system analyzes network traffic, it compares packets against the conditions specified in each rule, and triggers the rule if the data packet meets all the conditions specified in the rule. + Preprocessor rules, which are rules associated with preprocessors and packet decoder detection options in the network analysis policy. Most preprocessor rules are disabled by default.
質問 # 124
......
合格保証付き350-701問題集:https://jp.fast2test.com/350-701-premium-file.html
あなたを合格さすCisco 350-701試験専門はここにある:https://drive.google.com/open?id=1DaRuGygIhRd3Z4slTxsz-yDnSKgt04Q8