

Palo Alto Networks PCCSEテストエンジン練習テスト問題、試験問題集
100%無料PCCSE日常練習試験には250問があります
質問 # 33
What is the function of the external ID when onboarding a new Amazon Web Services (AWS) account in Prisma Cloud?
- A. It is the default name of the PrismaCloudApp stack.
- B. It is a UUID that establishes a trust relationship between the Prisma Cloud account and the AWS account in order to extract data.
- C. It is the resource name for the Prisma Cloud Role.
- D. It is a unique identifier needed only when Monitor & Protect mode is selected.
正解:B
解説:
The external ID plays a crucial role when onboarding a new Amazon Web Services (AWS) account in Prisma Cloud. It serves as a UUID (Universally Unique Identifier) that establishes a trust relationship between the Prisma Cloud account and the AWS account. This trust relationship is essential for allowing Prisma Cloud to securely extract data and perform security monitoring and compliance checks within the AWS environment. The use of an external ID ensures that Prisma Cloud can access the necessary information from the AWS account without compromising the security of the AWS account's credentials, adhering to the principle of least privilege and enhancing the overall security posture.
質問 # 34
When would a policy apply if the policy is set under Defend > Vulnerability > Images > Deployed?
- A. when a serverless repository is scanned
- B. when the Image is built
- C. when a Container is started form an Image
- D. when the Image is built and when a Container is started form an Image
正解:D
質問 # 35
The administrator wants to review the Console audit logs from within the Console Which page in the Console should the administrator use to review this data, if it can be reviewed at all?
- A. The audit logs can be viewed only externally to the Console
- B. Navigate to Monitor > Events > Host Log Inspection
- C. Navigate to Manage > Defenders > View Logs
- D. Navigate to Manage > View Logs > History
正解:D
質問 # 36
Which two statements are true about the differences between build and run config policies? (Choose two.)
- A. Build and Audit Events policies belong to the configuration policy set.
- B. Build policies enable you to check for security misconfigurations in the IaC templates and ensure that these issues do not get into production.
- C. Run policies monitor resources, and check for potential issues after these cloud resources are deployed.
- D. Run policies monitor network activities in your environment, and check for potential issues during runtime.
- E. Run and Network policies belong to the configuration policy set.
正解:B、C
解説:
In the context of Prisma Cloud, Build and Run policies serve distinct purposes in securing cloud environments. Build policies are designed to evaluate Infrastructure as Code (IaC) templates before deployment. These policies help identify and remediate security misconfigurations in the development phase, ensuring that vulnerabilities are addressed before the infrastructure is provisioned. This proactive approach enhances security by preventing misconfigurations from reaching production environments.
On the other hand, Run policies are applied to resources that are already deployed in the cloud. These policies continuously monitor the cloud environment, detecting and alerting on potential security issues that arise in the runtime. Run policies help maintain the security posture of cloud resources by identifying deviations from established security baselines and enabling quick remediation of identified issues.
Both Build and Run policies are integral to a comprehensive cloud security strategy, addressing security concerns at different stages of the cloud resource lifecycle-from development and deployment to ongoing operation.
質問 # 37
The development team wants to block Cross Site Scripting attacks from pods its environment How should the team construct the CNAF policy to protect against this attack?
- A. create a Container CNAF policy, targeted at a specific resource, check the box for XSS attack protection and set the action to alert
- B. create a Container CNAF policy, targeted at a specific resource, and they should set "Explicitly allowed inbound IP sources" to the IP address of the pod.
- C. create a Container CNAF policy, targeted at a specific resource, check the box for XSS attack protection and set the action to prevent
- D. create a Host CNAF policy targeted at a specific resource, check the box for XSS attack protection and set the action to "prevent"
正解:D
質問 # 38
How are the following categorized?
Backdoor account access Hijacked processes Lateral movement
Port scanning
- A. incidents
- B. admission controllers
- C. audits
- D. models
正解:A
質問 # 39
Which three types of classifications are available in the Data Security module? (Choose three.)
- A. Financial information
- B. Compliance standard
- C. Malicious IP
- D. Malware
- E. Personally identifiable information
正解:A、D、E
解説:
https://docs.paloaltonetworks.com/prisma/prisma-cloud/prisma-cloud-admin/prisma-cloud-data-security.html
質問 # 40
Which three serverless runtimes are supported by Prisma Cloud for vulnerability and compliance scans? (Choose three.)
- A. Node.js
- B. Dart
- C. Java
- D. Python
- E. Swift
正解:A、C、D
質問 # 41
Which Defender type performs registry scanning?
- A. Container
- B. RASP
- C. Serverless
- D. Host
正解:D
質問 # 42
Which two integrations enable ingesting host findings to generate alerts? (Choose two.)
- A. JIRA
- B. Tenable
- C. Qualys
- D. Splunk
正解:C、D
質問 # 43
Which three types of classifications are available in the Data Security module? (Choose three.)
- A. Financial information
- B. Malicious IP
- C. Malware
- D. Compliance standard
- E. Personally identifiable information
正解:A、D、E
解説:
https://docs.paloaltonetworks.com/prisma/prisma-cloud/prisma-cloud-admin/prisma-cloud-data-security.html In the Data Security module of Prisma Cloud, the classifications available focus on the types of sensitive data that need protection. These classifications include Personally Identifiable Information (PII), which involves data that can be used on its own or with other information to identify, contact, or locate a single person. Compliance standards pertain to data that must be protected to meet specific regulatory requirements, such as GDPR, HIPAA, or PCI-DSS. Financial information classification is concerned with data related to financial transactions, accounts, and credit card numbers, which are critical to secure due to their sensitive nature. These classifications are integral to data security strategies, ensuring that sensitive information is adequately protected according to its nature and the regulatory requirements governing it.
質問 # 44
The Prisma Cloud administrator has configured a new policy.
Which steps should be used to assign this policy to a compliance standard?
- A. Open the Compliance Standards section of the policy, and then save.
- B. Edit the policy, go to step 3 (Compliance Standards), click + at the bottom select the compliance standard, fill in the other boxes, and then click Confirm
- C. Custom policies cannot be added to existing standards.
- D. Create the Compliance Standard from Compliance tab. and then select Add to Policy.
正解:B
質問 # 45
Which three actions are required in order to use the automated method within Azure Cloud to streamline the process of using remediation in the identity and access management (IAM) module? (Choose three.)
- A. Configure IAM AWS remediation script.
- B. Install azure.servicebus & requests library.
- C. Integrate with Azure Service Bus.
- D. Install boto3 & requests library.
- E. Configure IAM Azure remediation script.
正解:B、C、E
解説:
To use the automated method within Azure Cloud for streamlining the process of using remediation in the identity and access management (IAM) module, the required actions include configuring the IAM Azure remediation script, integrating with Azure Service Bus, and installing the azure.servicebus & requests library. These steps ensure that the automated remediation system can communicate effectively with Azure services, execute the necessary remediation actions, and address IAM-related alerts by adjusting permissions and access controls as needed. This automation helps maintain a secure and compliant cloud environment by promptly addressing potential IAM issues.
質問 # 46
Which of the following is not a supported external integration for receiving Prisma Cloud Code Security notifications?
- A. ServiceNow
- B. Microsoft Teams
- C. Splunk
- D. Cortex XSOAR
正解:A
解説:
Prisma Cloud supports a wide range of external integrations for receiving Code Security notifications, including popular platforms like Splunk, Cortex XSOAR, and Microsoft Teams. These integrations facilitate seamless communication and automated workflows between Prisma Cloud and other operational tools, enhancing the security response capabilities. However, as of the current understanding, ServiceNow is primarily known for its capabilities in IT service management (ITSM) and incident management, and it might not be directly supported as an external integration specifically for Prisma Cloud Code Security notifications without custom configurations or additional integrations.
質問 # 47
What is the purpose of Incident Explorer in Prisma Cloud Compute under the "Monitor" section?
- A. To identify and suppress all audit events generated by the defender *
- B. To sort through large amounts of audit data manually in order to identify developing attacks
- C. To store large amounts of forensic data on the host where Console runs to enable a more rapid and effective response to incidents
- D. To correlate individual events to identify potential attacks and provide a sequence of process, file system, and network events for a comprehensive view of an incident
正解:D
解説:
The purpose of Incident Explorer in Prisma Cloud Compute under the "Monitor" section is to provide a comprehensive view of incidents by correlating individual events. This helps identify potential attacks through a sequence of processes, file system, and network events, thereby giving a complete picture of an incident's timeline and impact.
質問 # 48
An administrator sees that a runtime audit has been generated for a host.
The audit message is:
'Service postfix attempted to obtain capability SHELL by executing /bin/sh /usr/libexec/postfix/postfix-script stop. Low severity audit event is automatically added to the runtime mode'' Which runtime host policy rule is the root cause for this runtime audit?
- A. Custom rule with specific configuration for file integrity
- B. Default rule that alerts on suspicious runtime behavior
- C. Custom rule with specific configuration for networking
- D. Default rule that alerts on capabilities
正解:B
質問 # 49
Which of the following is displayed in the asset inventory?
- A. SSO users
- B. EC2 instances
- C. Federated users
- D. Asset tags
正解:B
解説:
The asset inventory in cloud security platforms like Prisma Cloud typically displays a wide range of cloud resources, including EC2 instances. EC2 instances are virtual servers in Amazon's Elastic Compute Cloud (EC2) for running applications on the Amazon Web Services (AWS) infrastructure. The asset inventory provides visibility into these instances, allowing security teams to monitor their configuration, security posture, and compliance status. This visibility is crucial for identifying misconfigurations, vulnerabilities, and ensuring that all EC2 instances adhere to the organization's security policies and compliance requirements.
質問 # 50
The development team is building pods to host a web front end, and they want to protect these pods with an application firewall.
Which type of policy should be created to protect this pod from Layer7 attacks?
- A. The development team should create a runtime policy with networking protections.
- B. The development team should create a WAAS rule targeted at all resources on the host.
- C. The development team should create a WAAS rule targeted at the image name of the pods.
- D. The development team should create a WAAS rule for the host where these pods will be running.
正解:B
質問 # 51
A Prisma Cloud administrator is tasked with pulling a report via API. The Prisma Cloud tenant is located on app2.prismacloud.io.
What is the correct API endpoint?
- A. httsp://api.prismacloud.cn
- B. https://api2.eu.prismacloud.io
- C. https://api2.prismacloud.io
- D. https://api.prismacloud.io
正解:D
質問 # 52
An S3 bucket within AWS has generated an alert by violating the Prisma Cloud Default policy "AWS S3 buckets are accessible to public". The policy definition follows:
config where cloud.type = 'aws' AND api.name='aws-s3api-get-bucket-acl' AND json.rule="((((acl.grants[? (@.grantee=='AllUsers')] size > 0) or policyStatus.isPublic is true) and publicAccessBlockConfiguration does not exist) or ((acl.grants[?(@.grantee=='AllUsers')] size > 0) and publicAccessBlockConfiguration.ignorePublicAcis is false) or (policyStatus.isPublic is true and publicAccessBlockConfiguration.restrictPublicBuckets is false)) and websiteConfiguration does not exist" Why did this alert get generated?
- A. network traffic to the S3 bucket
- B. configuration of the S3 bucket
- C. anomalous behaviors
- D. an event within the cloud account
正解:A
質問 # 53
Order the steps involved in onboarding an AWS Account for use with Data Security feature.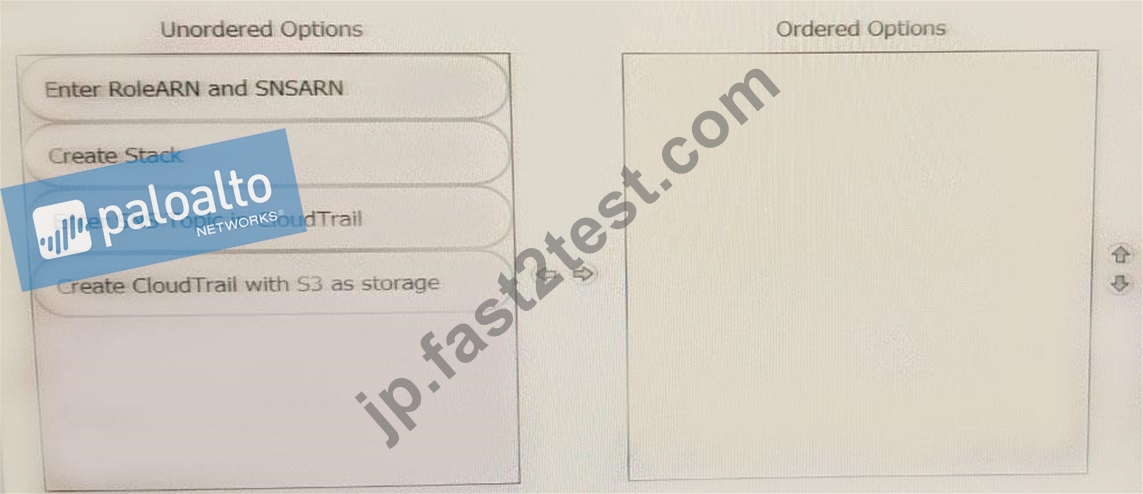
正解:
解説: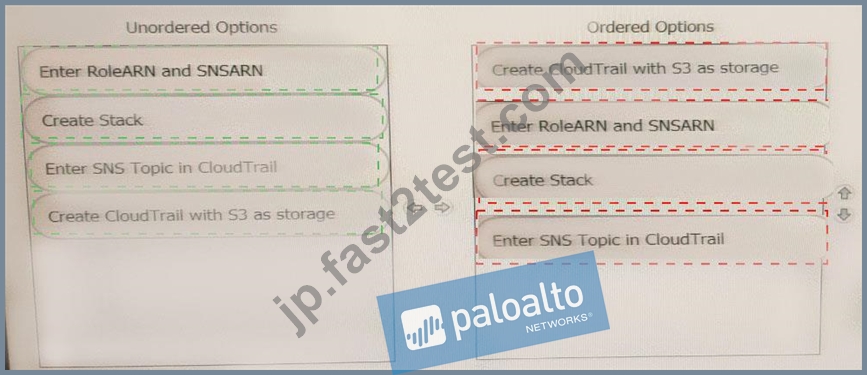
質問 # 54
......
有効な問題最新版を試そうPCCSEテスト解釈PCCSE有効な試験ガイド:https://jp.fast2test.com/PCCSE-premium-file.html
PCCSE試験資料Palo Alto Networks学習ガイド:https://drive.google.com/open?id=1JPPHy5e7qcMlK1BNihCiyygd728JvTiF