

[2025年07月18日] 問題集お試しセットSSE-Engineerテストエンジントレーニング問題集には54問あります
Palo Alto Networks SSE-Engineer問題集で100%カバー率リアル試験問題
質問 # 20
What is the purpose of embargo rules in Prisma Access?
- A. Blocking connections from specific countries
- B. Allowing traffic only from specific countries
- C. Blocking traffic from Russia. China, and North Korea only
- D. Rate-limiting connections originating from specific countries
正解:A
解説:
Embargo rules inPrisma Accessare designed toblock traffic from specific countriesthat are subject to regulatory or policy-based restrictions. These rules help organizations enforce compliance bypreventing inbound and outbound connectionsto or from regions that may pose security risks or arerestricted due to legal or geopolitical reasons. They are commonly used toalign with government sanctions and corporate security policies.
質問 # 21
Which statement applies when enabling multitenancy in Prisma Access (Managed by Panorama)?
- A. There is flexibility to manage different tenants using separate Panoramas, which allows for better organization and management of the multiple tenants.
- B. Service connection licenses will be assigned only to the first tenant, and these service connections can be shared with the other tenants.
- C. A single tenant cannot consist solely of mobile users or solely of remote networks.
- D. Each tenant is allocated its own dedicated Prisma Access instances, with compute resources that are not shared across tenants.
正解:D
解説:
When multitenancy is enabled in Prisma Access (Managed by Panorama), a key characteristic is the isolation of resources between tenants. Palo Alto Networks documentation emphasizes that each tenant operates within its own logically separate Prisma Access environment. This includes dedicated compute instances, ensuring that the performance and security of one tenant are not impacted by the activities of another.
Let's analyze why the other options are incorrect based on official documentation:
A: Service connection licenses will be assigned only to the first tenant, and these service connections can be shared with the other tenants. This statement is incorrect. In a multitenant Prisma Access deployment, licenses are typically managed and allocated per tenant. While the underlying infrastructure might be shared by Palo Alto Networks, the logical resources and often the licensing are segmented for each tenant. Sharing service connections across completely separate tenants would violate the principle of tenant isolation.
B: A single tenant cannot consist solely of mobile users or solely of remote networks. This statement is incorrect. Prisma Access multitenancy allows for flexibility in how tenants are configured. A tenant can be designed to exclusively serve mobile users, exclusively connect remote networks, or a combination of both, depending on the organizational structure and requirements.
D: There is flexibility to manage different tenants using separate Panoramas, which allows for better organization and management of the multiple tenants. While it is possible to have multiple Panorama instances managing different parts of a large infrastructure, when discussing multitenancy within a single Prisma Access instance (as implied by the question "enabling multitenancy in Prisma Access (Managed by Panorama))", all configured tenants are managed by that single Panorama instance. Managing different tenants with separate Panoramas is a different architectural consideration, not a defining characteristic of enabling multitenancy within one Prisma Access deployment managed by a specific Panorama.
Therefore, the defining characteristic of Prisma Access multitenancy (Managed by Panorama) is the allocation of dedicated Prisma Access instances and compute resources for each tenant, ensuring logical separation and resource isolation
質問 # 22
Which overlay protocol must a customer premises equipment (CPE) device support when terminating a Partner Interconnect-based Colo-Connect in Prisma Access?
- A. IPSec
- B. Geneve
- C. GRE
- D. DTLS
正解:A
解説:
When terminating aPartner Interconnect-based Colo-ConnectinPrisma Access, theCustomer Premises Equipment (CPE)must supportIPSecas the overlay protocol. Prisma Access establishes secureIPSec tunnels between theColo-Connect infrastructure and the CPE, ensuringencrypted communicationand reliable connectivity.IPSecprovidessecure site-to-cloud integration, enabling customers to extend their private network securely over the Prisma Access infrastructure.
質問 # 23
When configuring Remote Browser Isolation (RBI) with Prisma Access (Managed by Strata Cloud Manager), which element is required to define the protected URLs for mobile users?
- A. An RBI profile applied to the URL access management profile
- B. A Security policy with the target URL categories and set the action to "Isolate"
- C. A URL access management profile with site access set to "Isolate" applied to a Security policy
- D. A DNS Security profile applied to a Security policy with the action of "Isolate" for the target remote browser DNS categories
正解:C
解説:
When configuringRemote Browser Isolation (RBI)inPrisma Access (Managed by Strata Cloud Manager) for mobile users, aURL access management profilemust be created with thesite access action set to
"Isolate". This profile is thenapplied to a Security policyto enforce isolation for specific URLs. This ensures thatweb traffic to designated high-risk or untrusted sitesisredirected to a remote, secure browser instance, protecting endpoints from potential web-based threats.
質問 # 24
What must be configured to accurately report an application's availability when onboarding a discovered application for ZTNA Connector?
- A. icmp ping
- B. udp ping
- C. https ping
- D. tcp ping
正解:D
解説:
When onboarding a discovered application forZTNA Connector, configuring aTCP pingallows Prisma Access to accurately report the application'savailability.TCP ping(also known as aTCP connection check) verifies whether the application's service port isopen and responsive, ensuring that the application is reachable before allowing user connections. This method is more reliable thanICMP ping, as many cloud and SaaS applicationsblock ICMP trafficfor security reasons.
質問 # 25
How can an engineer use risk score customization in SaaS Security Inline to limit the use of unsanctioned SaaS applications by employees within a Security policy?
- A. Build an application filter using unsanctioned SaaS as the category.
- B. Build an application filter using unsanctioned SaaS as the characteristic.
- C. Increase the risk score for all SaaS applications to automatically block unwanted applications.
- D. Lower the risk score of sanctioned applications and increase the risk score for unsanctioned applications.
正解:D
解説:
SaaS Security Inline allows engineers to customize the risk scores assigned to different SaaS applications based on various factors. By manipulating these risk scores, you can influence how these applications are treated within Security policies.
To limit the use of unsanctioned SaaS applications:
* Lower the risk score of sanctioned applications:This makes them less likely to trigger policies designed to restrict high-risk activities.
* Increase the risk score of unsanctioned applications:This elevates their perceived risk, making them more likely to be caught by Security policies configured to block or limit access based on risk score thresholds.
Then, you would create Security policies that take action (e.g., block access, restrict features) based on these adjusted risk scores. For example, a policy could be configured to block access to any SaaS application with a risk score above a certain threshold, which would primarily target the unsanctioned applications with their inflated scores.
Let's analyze why the other options are incorrect based on official documentation:
* B. Increase the risk score for all SaaS applications to automatically block unwanted applications.
Increasing the risk score forallSaaS applications, including sanctioned ones, would lead to unintended blocking and disruption of legitimate business activities. Risk score customization is intended for differentiation, not a blanket increase.
* C. Build an application filter using unsanctioned SaaS as the category.While creating an application filter based on the "unsanctioned SaaS" category is a valid way to identify these applications, it directly filters based on the category itself, not the risk score. Risk score customization provides a more nuanced approach where you can define thresholds and potentially allow some low- risk activities within unsanctioned applications while blocking higher-risk ones.
* D. Build an application filter using unsanctioned SaaS as the characteristic.Similar to option C, using "unsanctioned SaaS" as a characteristic in an application filter allows you to directly target these applications. However, it doesn't leverage the risk score customization feature to control access based on a graduated level of risk.
Therefore, the most effective way to use risk score customization to limit unsanctioned SaaS application usage is by lowering the risk scores of sanctioned applications and increasing the risk scores of unsanctioned ones, and then building Security policies that act upon these adjusted risk scores.
質問 # 26
An intern is tasked with changing the Anti-Spyware Profile used for security rules defined in the GlobalProtect folder. All security rules are using the Default Prisma Profile. The intern reports that the options are greyed out and cannot be modified when selecting the Default Prisma Profile.
Based on the image below, which action will allow the intern to make the required modifications?
- A. Change the configuration scope to Prisma Access and modify the profile group.
- B. Create a new profile, because default profile groups cannot be modified.
- C. Request edit access for the GlobalProtect scope.
- D. Modify the existing anti-spyware profile, because best-practice profiles cannot be removed from a group.
正解:B
解説:
Palo Alto Networks best practices and the behavior of Strata Cloud Manager (SCM) dictate thatpredefined or default objects, including profile groups like "Default Prisma Profile," cannot be directly modified.
These default objects serve as baseline configurations and are often locked to prevent accidental or unintended changes that could impact the overall security posture.
The intern's experience of the options being greyed out when selecting "Default Prisma Profile" is a direct indication of this immutability of default objects.
Therefore, the correct action is to:
* Create a new Profile Group:The intern should create a new profile group within the appropriate configuration scope (likely GlobalProtect, given the task).
* Configure the new Profile Group:In this new profile group, the intern can select the desired Anti- Spyware Profile (which might be an existing custom profile or a new one they create).
* Modify Security Rules:The security rules currently using the "Default Prisma Profile" in the GlobalProtect folder need to be modified to use this newly created profile group.
Let's analyze why the other options are incorrect based on official documentation:
* A. Request edit access for the GlobalProtect scope.While having the correct scope permissions is necessary for makinganychanges within GlobalProtect, it will not override the inherent immutability of default objects like "Default Prisma Profile." Edit access will allow the intern to create new objects and modify rules, but not directly edit the default profile group.
* B. Change the configuration scope to Prisma Access and modify the profile group.The image shows that "Default Prisma Profile" has a "Location" of "Prisma Access." However, even within the Prisma Access scope, default profile groups are generally not directly editable. The issue is not the scope but the fact that it's a default object.
* D. Modify the existing anti-spyware profile, because best-practice profiles cannot be removed from a group.The question is about changing theprofile group, not the individual Anti-Spyware Profile. While "best-practice" profiles might be part of default groups, the core issue is the inability to modify thedefault groupitself. Creating a new group allows the intern to choose which Anti-Spyware Profile to include.
In summary, the fundamental principle in Palo Alto Networks management is that default objects are typically read-only to ensure a consistent and predictable baseline. To make changes, you need to create custom objects.
質問 # 27
A customer is implementing Prisma Access (Managed by Strata Cloud Manager) to connect mobile users, branch locations, and business-to- business (B2B) partners to their data centers.
* The solution must meet these requirements:
* The mobile users must have internet filtering, data center connectivity, and remote site connectivity to the branch locations.
* The branch locations must have internet filtering and data center connectivity.
* The B2B partner connections must only have access to specific data center internally developed applications running on non-standard ports.
* The security team must have access to manage the mobile user and access to branch locations.
* The network team must have access to manage only the partner access.
Which two components can be provisioned to enable data center connectivity over the internet? (Choose two.)
- A. Service connections
- B. ZTNA Connector
- C. SD-WAN Connector
- D. Colo-Connect
正解:A、D
解説:
Service connections enable secure connectivity between Prisma Access and on-premises data centers, allowing mobile users and branch locations to access internal applications. They facilitate seamless integration of internal networks with Prisma Access while maintaining security policies. Colo-Connect provides a dedicated and optimized pathway for traffic between Prisma Access and data centers, ensuring stable performance and reduced latency over the internet. Both components together support secure and efficient data center connectivity while aligning with the customer's access control and filtering requirements.
質問 # 28
A customer is implementing Prisma Access (Managed by Strata Cloud Manager) to connect mobile users, branch locations, and business-to- business (B2B) partners to their data centers.
The solution must meet these requirements:
The mobile users must have internet filtering, data center connectivity, and remote site connectivity to the branch locations.
The branch locations must have internet filtering and data center connectivity.
The B2B partner connections must only have access to specific data center internally developed applications running on non-standard ports.
The security team must have access to manage the mobile user and access to branch locations.
The network team must have access to manage only the partner access.
How should Prisma Access be implemented to meet the customer requirements?
- A. Deploy a Prisma Access instance with mobile users, remote networks, and private access for all connection types, and use the Prisma Access Configuration scope to manage all access.
- B. Deploy a Prisma Access instance with mobile users, remote networks, and private access for all connection types, and use the specific configuration scope for the connection type to manage access.
- C. Deploy two Prisma Access instances - the first with mobile users, remote networks, and private access for all internal connection types, and the second with remote networks and private application access for B2B connections - and use the Strata Multitenant Cloud Manager Prisma Access configuration scope to manage access.
- D. Deploy two Prisma Access instances - the first with mobile users, remote networks, and private access for all internal connection types, and the second with remote networks and private application access for B2B connections - and use the specific configuration scope for the connection type to manage access.
正解:D
解説:
To meet the customer's requirements, two separate Prisma Access instances should be deployed:
* Instance 1should includemobile users, remote networks, and private accessfor internal connectivity.
This ensures that mobile users can access the internet, data centers, and remote branch locations while enforcing security policies.
* Instance 2should be configured withremote networks and private application accessfor B2B connections. This instance will restrict access to only the required internally developed applications using non-standard ports, ensuring that partners cannot access other corporate resources.
By usingspecific configuration scopes for different connection types, the security team can manage access to mobile users and branch locations, while the network team can manage B2B partner connections. This ensuresproper segmentation of management responsibilitieswhile maintaining security and compliance.
質問 # 29
A customer using Prisma Access (Managed by Panorama) wants to monitor traffic patterns across all remote networks and use Strata Logging Service to gather insights on network usage. An engineer notices that some network data is missing from the Application Command Center (ACC).
What should the engineer do to ensure complete data visibility?
- A. Enable the Use Data for Pre-Defined Reports' setting in the Logging and Reporting configuration on Panorama.
- B. Verify that the Panorama web interface has been configured to aggregate logs from both the Panorama data and RN-SPNs.
- C. Reconfigure the Prisma Access remote networks to log directly to Panorama instead of using Strata Logging Service.
- D. Ensure that log forwarding profiles are applied to all Prisma Access policies and directed to Strata Logging Service.
正解:D
解説:
For complete data visibility inPrisma Access (Managed by Panorama),log forwarding profilesmust be applied toall security policiesto ensure that traffic logs are correctly sent toStrata Logging Service. If log forwarding is missing or misconfigured, some traffic data may not appear in theApplication Command Center (ACC), leading to incomplete insights. Verifying and correctly assigning log forwarding ensures that all relevant network activity is captured and available for analysis.
質問 # 30
A company has four branch offices between Canada Central and Canada East which use the same IPSec termination node and have QoS configured with customized bandwidth per site. An engineer wants to onboard a new branch office on the same IPSec termination node.
What is the QoS behavior for the new branch office?
- A. Automatically distributed to 20% for each site
- B. Cannot be added to existing QoS configuration
- C. Automatically distributed to 25% for each site
- D. Unallocated until manually assigned
正解:D
解説:
When onboarding a new branch office to anexisting IPSec termination nodeinPrisma Access, theQoS bandwidth is not automatically assigned. Instead, the newly added branchremains unallocateduntil the administratormanually assigns bandwidthwithin theQoS configuration settings. This ensures that customized bandwidth per siteremains intact and allows forfine-tuned traffic managementbased on business needs.
質問 # 31
Based on the image below, which two statements describe the reason and action required to resolve the errors? (Choose two.)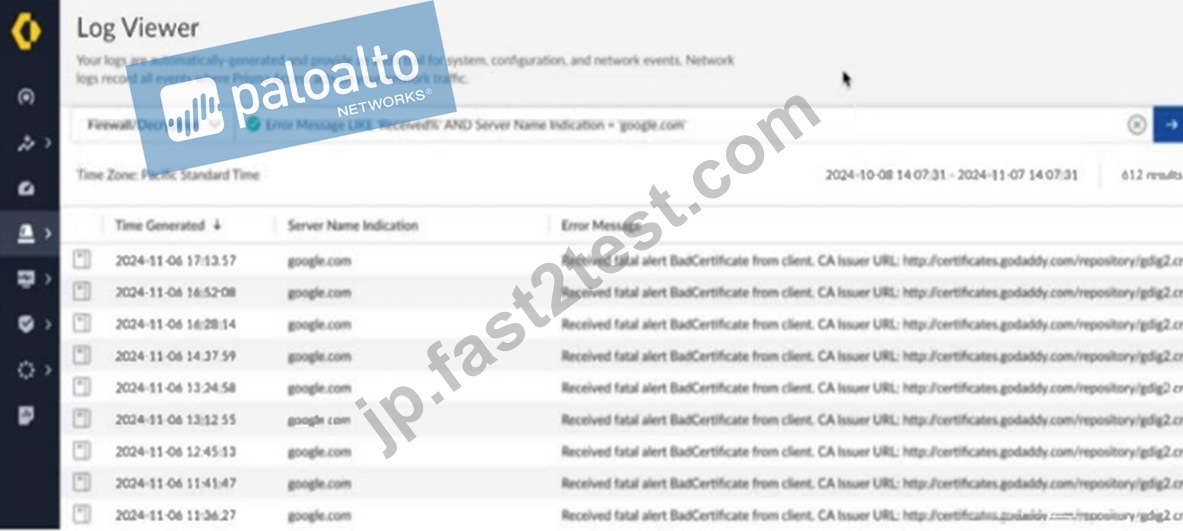
- A. The server has pinned certificates.
- B. Create a do not decrypt rule for the hostname "google.com."
- C. Create a do not decrypt rule for the hostname "certificates.godaddy.com."
- D. The client is misconfigured.
正解:A、B
解説:
The error messages indicate that Prisma Access is encountering certificate issues while attempting to decrypt traffic to "google.com." This suggests that theserver has pinned certificates, meaning it does not allow man- in-the-middle (MITM) decryption by Prisma Access. Since pinned certificates prevent traffic decryption, a solution is tocreate a "do not decrypt" rule for the hostname "google.com."This will allow traffic to flow without triggering certificate errors while maintaining secure communication with Google's servers.
質問 # 32
When using the traffic replication feature in Prisma Access, where is the mirrored traffic directed for analysis?
- A. Specified internal security appliance
- B. Panorama
- C. Dedicated cloud storage location
- D. Strata Cloud Manager (SCM)
正解:A
解説:
Palo Alto Networks documentation clearly states that when configuring the traffic replication feature in Prisma Access, you mustspecify an internal security applianceas the destination for the mirrored traffic.
This appliance, typically a Palo Alto Networks next-generation firewall or a third-party security tool, is responsible for receiving and analyzing the replicated traffic for various purposes like threat analysis, troubleshooting, or compliance monitoring.
Let's analyze why the other options are incorrect based on official documentation:
* B. Dedicated cloud storage location:While Prisma Access logs and other data might be stored in the cloud, themirrored trafficfor real-time analysis is directly streamed to a designated security appliance, not a passive storage location.
* C. Panorama:Panorama is the centralized management system for Palo Alto Networks firewalls. While Panorama can receive logs and manage the configuration of Prisma Access, it is not the direct destination for real-time mirrored traffic intended for immediate analysis.
* D. Strata Cloud Manager (SCM):Strata Cloud Manager is the platform used to configure and manage Prisma Access. It facilitates the setup of traffic replication, including specifying the destination appliance, but it does not directly receive or analyze the mirrored traffic itself.
Therefore, the mirrored traffic from the traffic replication feature in Prisma Access is directed to a specified internal security appliance for analysis.
質問 # 33
An engineer has configured IPSec tunnels for two remote network locations; however, users are experiencing intermittent connectivity issues across the tunnels.
What action will allow the engineer to receive notifications when the IPSec tunnels are down or experiencing instability?
- A. Set up the operational health dashboard to email alerts for remote Network IPSec tunnel issues.
- B. Select the IPSec tunnel monitoring and notifications checkbox when configuring the remote network IPSec tunnels.
- C. Create a new notification profile specifying conditions for remote network IPSec tunnels.
- D. Create a tunnel log notification rule to alert on specified remote network IPSec tunnel conditions.
正解:C
解説:
InPrisma Access, configuring anotification profileallows engineers to receive alerts when IPSec tunnels experience downtime or instability. By definingspecific conditions for remote network IPSec tunnels, the notification profile ensures that the engineer is proactively informed abouttunnel failures, flapping, or degraded performance. This approach enables timely troubleshooting and minimizes disruptions for users relying on the IPSec tunnels.
質問 # 34
Which statement is valid in relation to certificates used for GlobalProtect and pre-logon?
- A. The GlobalProtect agent may be used to distribute pre-logon certificates.
- B. The certificate used for pre-logon must include both Subject and Subject-Alt fields.
- C. Certificates must be deployed in the Machine Certificate Store.
- D. A public certificate authority (CA) must sign and validate all certificates used.
正解:C
解説:
ForGlobalProtect with pre-logon, certificates must beinstalled in the Machine Certificate Storeto ensure that authentication occursbefore user login. This allows the GlobalProtect client to establish aVPN connection before the user logs in, enabling access to corporate resources such as domain controllers and authentication services. Usingmachine certificatesensures secure authentication and eliminates dependency on user credentials at the pre-logon stage.
質問 # 35
A large retailer has deployed all of its stores with the same IP address subnet. An engineer is onboarding these stores as Remote Networks in Prisma Access. While onboarding each store, the engineer selects the
"Overlapping Subnets" checkbox.
Which Remote Network flow is supported after onboarding in this scenario?
- A. To mobile users
- B. To private applications
- C. To the internet
- D. To remote network
正解:B
解説:
When the "Overlapping Subnets" checkbox is selected during the Remote Network onboarding process in Prisma Access, the deployment enables Private Application access using Prisma Access for Users(ZTNA or Private Access). This feature is designed to handle scenarios where multiple sites use the same IP subnet by leveraging NAT (Network Address Translation) and segmentation to avoid conflicts.
Since overlapping subnets can create routing challenges for direct remote network-to-remote network communication, Prisma Access does not support Remote Network-to-Remote Network or Mobile User communication in this case. Private application access is supported as Prisma Access correctly routes requests based on application-layer intelligence rather than IP-based routing.
質問 # 36
How can an engineer verify that only the intended changes will be applied when modifying Prisma Access policy configuration in Strata Cloud Manager (SCM)?
- A. Select the most recent job under Operations > Push Status to view the pending changes that would apply to Prisma Access.
- B. Compare the candidate configuration and the most recent version under "Config Version Snapshots/
- C. Review the SCM portal for blue circular indicators next to each configuration menu item and ensure only the intended areas of configuration have this indicator.
- D. Open the push dialogue in SCM to preview all changes which would be pushed to Prisma Access.
正解:D
解説:
Palo Alto Networks documentation explicitly states that the"Preview Changes"functionality within the Strata Cloud Manager (SCM) push dialogue allows engineers to review a detailed summary of all modifications that will be applied to the Prisma Access configuration before committing the changes. This is the primary and most reliable method to ensure only the intended changes are deployed.
Let's analyze why the other options are incorrect based on official documentation:
* A. Review the SCM portal for blue circular indicators next to each configuration menu item and ensure only the intended areas of configuration have this indicator.While blue circular indicators might signify unsaved changes within a specific configuration section, they do not provide a comprehensive, consolidated view ofallpending changes across different policy areas. This method is insufficient for verifying the entirety of the intended modifications.
* B. Compare the candidate configuration and the most recent version under "Config Version Snapshots".While comparing configuration snapshots is a valuable method for understanding historical changes and potentially identifying unintended deviationsaftera push, it does not provide a real-time preview of thependingchanges before they are applied during the current modification session
* C. Select the most recent job under Operations > Push Status to view the pending changes that would apply to Prisma Access.The "Push Status" section primarily displays the status anddetails of completedorin-progresspush operations. It does not offer a preview of the changesbeforea push is initiated.
Therefore, the "Preview Changes" feature within the push dialogue is the documented and recommended method for an engineer to verify that only the intended changes will be applied when modifying Prisma Access policy configuration in Strata Cloud Manager (SCM).
質問 # 37
In addition to creating a Security policy, how can an AI Access Security be used to prevent users from uploading financial information to ChatGPT?
- A. Apply a vulnerability profile to stop attempts to exploit system flaws or gain unauthorized access to financial systems.
- B. Configure an Enterprise DLP rule to block uploads containing financial information.
- C. Add the ChatGPT domains using URL Filtering to block uploads containing financial information.
- D. Apply File Blocking to stop file uploads containing financial information.
正解:B
解説:
Palo Alto Networks AI Access Security integrates with Enterprise Data Loss Prevention (DLP) capabilities to control sensitive data within AI applications like ChatGPT. The most effective way to prevent users from uploading financial information is to:
* Define an Enterprise DLP rule:This rule would be configured to identify content that matches patterns or keywords associated with financial information (e.g., credit card numbers, bank account details, tax identifiers, financial statements).
* Apply the DLP rule to the AI Access Security policy:This policy would be specifically configured to inspect traffic to and from ChatGPT. When the DLP rule detects a user attempting to upload content containing financial information, it can take a defined action, such as blocking the upload.
Let's analyze why the other options are incorrect based on official documentation:
* A. Apply File Blocking to stop file uploads containing financial information.While File Blocking can prevent the upload of certain file types, it is not content-aware. It cannot inspect thecontentof a file to determine if it contains financial information. Therefore, it's not a granular or effective solution for this specific requirement.
* C. Add the ChatGPT domains using URL Filtering to block uploads containing financial information.URL Filtering controls access to specific websites or categories of websites. While you could potentially block access to ChatGPT entirely, it does not provide the capability to inspect the content being uploaded to a permitted domain and prevent the transfer of sensitive financial data.
* D. Apply a vulnerability profile to stop attempts to exploit system flaws or gain unauthorized access to financial systems.Vulnerability profiles are designed to detect and prevent attempts to exploit known security vulnerabilities in systems. They are not designed to inspect the content of user uploads for sensitive data like financial information. While importantfor overall security, they do not directly address the requirement of preventing financial data uploads to ChatGPT.
Therefore, configuring an Enterprise DLP rule within AI Access Security is the correct and most effective method to prevent users from uploading financial information to ChatGPT by inspecting the content of the uploads.
質問 # 38
How can a network security team be granted full administrative access to a tenant's configuration while restricting access to other tenants by using role-based access control (RBAC) for Panorama Managed Prisma Access in a multitenant environment?
- A. Create a custom role with Device Group and Template privileges and assign it to the security team's user accounts.
- B. Create an Access Domain and restrict access to only the Device Groups and Templates for the Target Tenant.
- C. Create a custom role enabling all privileges within the specific tenant's scope and assign it to the security team's user accounts.
- D. Set the administrative accounts for the security team to the "Superuser" role.
正解:B
解説:
In aPanorama Managed Prisma Access multitenant environment,Access Domainsprovide granularrole- based access control (RBAC). By defining anAccess Domain, the network security team can be granted full administrative privileges for aspecific tenant's configurationwhile ensuring theycannot access or modify other tenants. This method enforces proper segmentation andensures compliance with multitenant security policies.
質問 # 39
......
実際にあるSSE-Engineer問題集PDFで100%合格率保証付きます:https://jp.fast2test.com/SSE-Engineer-premium-file.html