

完全版は2024年最新のMS-102試験問題集テストガイドはトレーニング専門問題
試験準備と合格するための最高なカバー率問題集を提供しています これで試験準備せよMS-102
Microsoft MS-102 認定試験の出題範囲:
| トピック | 出題範囲 |
|---|---|
| トピック 1 |
|
| トピック 2 |
|
| トピック 3 |
|
| トピック 4 |
|
質問 # 94
You use Microsoft Defender for Endpoint.
You have the Microsoft Defender for Endpoint device groups shown in the following table
You plan to onboard computers to Microsoft Defender for Endpoint as shown in the following table.
正解:
解説: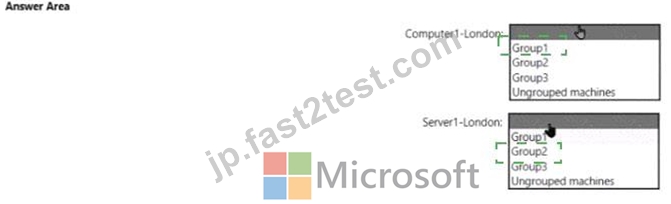
Explanation
質問 # 95
You have a Microsoft 365 subscription that uses an Azure AD tenant named contoso.com. The tenant contains the users shown in the following table.
From the Sign-ins blade of the Microsoft Entra admin center for which users can User1 and User2 view the sign-ins? To answer, select the appropriate options in the answer area.
NOTE: Each correct selection is worth one point.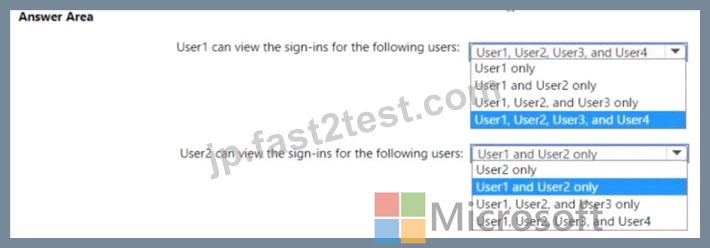
正解:
解説: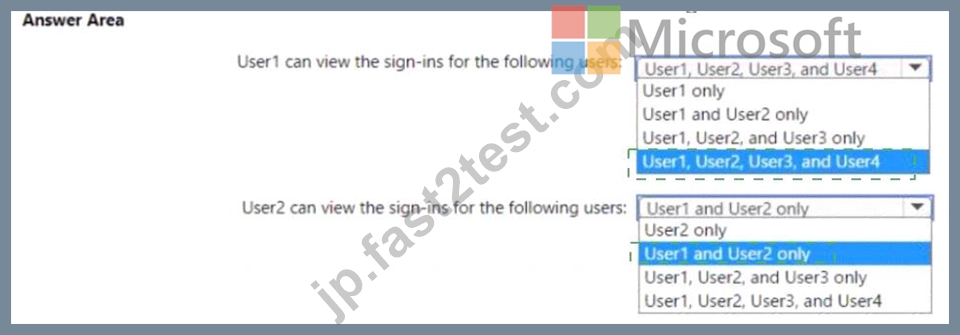
Explanation: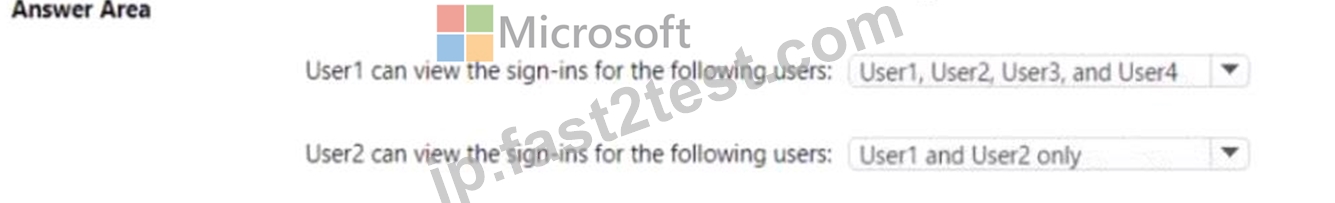
質問 # 96
You have a hybrid deployment of Azure AD that contains the users shown in the following table.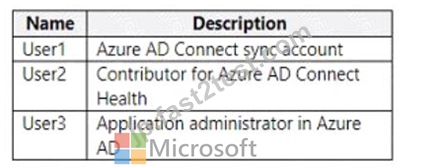
You need to identify which users can perform the following tasks:
* View sync errors in Azure AD Connect Health.
* Configure Azure AD Connect Health settings.
Which user should you identify for each task? To answer, select the appropriate options in the answer area.
NOTE: Each correct selection is worth one point.
正解:
解説: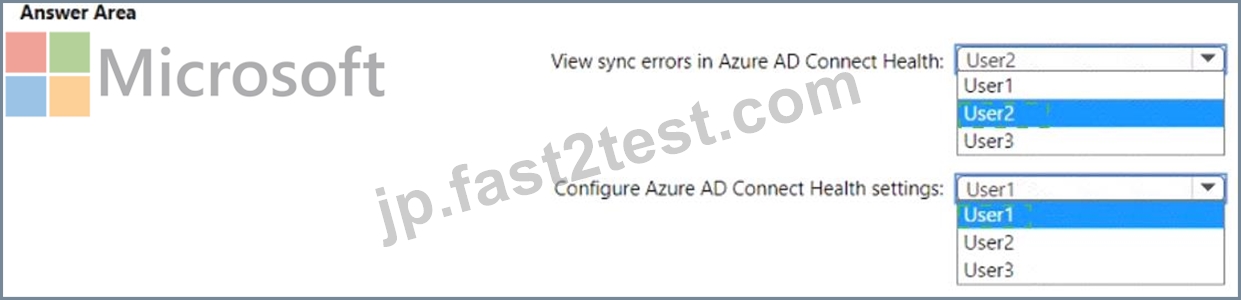
Explanation:
質問 # 97
You have a Microsoft 365 E5 subscription.
You plan to implement identity protection by configuring a sign-in risk policy and a user risk policy. Which type of risk is detected by each policy? To answer, select the appropriate options in the answer area.
NOTE: Each correct selection is worth one point.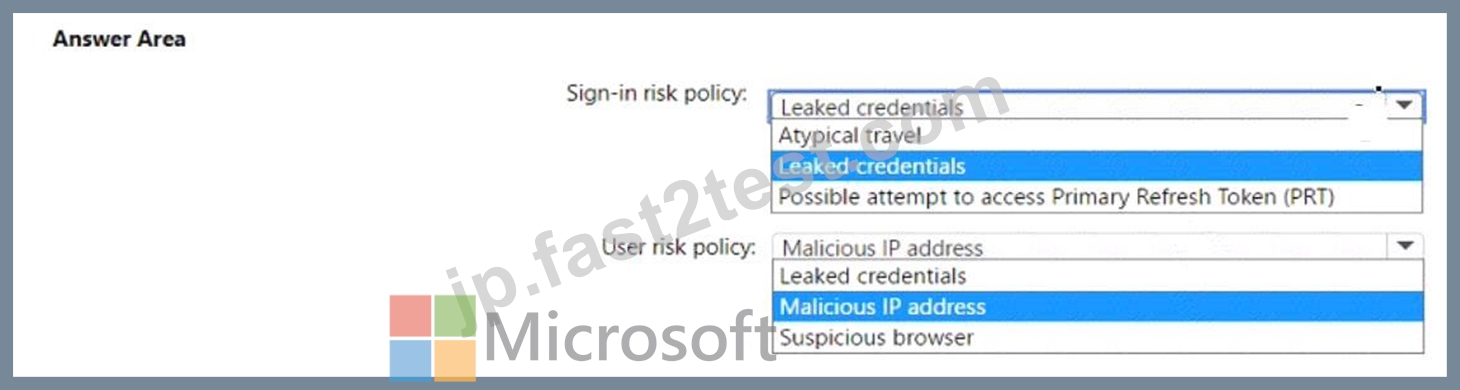
正解:
解説:
Explanation
質問 # 98
You have a Microsoft 365 E5 tenant that uses Microsoft Intune.
You need to configure Intune to meet the following requirements:
Prevent users from enrolling personal devices.
Ensure that users can enroll a maximum of 10 devices.
What should you use for each requirement? To answer, select the appropriate options in the answer area.
NOTE: Each correct selection is worth one point.
正解:
解説:
Explanation
Graphical user interface, text, application, chat or text message Description automatically generated
Reference:
https://docs.microsoft.com/en-us/mem/intune/enrollment/enrollment-restrictions-set#blocking-personal-windows
質問 # 99
You need to ensure that Admin4 can use SSPR.
Which tool should you use. and which action should you perform? To answer, select the appropriate options m the answer area.
NOTE: Each correct selection is worth one point.
正解:
解説: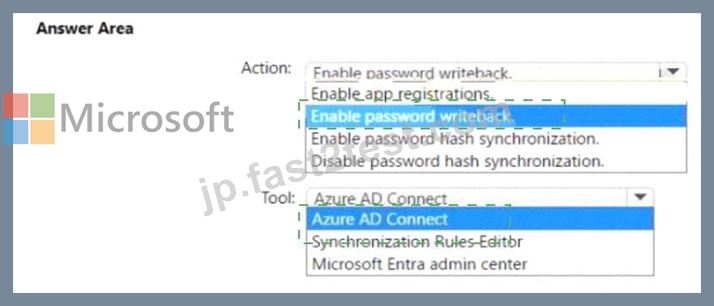
Explanation: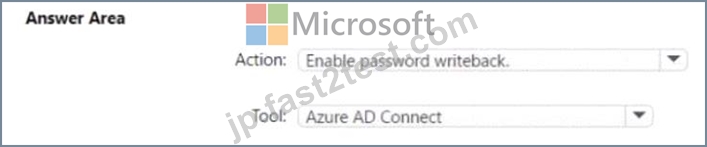
質問 # 100
HOTSPOT
You have a Microsoft 365 E5 subscription.
All company-owned Windows 11 devices are onboarded to Microsoft Defender for Endpoint.
You need to configure Defender for Endpoint to meet the following requirements:
* Block a vulnerable app until the app is updated.
* Block an application executable based on a file hash.
The solution must minimize administrative effort.
What should you configure for each requirement? To answer, select the appropriate options in the answer area.
NOTE: Each correct selection is worth one point.
正解:
解説:
Explanation:
Box 1: A remediation request
Block a vulnerable app until the app is updated.
Block vulnerable applications
How to block vulnerable applications
* Go to Vulnerability management > Recommendations in the Microsoft 365 Defender portal.
* Select a security recommendation to see a flyout with more information.
* Select Request remediation.
* Select whether you want to apply the remediation and mitigation to all device groups or only a few.
* Select the remediation options on the Remediation request page. The remediation options are software update, software uninstall, and attention required.
* Pick a Remediation due date and select Next.
* Under Mitigation action, select Block or Warn. Once you submit a mitigation action, it is immediately applied.
* Review the selections you made and Submit request. On the final page you can choose to go directly to the remediation page to view the progress of remediation activities and see the list of blocked applications.
Box 2: A file indicator
Block an application executable based on a file hash.
While taking the remediation steps suggested by a security recommendation, security admins with the proper permissions can perform a mitigation action and block vulnerable versions of an application. File indicators of compromise (IOC)s are created for each of the executable files that belong to vulnerable versions of that application. Microsoft Defender Antivirus then enforces blocks on the devices that are in the specified scope.
The option to View details of blocked versions in the Indicator page brings you to the Settings > Endpoints > Indicators page where you can view the file hashes and response actions.
Reference:
https://learn.microsoft.com/en-us/microsoft-365/security/defender-vulnerability-management/tvm-block-vuln-ap
質問 # 101
You have a Microsoft 365 E5 subscription that contains a Microsoft SharePoint site named Sitel. You need to perform the following tasks:
* Create a sensitive info type named SIT1 based on a regular expression.
* Add a watermark to all new documents that are matched by SIT1.
Which two settings should you use in the Microsoft Purview compliance portal? To answer, select the appropriate settings in the answer area.
NOTE: Each correct selection is worth one point.
正解:
解説: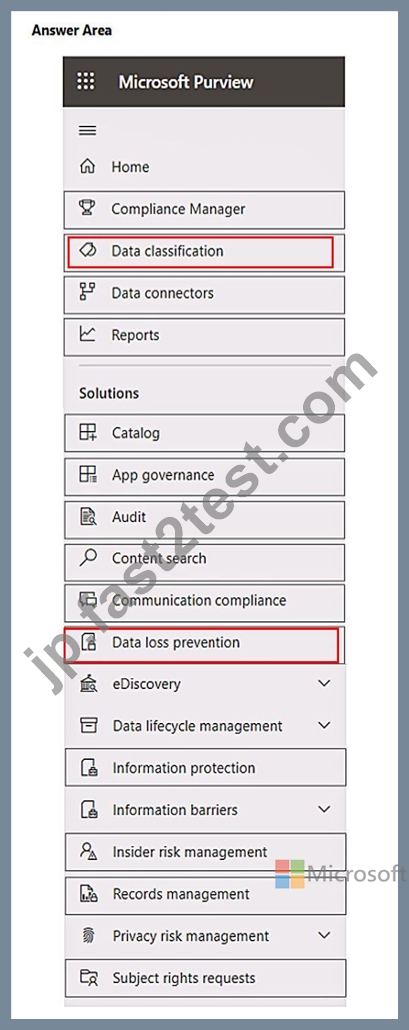
質問 # 102
HOTSPOT
You have a Microsoft 365 E3 subscription.
You plan to launch Attack simulation training for all users.
Which social engineering technique and training experience will be available? To answer, select the appropriate options in the answer area.
NOTE: Each correct selection is worth one point.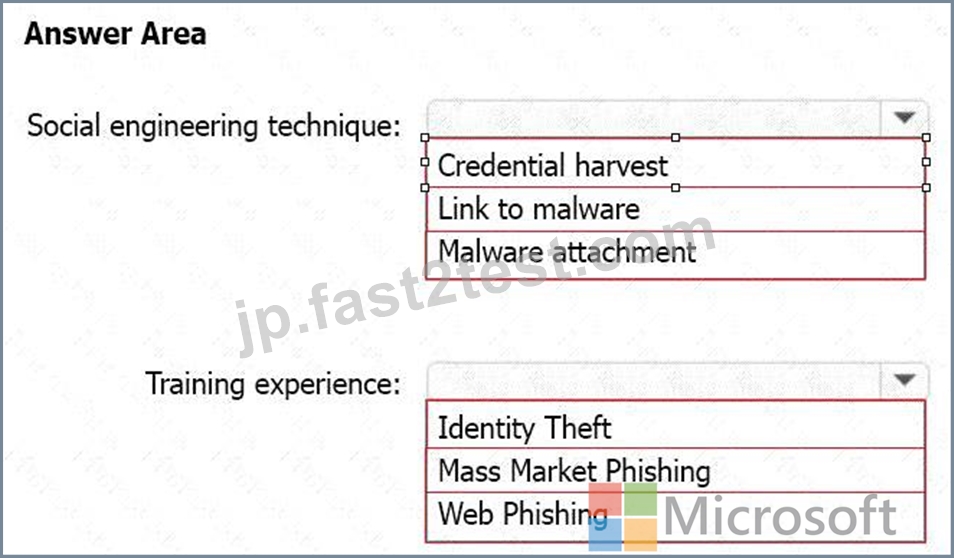
正解:
解説:
Box 1: Credential Harvest
Attack simulation training offers a subset of capabilities to E3 customers as a trial. The trial offering contains the ability to use a Credential Harvest payload and the ability to select 'ISA Phishing' or 'Mass Market Phishing' training experiences. No other capabilities are part of the E3 trial offering.
Note: In Attack simulation training, multiple types of social engineering techniques are available:
Credential Harvest
Malware Attachment
Link to Malware
Etc.
Box 2: Mass Market Phishing
Reference:
https://learn.microsoft.com/en-us/microsoft-365/security/office-365-security/attack-simulation-training-get-starte
質問 # 103
Your network contains an on-premises Active Directory domain. The domain contains the servers shown in the following table.
You purchase a Microsoft 365 E5 subscription.
You need to implement Azure AD Connect cloud sync.
What should you install first and on which server? To answer, select the appropriate options in the answer area.
NOTE: Each correct selection is worth one point.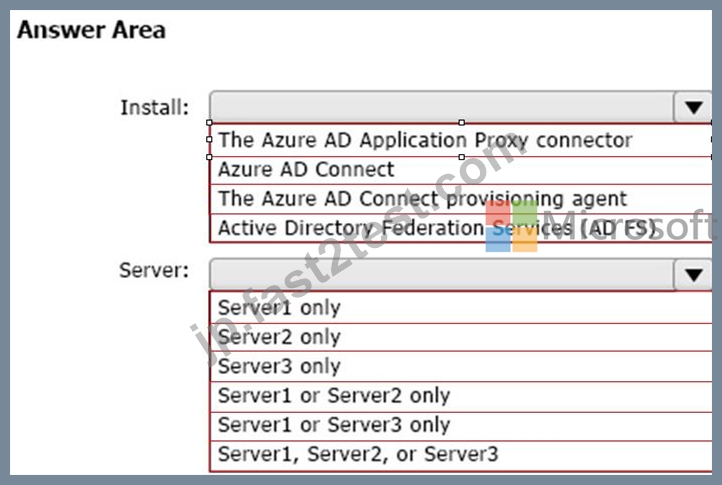
正解:
解説:
Reference:
https://docs.microsoft.com/en-us/azure/active-directory/cloud-sync/how-to-install
https://docs.microsoft.com/en-us/azure/active-directory/cloud-sync/how-to-prerequisites
質問 # 104
Your company has digitally signed applications.
You need to ensure that Microsoft Defender Advanced Threat Protection (Microsoft Defender ATP) considers the digitally signed applications safe and never analyzes them.
What should you create in the Microsoft Defender Security Center?
- A. an alert suppression rule
- B. an allowed/blocked list rule
- C. a custom detection rule
- D. an indicator
正解:D
解説:
Reference:
https://docs.microsoft.com/en-us/windows/security/threat-protection/microsoft-defender-atp/manage-indicators
質問 # 105
You have a Microsoft 365 E5 subscription.
You plan to implement Microsoft 365 compliance policies to meet the following requirements:
Identify documents that are stored in Microsoft Teams and SharePoint Online that contain Personally Identifiable Information (PII).
Report on shared documents that contain PII.
What should you create?
- A. an alert policy
- B. a Microsoft Cloud App Security policy
- C. a data loss prevention (DLP) policy
- D. a retention policy
正解:C
解説:
Reference:
https://docs.microsoft.com/en-us/microsoft-365/compliance/dlp-learn-about-dlp?view=o365-worldwide
質問 # 106
Note: This question is part of a series of questions that present the same scenario. Each question in the series contains a unique solution that might meet the stated goals. Some question sets might have more than one correct solution, while others might not have a correct solution.
After you answer a question in this section, you will NOT be able to return to it. As a result, these questions will not appear in the review screen.
Your network contains an Active Directory domain.
You deploy an Azure AD tenant.
Another administrator configures the domain to synchronize to Azure AD.
You discover that 10 user accounts in an organizational unit (OU) are NOT synchronized to Azure AD. All the other user accounts synchronized successfully.
You review Azure AD Connect Health and discover that all the user account synchronizations completed successfully.
You need to ensure that the 10 user accounts are synchronized to Azure AD.
Solution: You run idfix.exe and export the 10 user accounts.
Does this meet the goal?
- A. No
- B. Yes
正解:A
解説:
Explanation
The question states that "all the user account synchronizations completed successfully". If there were problems with the 10 accounts that needed fixing with idfix.exe, there would have been synchronization errors in Azure AD Connect Health.
It is likely that the 10 user accounts are being excluded from the synchronization cycle by a filtering rule.
Reference:
https://docs.microsoft.com/en-us/azure/active-directory/hybrid/how-to-connect-sync-configure-filtering
質問 # 107
HOTSPOT
You have a Microsoft 365 E5 subscription that contains the users shown in the following table.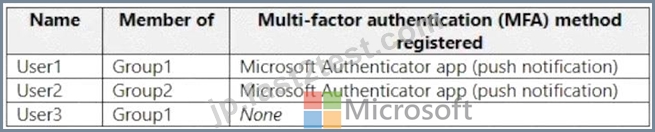
You configure the Microsoft Authenticator authentication method policy to enable passwordless authentication as shown in the following exhibit.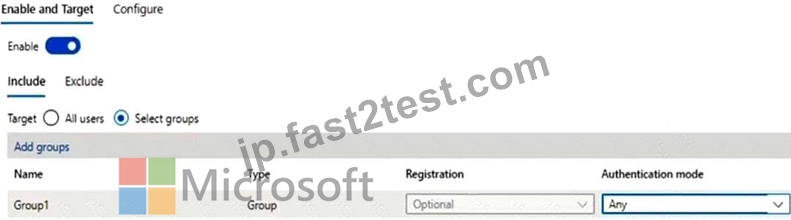
Both User1 and User2 report that they are NOT prompted for passwordless sign-in in the Microsoft Authenticator app.
For each of the following statements, select Yes if the statement is true. Otherwise, select No.
NOTE: Each correct selection is worth one point.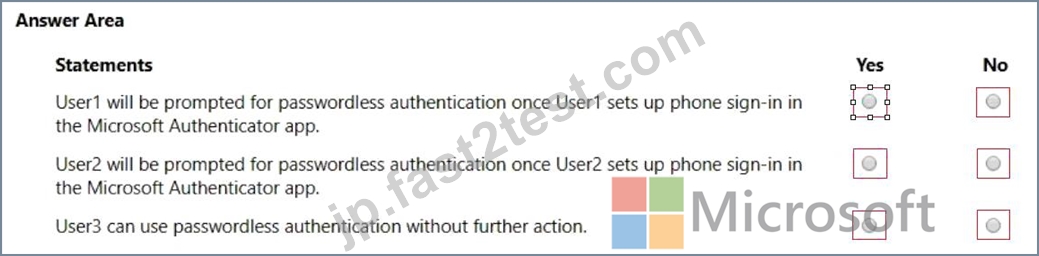
正解:
解説: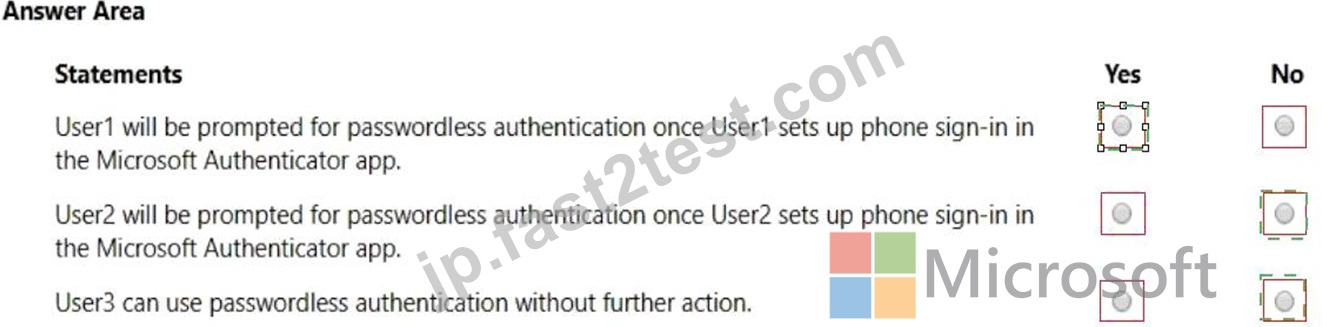
Explanation:
Box 1: Yes
User1 is member of Group1.
User1 has MFA registered method of Microsoft Authenticater app (push notification) The Microsoft Authenticator authentication method policy is configured for Group1, registration is optional, authentication method is any.
Note: Microsoft Authenticator can be used to sign in to any Azure AD account without using a password.
Microsoft Authenticator uses key-based authentication to enable a user credential that is tied to a device, where the device uses a PIN or biometric. Windows Hello for Business uses a similar technology.
This authentication technology can be used on any device platform, including mobile. This technology can also be used with any app or website that integrates with Microsoft Authentication Libraries.
Box 2: No
User2 is member of Group2.
The Microsoft Authenticator authentication method policy is configured for Group1, not for Group2.
Box 3: No
User3 is member of Group1.
User3 has no MFA method registered.
User3 must choose an authentication method.
Note: Enable passwordless phone sign-in authentication methods
Azure AD lets you choose which authentication methods can be used during the sign-in process. Users then register for the methods they'd like to use.
Reference:
https://learn.microsoft.com/en-us/azure/active-directory/authentication/howto-authentication-passwordless-phone
質問 # 108
You have a Microsoft 365 E5 subscription.
Several users have iOS devices.
You plan to enroll the iOS devices in Microsoft Endpoint Manager.
You need to ensure that you can create an iOS/iPadOS enrollment profile in Microsoft Endpoint Manager.
Which three actions should you perform in sequence? To answer, move the appropriate actions from the list of actions to the answer area and arrange them in the correct order.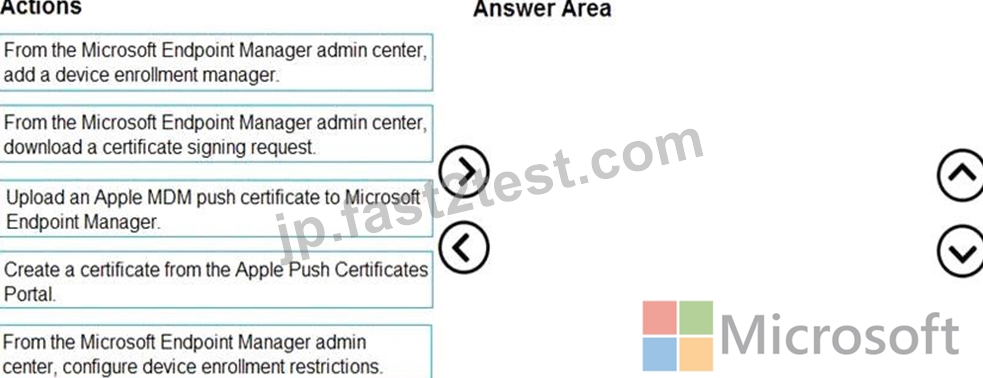
正解:
解説: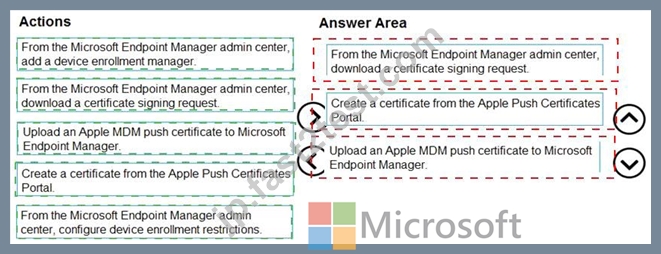
Explanation
Reference:
https://docs.microsoft.com/en-us/mem/intune/enrollment/apple-mdm-push-certificate-get
質問 # 109
Your company has a Microsoft 365 E5 tenant.
Users at the company use the following versions of Microsoft Office:
* Microsoft 365 Apps for enterprise
* Office for the web
* Office 2016
* Office 2019
The company currently uses the following Office file types:
* .docx
* .xlsx
* .doc
* xls
You plan to use sensitivity labels. You need to identify the following:
* Which versions of Office require an add-in to support the sensitivity labels.
* Which file types support the sensitivity labels.
What should you identify? To answer, select the appropriate options in the answer area, NOTE: Each correct selection is worth one point.
正解:
解説: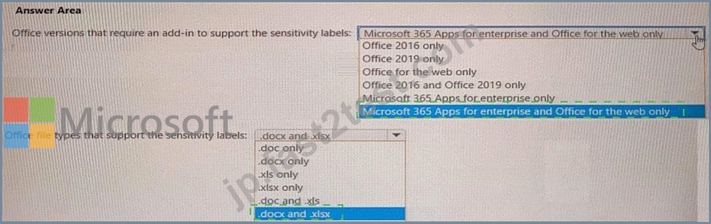
Explanation
質問 # 110
You have a Microsoft 365 E5 tenant that contains the devices shown in the following table.
You plan to implement attack surface reduction (ASR) rules. Which devices will support the ASR rules?
- A. Device3 only
- B. Device 1, Device2, and Device3 only
- C. Device1, Device2, Devices and Device4
- D. Device2 and Device3 only
正解:D
解説:
Reference:
https://docs.microsoft.com/en-us/microsoft-365/security/defender-endpoint/enable-attack-surface-reduction?view
質問 # 111
You have a Microsoft 365 E5 subscription that contains the users shown in the following table.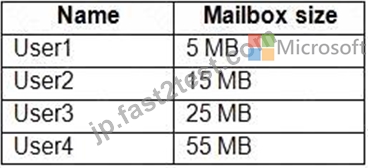
You have a Microsoft Office 365 retention label named Retention1 that is published to Exchange email.
You have a Microsoft Exchange Online retention policy that is applied to all mailboxes. The retention policy contains a retention tag named Retention2.
Which users can assign Retention1 and Retention2 to their emails? To answer, select the appropriate options in the answer area.
NOTE: Each correct selection is worth one point.
正解:
解説:
Explanation:
Graphical user interface, text, application, chat or text message Description automatically generated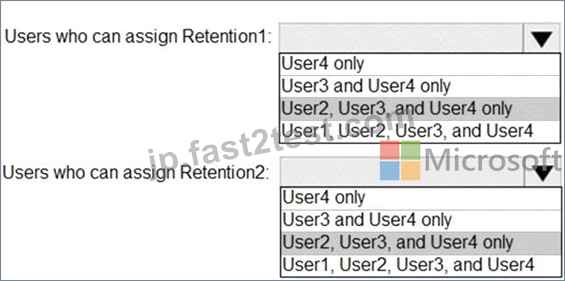
Reference:
https://docs.microsoft.com/en-us/microsoft-365/compliance/retention-policies-exchange?view=o365-worldwide
質問 # 112
You have a Microsoft 365 E5 tenant.
industry regulations require that the tenant comply with the ISO 27001 standard.
You need to evaluate the tenant based on the standard
- A. From Policy in the Azure portal, select Compliance, and then assign a pokey
- B. From the Microsoft 365 admin center enable the Productivity Score.
- C. From the Microsoft J6i compliance center, create an audit retention policy.
- D. From Compliance Manager, create an assessment
正解:D
質問 # 113
Your company has a Microsoft 365 subscription.
You need to identify all the users in the subscription who are licensed for Office 365 through a group membership. The solution must include the name of the group used to assign the license.
What should you use?
- A. Reports in Microsoft Purview compliance portal
- B. Active users in the Microsoft 365 admin center
- C. the Licenses blade in the Microsoft Entra admin center
- D. Reports in the Microsoft 365 admin center
正解:D
解説:
Explanation
Microsoft 365 Reports in the admin center
You can easily see how people in your business are using Microsoft 365 services. For example, you can identify who is using a service a lot and reaching quotas, or who may not need a Microsoft 365 license at all.
Which activity reports are available in the admin center
Depending on your subscription, here are the available reports in all environments.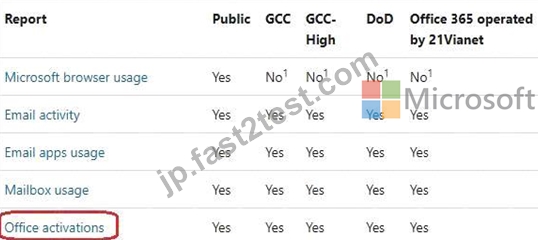
Reference:
https://learn.microsoft.com/en-us/microsoft-365/admin/activity-reports/activity-reports
質問 # 114
You have a Microsoft 365 E5 subscription.
You need to configure Microsoft Defender for Office 365 to meet the following requirements:
* A user's email sending patterns must be used to minimize false positives for spoof protection.
* Documents uploaded to Microsoft Teams, SharePoint Online, and OneDrive must be protected by using Defender for Office 365.
What should you configure for each requirement? To answer, select the appropriate options in the answer area.
NOTE: Each correct selection is worth one point.
正解:
解説:
Explanation:
質問 # 115
HOTSPOT
You have a Microsoft 365 E5 subscription that contains a Microsoft SharePoint Online site named Site1 and the users shown in the following table.
The devices are configured as shown in the following table.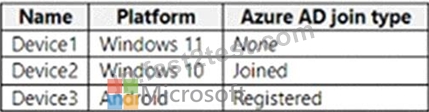
You have a Conditional Access policy named CAPolicy1 that has the following settings:
1.Assignments
Users or workload identities: Group1
Cloud apps or actions: Office 365 SharePoint Online
Conditions
- Filter for devices: Exclude filtered devices from the policy
- Rule syntax: device.displayName -startsWith "Device"
2.Access controls
Grant
- Grant: Block access
Session: 0 controls selected
3.Enable policy: On
For each of the following statements, select Yes if the statement is true. Otherwise, select No.
NOTE: Each correct selection is worth one point.
正解:
解説:
Explanation
Box 1: No
User1 is member of Group1 and has Device1.
Device1 is not Azure AD joined.
Note: Requiring a hybrid Azure AD joined device is dependent on your devices already being hybrid Azure AD joined.
Box 2: Yes
User2 is member of Group1 and has devices Device2 and Device3.
Device2 is Azure AD joined.
Device2 is excluded from CAPolicy1 (which would block access to Site1).
Box 3: Yes
User2 is member of Group1 and has devices Device2 and Device3.
Device3 is Android and is Azure AD registered.
Device3 is excluded from CAPolicy1 (which would block access to Site1).
Note: On Windows 7, iOS, Android, macOS, and some third-party web browsers, Azure AD identifies the device using a client certificate that is provisioned when the device is registered with Azure AD. When a user first signs in through the browser the user is prompted to select the certificate. The end user must select this certificate before they can continue to use the browser.
Reference:
https://learn.microsoft.com/en-us/azure/active-directory/devices/howto-hybrid-azure-ad-join
https://learn.microsoft.com/en-us/azure/active-directory/conditional-access/howto-conditional-access-policy-com
質問 # 116
You have a Microsoft 365 E5 subscription that uses Microsoft Intune and contains the devices shown in the following table.
You need to onboard Device1 and Device2 to Microsoft Defender for Endpoint.
What should you use to onboard each device? To answer, select the appropriate options in the answer area.
NOTE: Each correct selection is worth one point.
正解:
解説: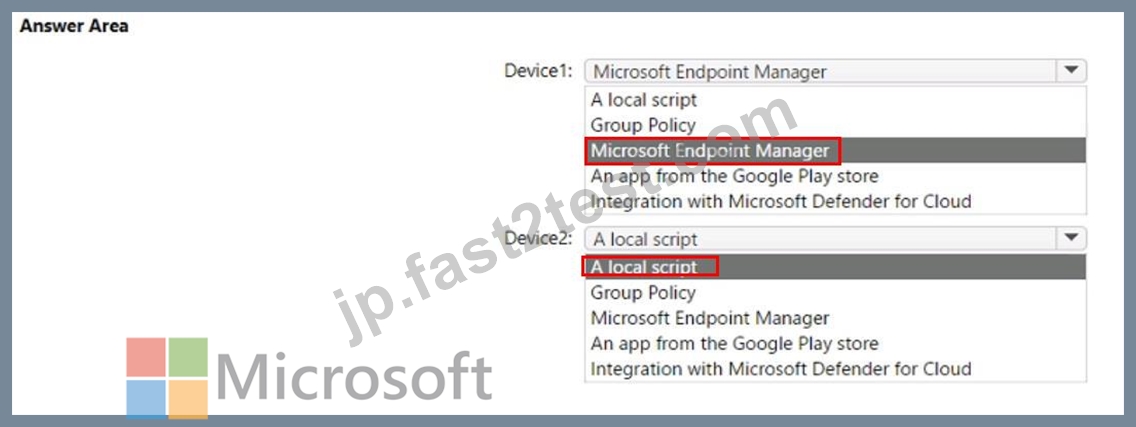
質問 # 117
......
検証された材料は決まってこれMS-102:https://jp.fast2test.com/MS-102-premium-file.html
合格するために必要なMS-102試験問題集:https://drive.google.com/open?id=15xSROu05xO7KzPqrpsA9LwfqV_LQT5Kn