

ベストな準備プラン350-201試験2023年最新のCyberOps Professional無制限141問題
注目すべき時短になる350-201オールインワン試験ガイド
Cisco 350-201 認定試験の出題範囲:
| トピック | 出題範囲 |
|---|---|
| トピック 1 |
|
| トピック 2 |
|
| トピック 3 |
|
| トピック 4 |
|
| トピック 5 |
|
| トピック 6 |
|
| トピック 7 |
|
質問 45
Refer to the exhibit.
IDS is producing an increased amount of false positive events about brute force attempts on the organization's mail server. How should the Snort rule be modified to improve performance?
- A. Change the rule content match to case sensitive
- B. Set the rule to track the source IP
- C. Block list of internal IPs from the rule
- D. Tune the count and seconds threshold of the rule
正解: A
質問 46
Refer to the exhibit.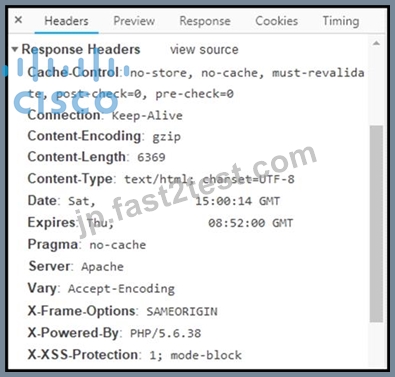
Where are the browser page rendering permissions displayed?
- A. Content-Type
- B. X-XSS-Protection
- C. X-Frame-Options
- D. Cache-Control
正解: A
質問 47
An engineer implemented a SOAR workflow to detect and respond to incorrect login attempts and anomalous user behavior. Since the implementation, the security team has received dozens of false positive alerts and negative feedback from system administrators and privileged users. Several legitimate users were tagged as a threat and their accounts blocked, or credentials reset because of unexpected login times and incorrectly typed credentials. How should the workflow be improved to resolve these issues?
- A. Change the SOAR configuration flow to remove the automatic remediation that is increasing the false positives and triggering threats
- B. Increase incorrect login tries and tune anomalous user behavior not to affect privileged accounts
- C. Meet with privileged users to increase awareness and modify the rules for threat tags and anomalous behavior alerts
- D. Add a confirmation step through which SOAR informs the affected user and asks them to confirm whether they made the attempts
正解: A
質問 48
An engineer is moving data from NAS servers in different departments to a combined storage database so that the data can be accessed and analyzed by the organization on-demand. Which data management process is being used?
- A. data regression
- B. data clustering
- C. data ingestion
- D. data obfuscation
正解: B
質問 49 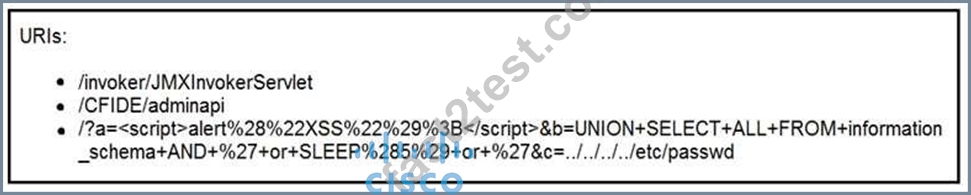
Refer to the exhibit. At which stage of the threat kill chain is an attacker, based on these URIs of inbound web requests from known malicious Internet scanners?
- A. actions on objectives
- B. delivery
- C. exploitation
- D. reconnaissance
正解: B
解説:
Explanation/Reference: https://www2.deloitte.com/content/dam/Deloitte/sg/Documents/risk/sea-risk-cyber-101-july2017.pdf
質問 50
A threat actor has crafted and sent a spear-phishing email with what appears to be a trustworthy link to the site of a conference that an employee recently attended. The employee clicked the link and was redirected to a malicious site through which the employee downloaded a PDF attachment infected with ransomware. The employee opened the attachment, which exploited vulnerabilities on the desktop. The ransomware is now installed and is calling back to its command and control server. Which security solution is needed at this stage to mitigate the attack?
- A. web security solution
- B. email security solution
- C. endpoint security solution
- D. network security solution
正解: D
質問 51
What is a limitation of cyber security risk insurance?
- A. It does not cover the costs to hire forensics experts to analyze the cyber attack
- B. It does not cover the costs to hire a public relations company to help deal with a cyber attack
- C. It does not cover the costs to restore stolen identities as a result of a cyber attack
- D. It does not cover the costs of damage done by third parties as a result of a cyber attack
正解: C
質問 52
Drag and drop the components from the left onto the phases of the CI/CD pipeline on the right.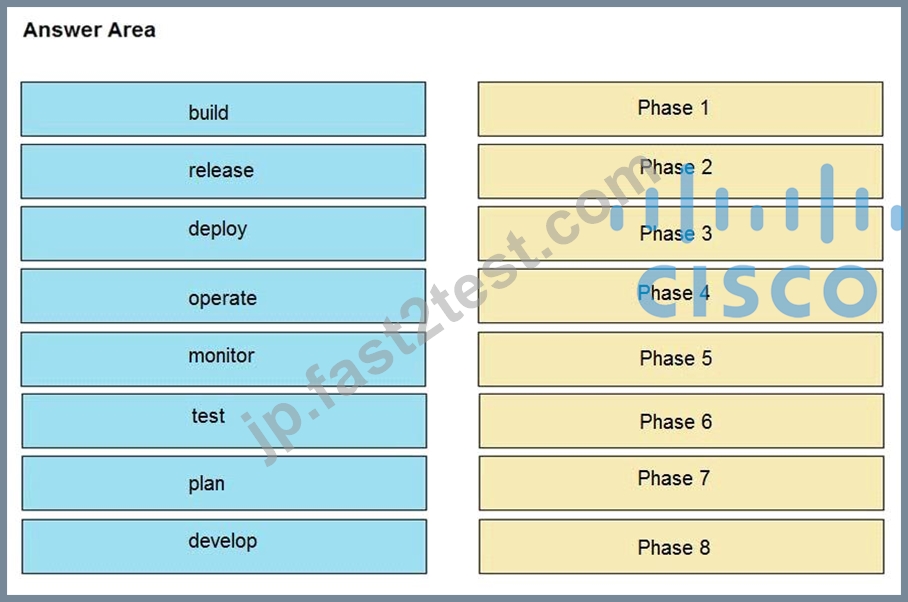
正解:
解説:
Reference:
https://www.densify.com/resources/continuous-integration-delivery-phases
質問 53
An engineer has created a bash script to automate a complicated process. During script execution, this error occurs: permission denied. Which command must be added to execute this script?
- A. sh ex.sh
- B. chroot ex.sh
- C. chmod +x ex.sh
- D. source ex.sh
正解: C
質問 54
Refer to the exhibit.
Where does it signify that a page will be stopped from loading when a scripting attack is detected?
- A. x-content-type-options
- B. x-frame-options
- C. x-test-debug
- D. x-xss-protection
正解: D
質問 55
What is a principle of Infrastructure as Code?
- A. Comprehensive initial designs support robust systems
- B. Scripts and manual configurations work together to ensure repeatable routines
- C. System maintenance is delegated to software systems
- D. System downtime is grouped and scheduled across the infrastructure
正解: A
質問 56
An engineer notices that unauthorized software was installed on the network and discovers that it was installed by a dormant user account. The engineer suspects an escalation of privilege attack and responds to the incident. Drag and drop the activities from the left into the order for the response on the right.
正解:
解説:
質問 57 
Refer to the exhibit. What results from this script?
- A. A search is conducted for additional seeds
- B. Seeds for existing domains are checked
- C. Domains are compared to seed rules
- D. A list of domains as seeds is blocked
正解: A
質問 58
Refer to the exhibit.
Where is the MIME type that should be followed indicated?
- A. x-content-type-options
- B. x-xss-protection
- C. x-test-debug
- D. strict-transport-security
正解: C
質問 59
How is a SIEM tool used?
- A. To compare security alerts against configured scenarios and trigger system responses
- B. To collect and analyze security data from network devices and servers and produce alerts
- C. To collect security data from authentication failures and cyber attacks and forward it for analysis
- D. To search and compare security data against acceptance standards and generate reports for analysis
正解: B
質問 60
A security incident affected an organization's critical business services, and the customer-side web API became unresponsive and crashed. An investigation revealed a spike of API call requests and a high number of inactive sessions during the incident. Which two recommendations should the engineers make to prevent similar incidents in the future? (Choose two.)
- A. Configure shorter timeout periods.
- B. Automate server-side error reporting for customers.
- C. Implement API key maintenance.
- D. Decrease simultaneous API responses.
- E. Determine API rate-limiting requirements.
正解: B,E
質問 61
Drag and drop the actions below the image onto the boxes in the image for the actions that should be taken during this playbook step. Not all options are used.
正解:
解説:
質問 62
A security manager received an email from an anomaly detection service, that one of their contractors has downloaded 50 documents from the company's confidential document management folder using a company- owned asset al039-ice-4ce687TL0500. A security manager reviewed the content of downloaded documents and noticed that the data affected is from different departments. What are the actions a security manager should take?
- A. Report to the incident response team.
- B. Communicate with the contractor to identify the motives.
- C. Escalate to contractor's manager.
- D. Measure confidentiality level of downloaded documents.
正解: A
質問 63
An engineer returned to work and realized that payments that were received over the weekend were sent to the wrong recipient. The engineer discovered that the SaaS tool that processes these payments was down over the weekend. Which step should the engineer take first?
- A. Contact the incident response team to inform them of a potential breach
- B. Utilize the SaaS tool team to gather more information on the potential breach
- C. Request that the purchasing department creates and sends the payments manually
- D. Organize a meeting to discuss the services that may be affected
正解: B
質問 64
An organization had an incident with the network availability during which devices unexpectedly malfunctioned. An engineer is investigating the incident and found that the memory pool buffer usage reached a peak before the malfunction. Which action should the engineer take to prevent this issue from reoccurring?
- A. Enable memory tracing notifications.
- B. Enable memory threshold notifications.
- C. Disable memory limit.
- D. Disable CPU threshold trap toward the SNMP server.
正解: B
質問 65
What is the HTTP response code when the REST API information requested by the authenticated user cannot be found?
- A. 0
- B. 1
- C. 2
- D. 3
- E. 4
正解: A
解説:
Explanation
Explanation/Reference: https://airbrake.io/blog/http-errors/401-unauthorized-error#:~:text=The%20401%20Unauthorized%
20Error%20is,client%20could%20not%20be%20authenticated.
質問 66
......
合格保証付き350-201問題集:https://jp.fast2test.com/350-201-premium-file.html
あなたを合格さすCisco 350-201試験専門はここにある:https://drive.google.com/open?id=1NDniYG62HtcQaczoM5mRkuFPj2EfgNoY